

Maximum of 25 job preferences reached.
Top Cyber Security Jobs in Washington, DC

18 Days AgoSaved
Aerospace • Information Technology • Professional Services • Security • Software
Leads cybersecurity accreditation and authorization activities for government systems. Documents security controls, architectures, SSPs, CONOPS, contingency plans, user guides, SOPs, and POA&M mitigations. Coordinates with system owners, project managers, engineers, contractors, and customer security organizations to secure ATD, IATT, and ATO approvals. Monitors project status, supports audits and compliance oversight, updates security plans based on emerging threats and policy, and recommends process improvements.
Top Skills:
Authority To Operate (Ato)Authority To Test (Att)ConopsDod 8570.01-MIcd 503Information System SecurityPlan Of Action And Milestones (Poa&M)Risk Management Framework (Rmf)Security Control AssessmentsSecurity Plans (Ssp)
Cloud • Security • Software • Cybersecurity • Automation
Conduct advanced application security research across GitLab’s DevSecOps and AI-powered platforms. Identify and exploit novel, systemic, and chained vulnerabilities; develop proof-of-concept exploits, testing methodologies, and research automation; assess AI attack vectors and open-source dependencies; drive remediation and security improvements; advise engineering teams, contribute to roadmaps, mentor researchers, and share findings with the security community.
Top Skills:
Duo Agent PlatformGitlabGitlab DuoGoPythonRubyRustTypescript
Cloud • Security • Software • Cybersecurity • Automation
Conducts advanced application security research across GitLab’s DevSecOps and AI-powered platforms. Responsibilities include discovering and exploiting systemic vulnerabilities, penetration testing, developing proof-of-concept exploits, researching AI and agentic security threats, building automated research tooling, coordinating remediation, mentoring security professionals, and communicating findings to engineering and security communities.
Top Skills:
Ai FrameworksDevsecopsDuo Agent PlatformGitlabGitlab Duo ChatGoPythonRubyRustTypescript
Information Technology • Consulting • Defense
Establish and operationalize DHS OIG data governance and cybersecurity authorization frameworks for AI and analytics platforms. Responsibilities include developing governance policies, metadata standards, stewardship workflows, RBAC designs, data lineage, SSPs, POA&Ms, architecture documentation, privacy inputs, and continuous monitoring evidence. The role supports ATO processes, NIST/FedRAMP compliance, AI governance, data quality assessments, and protection of sensitive investigative and law-enforcement data in Azure Government environments.
Top Skills:
AlationAws GovcloudAzure Commercial/GccAzure GovernmentAzure PurviewCollibraFedrampFismaLucidchartNist 800-53RbacVisio
Information Technology • Consulting • Defense
Designs and maintains security controls for AI platforms, data environments, applications, and cloud infrastructure supporting DHS OIG. Responsibilities include RBAC, encryption, logging, SIEM integration, security monitoring, vulnerability assessments, penetration testing coordination, secure code review, ATO support, NIST and FedRAMP compliance, incident response, forensic analysis, and security documentation. The role requires Azure cloud security expertise, federal cybersecurity experience, and the ability to obtain DHS/EOD clearance.
Top Skills:
AWSAzureAzure AdAzure GovernmentEntra IdFedrampFismaGCPNist 800-53Owasp Top 10SIEM

Reposted 19 Days AgoSaved
Aerospace • Information Technology • Security • Cybersecurity • Defense
Assess and document cybersecurity controls across federal information systems, coordinate remediation with system stakeholders, and oversee RMF activities throughout the system authorization lifecycle. Guide categorization, control selection, implementation, assessment, continuous monitoring, risk documentation, audit support, and incident response. Serve as a senior technical cybersecurity advisor, communicate risks and metrics to leadership, and provide security guidance and training while maintaining alignment with NIST and DoD requirements.
Top Skills:
Ccnp EnterpriseCehCismCisspCissp-IssapCissp-IssepCloud ComputingDod 8140.03GciaGdsaGicspNist Risk Management Framework (Rmf)

Information Technology • Professional Services • Defense • Manufacturing
Performs IT general controls testing, control design and effectiveness assessments, financial systems security assessments, benchmarking, remediation planning, and compliance evaluations. Supports NIST, DHS, OMB, DISA, and federal internal-control requirements while collaborating with technical teams and stakeholders. Reports security risks and mitigation strategies, assists with annual ITGC scoping, and supports related assessments and authorizations to operate.
Top Skills:
Dhs 4300ADhs Control Evaluation Matrix (Cem)Disa StigsIt General Controls (Itgc)Nist 800-53 Rev. 5Omb A-123Poa&M
Artificial Intelligence • Cybersecurity • Quantum Computing • Defense
Manages federal information-system security authorization and Risk Management Framework activities, including FISMA-compliant security packages, POA&Ms, risk analyses, control assessments, continuous monitoring, incident response, contingency planning, inventories, vulnerability scans, and stakeholder coordination. Supports NIST, OMB, CNSS, and privacy requirements for a law-enforcement customer, while validating physical safeguards and developing assessment scripts and technical reports.
Top Skills:
Cnss 1253CsamCustom Assessment ScriptsDatabasesFedrampFips 140Fips 199Fips 200Fips 201FismaLinuxNessusNetwork ProtocolsNetwork Security ArchitectureNist RmfNist Sp 800-37Nist Sp 800-53Nist Sp 800-53AOmb Circular A-123Omb Circular A-130QualysRoutersServicenowSwitchesUnixVulnerability Assessment ToolsWeb ServersWindows
Blockchain • Financial Services • Cryptocurrency • Web3
Own product and protocol security across Jito’s Solana-based products. Responsibilities include threat modeling, secure design and code reviews, deployment hardening, internal audits, onchain monitoring, bug bounty operations, remediation tracking, AI-assisted security testing, and key and asset risk management. The role requires production software engineering experience, strong application security expertise, security automation skills, and familiarity with Web3, crypto, or DeFi.
Top Skills:
BlockaidC++Formal VerificationFuzzingGoHardware Security ModulesHypernativeMultisigProperty-Based TestingPythonRustSmart ContractsSolanaSvmTrusted Execution Environments
Artificial Intelligence • Cybersecurity • Quantum Computing • Defense
Performs cloud security engineering across AWS and GCP, including system hardening, vulnerability remediation, compliance scanning, cloud operations, security tooling, incident response, and troubleshooting across infrastructure and identity layers. Supports FedRAMP, FISMA, and NIST 800-53 environments, participates in a 24×7 on-call rotation, maintains technical documentation, communicates with customers, and mentors junior engineers.
Top Skills:
Active DirectoryAcunetixAnchoreAnsibleAppgateAWSCis BenchmarksCloud SqlCloud StorageCloudFormationCompute EngineDevsecopsDisa StigsEbsEc2FedrampFismaGitlabGoogle Cloud Platform (Gcp)IamInvictiJIRAKubernetesLinuxNessusNist 800-53OktaOpenscapPalo Alto Networks FirewallsRdsS3ServicenowSplunk EnterpriseTenable Security CenterTerraformTrend Micro Deep SecurityTrivyTwistlockWindowsWorkspaces
Reposted 10 Days AgoSaved
Aerospace • Information Technology • Professional Services • Security • Software
Provides information security support for federal healthcare systems, including security architecture reviews, firewall and infrastructure initiatives, security impact assessments, mitigating controls, system security plans, SOPs, and POA&M remediation. Advises development teams and customer security organizations on federal security requirements, emerging practices such as Zero Trust and SBOM, network monitoring, authentication, and data security. The role is remote and requires passing an IHS background check for Public Trust eligibility.
Top Skills:
Agile SdlcData Security AdministrationDigital SignaturesFips 199Fips 200FirewallsHhs EplcIt SecurityNetwork Configuration And MonitoringNist 800-53RpmsSbomSource Code ControlUser AuthenticationVersion Management SoftwareVistaZero Trust

Healthtech
Builds and operates cloud security controls across AWS, Azure, GovCloud, and other platforms. Responsibilities include IAM, encryption, secrets management, preventive and detective controls, PHI protection, logging pipelines, Terraform automation, security remediation, audit evidence, and compliance support for HIPAA, HITRUST, SOC 2, and FedRAMP.
Top Skills:
AWSAws GovcloudAzureCi/CdCloud-Native Security ServicesEncryptionFedrampHipaaHitrustIamKmsNist 800-53ScpsSecrets ManagementSIEMSoc 2Terraform
New
Cut your apply time in half.
Use ourAI Assistantto automatically fill your job applications.
Use For Free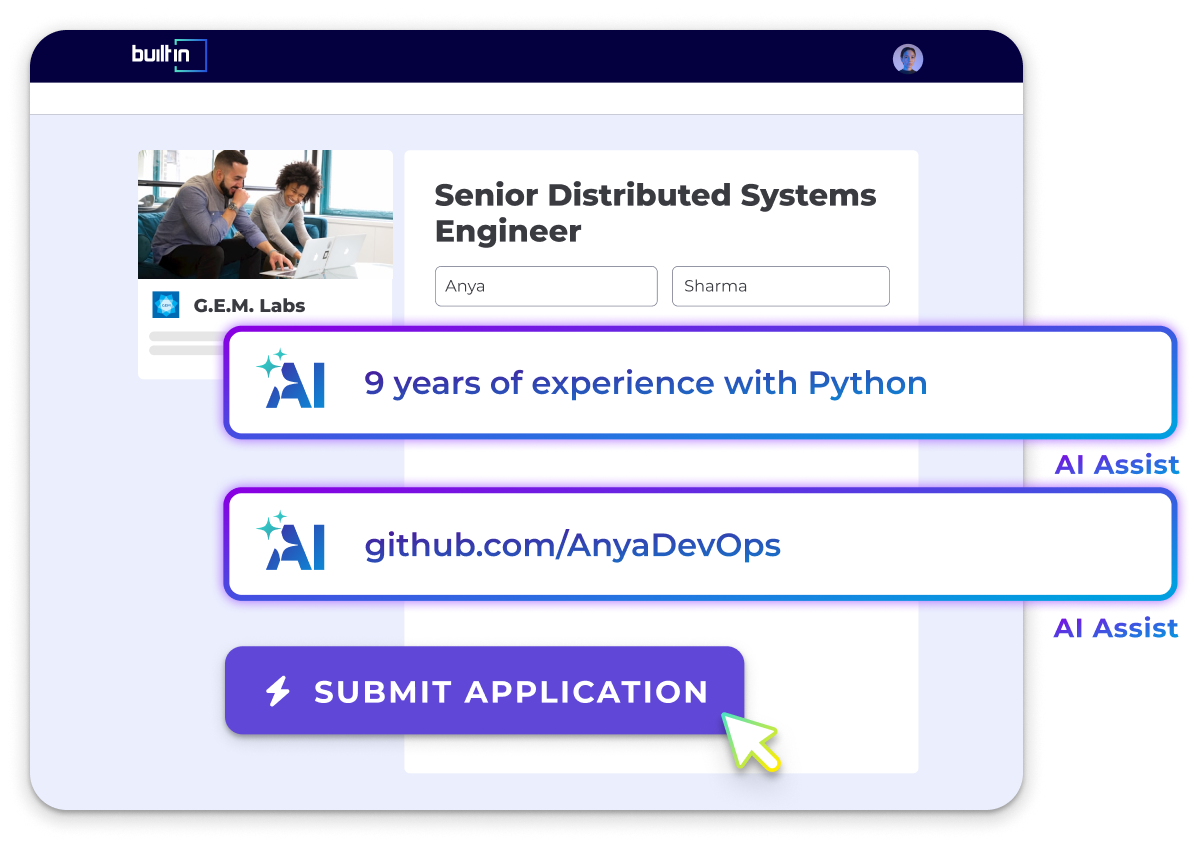
Cloud • Information Technology • Software • Cybersecurity
Supports security operations by onboarding and troubleshooting network monitoring infrastructure, triaging security-device issues, resolving escalated customer problems, coordinating vendor maintenance, and managing hardware sensors. The role collaborates with SOC analysts, assists with testing and quality assurance, provides customer support, and participates in on-call incident response. Requires network and security administration experience, TCP/IP knowledge, command-line expertise, and troubleshooting across Linux, Windows, and macOS.
Top Skills:
AnsibleBashCloud-Based ApplicationsFirewallsIntrusion Detection SystemsLinuxmacOSNetwork AnalysisNetwork Monitoring SystemsPerlPythonSuricataTcp/IpUnixWindows

One Month AgoSaved
Easy Apply
Easy Apply
Artificial Intelligence • Big Data • Cloud • Security • Software • Cybersecurity • Infrastructure as a Service (IaaS)
Own and improve vulnerability management across cloud, on-premises, network, and endpoint environments. Responsibilities include scanning, triage, risk-based prioritization, remediation coordination, SLA tracking, exception management, closure validation, asset reconciliation, reporting, incident support, on-call participation, and audit documentation. The role partners with Engineering, SRE, IT, and Infrastructure teams and uses security tooling and AI-assisted workflows to reduce exposure and recurring vulnerabilities.
Top Skills:
Api AutomationAWSCmdbQualysRapid7 InsightvmTenableWiz

Software • Quantum Computing • Metaverse • Infrastructure as a Service (IaaS)
Develops secure, isolated attack scenarios across cloud, on-premises, and hybrid environments. Reproduces vulnerabilities, builds multi-step attack chains, creates automated graders and reward signals, and validates outcomes using system state and telemetry. The role also develops attack variants and benign comparisons to evaluate AI security agents, partnering with threat researchers, AI engineers, and environment engineers.
Top Skills:
Automated TestingAWSAzureC#C/C++Cloud IamDirectory ServicesGCPGoLinuxPythonTelemetryTypescriptVersion ControlWindows
Reposted 11 Days AgoSaved
Software • Quantum Computing • Metaverse • Infrastructure as a Service (IaaS)
Lead security reviews, code audits, penetration testing, vulnerability research, and mitigation efforts for Microsoft Windows services. Develop reusable security tools and agents, identify attack vectors and architectural risks, demonstrate exploit impact, and collaborate with product engineering teams to design scalable defenses and improve security investments.
Top Skills:
Automated Security ToolsCode ReviewMicrosoft Cloud ServicesWindowsPenetration TestingVulnerability Research

HR Tech • Information Technology • Professional Services • Consulting
Create challenging coding tasks for AI systems, implement deterministic solution verifiers, and contribute backend expertise across feature development, bug fixing, refactoring, performance optimization, testing, and security reviews. The role requires strong programming and software engineering skills, with cybersecurity experience in secure coding, application security, penetration testing, vulnerability assessment, or security-focused code reviews preferred.
Top Skills:
C++CweGoJavaNode.jsOwaspPythonRustTypescript
HR Tech • Information Technology • Professional Services • Consulting
Build and secure scalable backend services and APIs while debugging, optimizing performance, implementing features, refactoring codebases, and conducting security reviews and penetration testing. The role also involves automated testing, code review, vulnerability assessment, and contributing domain expertise to training next-generation AI systems.
Top Skills:
C++CweGoJavaNode.jsOwaspPython 3RustTypescript
Healthtech • Pharmaceutical
Designs, deploys, and manages enterprise cloud security solutions across AWS and Azure. Responsibilities include automating security controls, managing AWS WAF and CDK rules, improving policies, patching vulnerabilities, implementing DevSecOps practices, assessing cloud applications and APIs, monitoring security posture, analyzing logs, triaging issues, and supporting compliance and risk initiatives.
Top Skills:
APIsAWSAws CdkAws WafAzureDevsecops
Logistics • Software
Lead Stord’s enterprise security function and build its long-term strategy, governance, operations, engineering, application and cloud security capabilities. Own NIST, SOC 2 and ISO programs, 24/7 detection and response, incident management, M&A security integration, secure product development, penetration testing, customer trust, business continuity and disaster recovery. Lead the security team, MDR partnership, executive and board communications, AI governance, and security readiness for international growth, acquisitions and potential public-market scrutiny.
Top Skills:
Api SecurityAWSCi/CdCloud Security Posture ManagementDastEdrEu Ai ActEu-U.S. Data Privacy FrameworkGCPGdprIso 27001KubernetesMdrMicroservicesNis2Nist Ai RmfNist Csf 2.0SastSbomSec Cybersecurity DisclosureSecrets ManagementSIEMSoarSoc 2Sox It ControlsVulnerability ManagementXdr
Reposted 11 Days AgoSaved
Other
Architect and engineer multi-tenant SIEM, SOAR, EDR, telemetry, and cloud security platforms for managed security services. Build detection content, automate response workflows, optimize log ingestion, and secure customer connectivity. Lead technical discovery, onboarding, security assessments, remediation planning, escalations, solution design, and customer advisory engagements. Create architectures, runbooks, and documentation while shaping the MSSP technology strategy.
Top Skills:
AWSAzureBindplaneCis BenchmarksCnappCoralogixCrowdstrikeCspmElasticGCPGoogle SecopsInfrastructure-As-CodeMitre Att&CkNist CsfPowershellPythonSentineloneSoarSoc 2TailscaleWiz

Cybersecurity
Supports enterprise application security by operating SAST, DAST, IAST, and IDE security tools; developing pipelines; securing web applications; troubleshooting Linux environments; and implementing enterprise security controls. The role applies OWASP and federal compliance standards, collaborates with clients and application teams, and requires experience with Veracode, Burp Suite, programming languages, and security testing tools.
Top Skills:
.NetBashBurp ProxyBurp SuiteC#CvssCweDastEclipseFedrampFipsHackeroneIastJavaJdeveloperLinuxNist 800-53Owasp Top 10Owasp ZapPythonSans-25SastSeleniumVeracodeVisual StudioWasc
Cloud • Information Technology • Software • Cybersecurity
Engineer and operate SIEM and SOAR platforms supporting SOC and MDR services. Responsibilities include log-source onboarding, parsing, enrichment, detection engineering, playbook automation, alert and dashboard development, end-to-end pipeline troubleshooting, vendor escalations, customer onboarding, ingest-volume management, documentation, and platform incident response. The role serves as the technical escalation point and participates in an after-hours on-call rotation.
Top Skills:
AlbertAmazon Web ServicesCrowdstrikeGCPAzureMitre Att&CkPcapPowershellPythonRegexSIEMSoarSQLSuricataSyslogTcpdumpTlsWireshark
One Month AgoSaved
Easy Apply
Easy Apply
Cloud • Security • Software • Cybersecurity • Automation
Own and evolve GitLab’s authorization systems across its Ruby on Rails monolith and next-generation Rust policy engine. Design fine-grained permissions for users, tokens, roles, and AI agents; secure GraphQL and REST APIs; lead feature-flagged rollouts and migrations; improve performance and reliability; and collaborate across authentication, platform, AI, and modular-service teams in a distributed asynchronous environment.
Top Skills:
CedarGoGraphQLGrpcProtocol BuffersRestRubyRuby On RailsRustYamlZanzibar-Style Authorization
Healthtech
Supports the IT Governance, Risk, and Compliance program through security risk assessments, policy administration, audit readiness, control validation, evidence collection, remediation tracking, regulatory compliance monitoring, and third-party risk reviews. The role maps controls to frameworks including HIPAA, SOC 2, NIST, CIS, CMS, and URAC; maintains risk registers and governance documentation; and partners with technical and business teams to address vulnerabilities, control gaps, and compliance requirements.
Top Skills:
ArcherAuditboardCis ControlsCmsHipaaHitrustIso 27001LogicgateNist Cybersecurity FrameworkOnetrustServicenow GrcSoc 2Urac

Let Your Resume Do The Work
Upload your resume to be matched with jobs you're a great fit for.
Success! We'll use this to further personalize your experience.
Top Companies in Washington, DC Hiring Cyber Security Roles
See All





Popular Washington, DC Job Searches
Tech Jobs & Startup Jobs in Washington, DC
Remote Jobs in Washington, DC
Content Jobs in Washington, DC
Customer Success Jobs in Washington, DC
IT Jobs in Washington, DC
Cyber Security Jobs in Washington, DC
Tech Support Jobs in Washington, DC
Data & Analytics Jobs in Washington, DC
Analysis Reporting Jobs in Washington, DC
Analytics Jobs in Washington, DC
Business Intelligence Jobs in Washington, DC
Data Engineer Jobs in Washington, DC
Data Science Jobs in Washington, DC
Machine Learning Jobs in Washington, DC
Data Management Jobs in Washington, DC
UX Designer Jobs in Washington, DC
Software Engineer Jobs in Washington, DC
Android Developer Jobs in Washington, DC
C# Jobs in Washington, DC
C++ Jobs in Washington, DC
DevOps Jobs in Washington, DC
Front End Developer Jobs in Washington, DC
Golang Jobs in Washington, DC
Hardware Engineer Jobs in Washington, DC
iOS Developer Jobs in Washington, DC
Java Developer Jobs in Washington, DC
Javascript Jobs in Washington, DC
Linux Jobs in Washington, DC
Engineering Manager Jobs in Washington, DC
.NET Developer Jobs in Washington, DC
PHP Developer Jobs in Washington, DC
Python Jobs in Washington, DC
QA Jobs in Washington, DC
Ruby Jobs in Washington, DC
Salesforce Developer Jobs in Washington, DC
Scala Jobs in Washington, DC
Finance Jobs in Washington, DC
HR Jobs in Washington, DC
Internships in Washington, DC
Legal Jobs in Washington, DC
Marketing Jobs in Washington, DC
Operations Jobs in Washington, DC
Office Manager Jobs in Washington, DC
Operations Manager Jobs in Washington, DC
Product Manager Jobs in Washington, DC
Project Manager Jobs in Washington, DC
Sales Jobs in Washington, DC
Account Executive (AE) Jobs in Washington, DC
Account Manager (AM) Jobs in Washington, DC
Sales Leadership Jobs in Washington, DC
Sales Development Representative Jobs in Washington, DC
Sales Engineer Jobs in Washington, DC
Sales Operations Jobs in Washington, DC
All Filters
Total selected ()
No Results
No Results
