

Maximum of 25 job preferences reached.
Top Senior Cyber Security Jobs in Washington, DC
Aerospace • Defense
Lead enterprise security risk assessments, maintain the risk register, prioritize and track remediation, evaluate vendor and architectural risks, define risk methodologies, map controls to NIST and CMMC requirements, support audits, report risk metrics to leadership, and promote risk ownership across the organization.
Top Skills:
CmmcEarFairIso 27001ItarNist 800-171Nist 800-30Nist RmfSoc 2
Cloud • Security • Cybersecurity
Secure Wiz’s products, CI/CD systems, and production cloud infrastructure through threat modeling, security reviews, vulnerability management, detection and response, cloud and Kubernetes security baselines, policy-as-code, and automation. Partner with engineering, DevOps, operations, and Federal teams to implement scalable security controls, remediate risks, support FedRAMP requirements, and promote secure-by-design development practices.
Top Skills:
AksAWSAzureCiemCloudFormationCnappCspmEksFedrampGCPGkeGoHclHelmIamKubernetesOwasp Top 10PulumiPythonRegoShellTerraform
Healthtech
Designs, implements, and manages AWS cloud security policies, architecture, and technologies. The role oversees firewalls, DLP, vulnerability scanning, monitoring, logging, IAM, incident response, compliance, and remediation. It provides security guidance for AWS solutions, supports migrations of mission-critical applications, researches new technologies, documents standards, presents to varied audiences, and mentors less experienced engineers. The position requires strong AWS expertise, infrastructure-as-code proficiency, knowledge of regulated healthcare environments, and experience securing highly available cloud and serverless architectures.
Top Skills:
Active DirectoryAdfsAmazon CloudfrontAmazon CloudwatchAmazon InspectorAmazon MacieAmazon VpcApplication Load BalancerAWSAws CloudformationAws CloudtrailAws ConfigAws Control TowerAws GuarddutyAws LambdaAws Security HubAws ShieldAws Transit GatewayAws Trusted AdvisorAws WafAzureAzure AdBashCi/CdCisDatadogDynatraceGCPHipaaHitrustIamInfrastructure As CodeJSONLanding Zone AcceleratorNetwork AclsNetwork Load BalancerNew RelicNistPci DssPythonSecurity GroupsSoc 2SplunkTerraformVpc Flow LogsYaml
News + Entertainment
Own security partnerships for Netflix Marketing and Animation, advising leaders on risk, GenAI adoption, access controls, content protection, architecture, and remediation. Lead risk assessments, business risk profiles, metrics, and pre-release content security initiatives. Support technical security due diligence for acquisitions and subsidiaries while translating complex security concerns into actionable business guidance across application, cloud, identity, and data domains.
Top Skills:
Application SecurityCloud SecurityData GovernanceGenaiIdentity And Access Management

Information Technology • Consulting
Supports cybersecurity risk management and authorization for the VA.gov Platform. Assesses NIST security controls, performs gap and risk analyses, maintains SSPs, POA&Ms, and authorization evidence, and translates deficiencies into engineering remediation. The role supports ATO/cATO readiness, OSCAL automation, threat modeling, secure design reviews, stakeholder coordination, incident response, and continuous synchronization between technical changes and security documentation.
Top Skills:
Amazon EksAtoAWSCatoCi/CdFisma HighGithub ActionsInfrastructure As CodeKubernetesNist 800-53Nist Risk Management Framework (Rmf)OscalWasa/Dast

Software
Build and operate infrastructure security platforms centered on workload identity, service-to-service authentication, authorization, and short-lived credentials. Replace static secrets with identity-based systems, develop identity-authenticated proxies and APIs, and unify authorization policy management. Partner with platform and application teams to drive adoption, migrate legacy systems, and ensure reliable production infrastructure with strong developer experience.
Top Skills:
Authorization SystemsCert-ManagerDistributed SystemsEgress ProxiesIdentity CertificatesJwtKubernetesOpaPkiSecrets ManagementSpiffeSpireWorkload IdentityX.509 Certificates
Software
Lead secure design and code reviews, conduct penetration testing and code audits, build secure-by-default systems, improve security tooling and vulnerability management, operate responsible disclosure programs, remediate production vulnerabilities, and address customer security concerns. The role partners closely with engineering teams and requires strong coding, risk assessment, offensive security, and security communication skills.
Top Skills:
Ai AutomationAuthenticationCode AuditingIdentity And Access ControlPenetration TestingStatic AnalysisSupply Chain SecurityVulnerability Management
Cloud • Information Technology • Cybersecurity
Provides security engineering and architecture expertise for FedRAMP authorization and continuous monitoring. Reviews cloud service provider architectures, security controls, authorization packages, assessment reports, vulnerabilities, and compliance documentation against NIST, FedRAMP, FISMA, RMF, and agency requirements. Leads vendor interviews, identifies technical and documentation gaps, advises government program leads and CISOs on risk posture, and supports secure, compliant, resilient system design.
Top Skills:
Cloud ArchitecturesFedrampFismaNistPenetration TestingRmfSecurity Control ImplementationsVulnerability Scanning
Blockchain • Financial Services • Cryptocurrency • Web3
Owns broad product and operational security responsibilities, including identity and access management, threat modeling, code review, fuzzing, bug bounty operations, AI security research, software supply chain monitoring, penetration test coordination, and compliance evidence. The role requires a strong software engineering background, product security expertise, security tooling development, systems programming experience, and familiarity with web3 or DeFi. It is remote-first and emphasizes autonomy, documentation, and high ownership.
Top Skills:
Artificial Intelligence SecurityBug Bounty PlatformsC++DefiFuzzingGoHardware Security Modules (Hsms)Identity And Access ManagementLinuxMobile Device Management (Mdm)Multisignature SchemesPenetration TestingPrivileged Access Management (Pam)PythonRustSingle Sign-On (Sso)Software Supply Chain SecuritySolanaThreat ModelingTrusted Execution Environments (Tees)Web3
Cloud • Security • Software • Cybersecurity • Automation
Lead corporate endpoint security architecture with a focus on macOS, designing secure-by-default controls, automation, patching, software distribution, and security baselines across macOS, iOS, Windows, and Linux. Manage configurations through Terraform, GitOps, version control, CI pipelines, and automated rollouts. Partner with IT and security teams to improve telemetry, detection, response, auditability, and operational efficiency. Mentor engineers and serve as a senior escalation point for complex endpoint security issues in a fully remote environment.
Top Skills:
BashFleetdmGitGitopsGoGoogle WorkspaceInfrastructure As CodeiOSJamf ProLdapLinuxmacOSOktaPowershellPythonTerraformWindows

Other
Lead independent security assessments and authorization activities for federal cloud, hybrid, and enterprise systems. Evaluate Azure and AWS security controls, FedRAMP packages, inherited controls, vulnerabilities, architectures, and technical evidence. Produce assessment plans, reports, risk assessments, evidence requests, and POA&Ms. Communicate findings and mitigation recommendations to technical teams, system owners, executives, and stakeholders while supporting consistent, defensible cybersecurity assessment practices.
Top Skills:
Amazon Web Services (Aws)CsamFedrampAzureNist Risk Management Framework (Rmf)
Cloud • Software • Cybersecurity
Build backend services and distributed systems for a cybersecurity and software supply chain security platform. Develop scalable APIs, data pipelines, and platform components handling vulnerability, container, package, runtime, and SBOM data. Work across Linux, Kubernetes, containers, and cloud environments while solving concurrency, performance, reliability, and distributed processing challenges. Own projects from design through deployment, participate in architecture discussions, review code, and collaborate with security researchers and product teams.
Top Skills:
APIsApkAWSAzureC++Ci/CdContainer RuntimesData PipelinesDebDockerGCPGoJavaKubernetesLinuxMicroservicesNosql DatabasesPythonRelational DatabasesRpmSbomsSoftware Composition Analysis
New
Cut your apply time in half.
Use ourAI Assistantto automatically fill your job applications.
Use For Free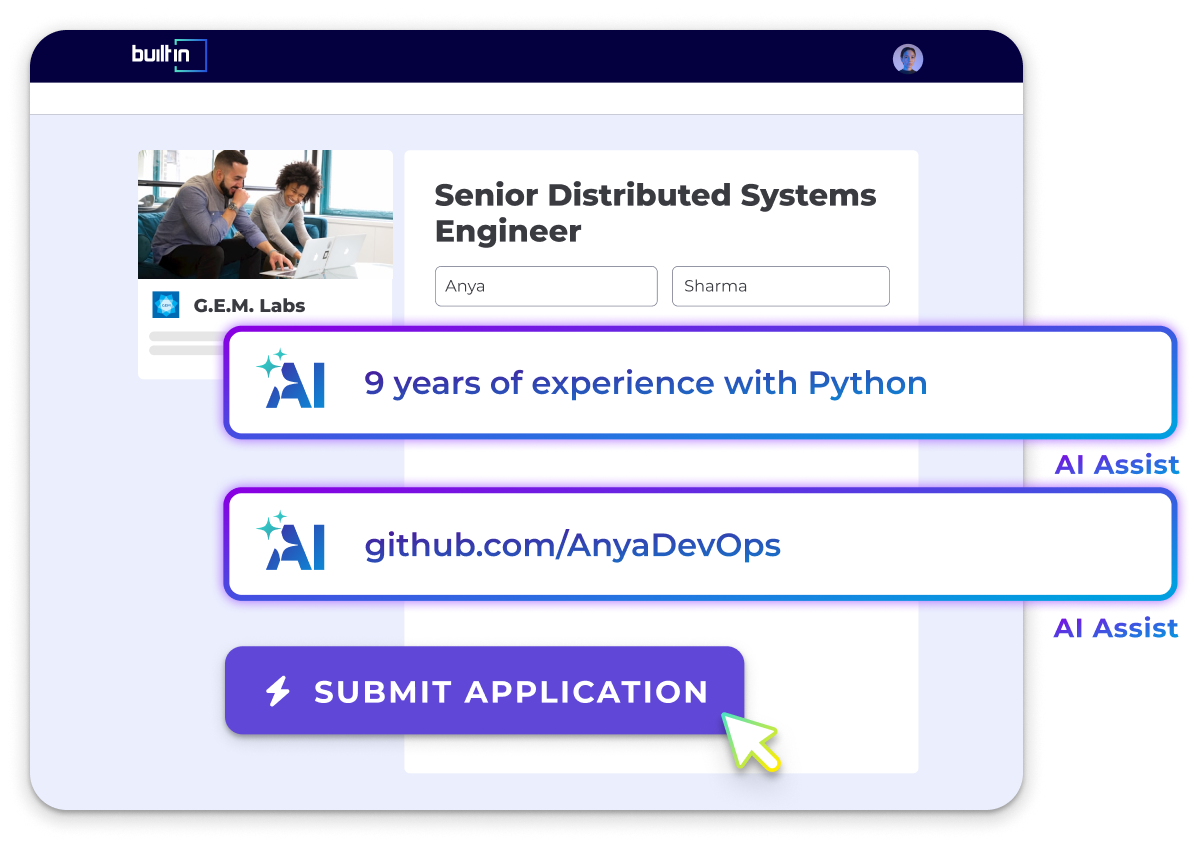

Aerospace • Information Technology • Security • Cybersecurity • Defense
Leads cybersecurity professionals implementing the Risk Management Framework for federal IT systems. Oversees system categorization, security control selection and assessment, authorization documentation, continuous monitoring, risk analysis, remediation, incident response, audit support, and stakeholder training. Advises leadership on cybersecurity risks and compliance while maintaining alignment with NIST guidance and DoD requirements.
Top Skills:
NistRmf
One Month AgoSaved
Aerospace • Information Technology • Security • Cybersecurity • Defense
Advise and lead cybersecurity risk management activities for cloud and federal systems, including system categorization, security control selection, implementation oversight, assessments, authorization documentation, continuous monitoring, incident response, remediation, audits, and stakeholder training. Maintain compliance with RMF, NIST guidance, and DoD requirements while reporting security risks and improvement opportunities to leadership.
Top Skills:
AWSAzureCloud ComputingGCPHp WebinspectIbm GuardiumNistNmapRmfSplunkTenable NessusTenable Securitycenter

Information Technology • Security • Cybersecurity
Designs and presents Qualys security solutions for federal enterprise customers, supporting technical sales engagements, proofs of concept, architecture workshops, compliance programs, and post-sale deployment health checks. Advises customers on vulnerability, asset, patch, cloud, application, and threat security while partnering with sales, product, marketing, and strategic partners. Authors technical content, enables field teams, and travels to customer locations at least 30% of the time.
Top Skills:
AWSGoogle Cloud PlatformAzureQualys Platform
Aerospace • Information Technology • Security • Cybersecurity • Defense
Supports federal cybersecurity programs by implementing and assessing NIST security controls, managing RMF authorization activities in eMASS, developing security documentation, and maintaining POA&Ms. The role coordinates STIG remediation, conducts risk assessments, monitors incidents, and communicates security requirements to technical and nontechnical stakeholders. Requires extensive ISSO or security engineering experience, advanced cybersecurity certification, familiarity with security tools, and an active TS/SCI clearance with the ability to obtain a polygraph.
Top Skills:
DatabasesEmassEncryptionFirewallsHp WebinspectIbm GuardiumIntrusion Detection SystemsIntrusion Prevention SystemsLinuxNist Sp 800-53Nist Sp 800-53ANmapRisk Management Framework (Rmf) V5Security CenterSecurity Technical Implementation Guides (Stigs)SplunkTcp/IpTenable NessusUnixWeb ServersWindows
Artificial Intelligence • Information Technology • Software • Defense
Supports security operations and SIEM administration for Department of State IT environments. Develops secure installation guides aligned with federal standards and DISA STIGs, configures and manages SIEM processes and tools, implements security solutions for threats and vulnerabilities, and performs patch management and security update operations to maintain compliance.
Top Skills:
DatabasesDisa StigsOperating SystemsPatch ManagementSIEMSplunkVirtual Machines
Artificial Intelligence • Information Technology • Software • Defense
Leads a 10-person security operations team supporting Department of State IT systems. Responsibilities include security monitoring, incident response, vulnerability and cyber hygiene assessments, POA&M remediation, patching, centralized logging, A&A and ATO support, security architecture, risk mitigation, asset management, and compliance with government security standards. The role also coordinates engineers, project managers, stakeholders, and personnel training while supporting secure government environments.
Top Skills:
Authority To Operate (Ato)Centralized LoggingCloud ComputingEncryption DevicesIncident ResponseInformation Assurance StandardsNetwork SecurityPatch ManagementSecurity ArchitectureSecurity MonitoringThreat AnalysisVulnerability Assessment
Artificial Intelligence • Information Technology • Software • Defense
Designs, implements, maintains, and evolves firewall and network security systems supporting a global Department of State network. Troubleshoots complex firewall-related incidents, evaluates security products and configurations, develops upgrade plans, coordinates with vendors and the CISO, and serves as a senior escalation point for administrators and technicians. The role also documents security elements, researches emerging threats, approves technical solutions, and provides guidance to junior staff.
Top Skills:
F5FirewallsNetwork SecurityPalo AltoUnified Communications Systems

Information Technology • Other
Provides multidisciplinary information assurance and cybersecurity leadership for a Department of Defense client. Responsibilities include supporting vulnerability management, penetration testing, corrective actions, NIST RMF and security control implementation, STIGs, SCAP, IAVAs, FISMA, defensive cyber operations, incident response, reporting, recovery, and complex DoD project management. Requires extensive DoD IA experience, an approved Level 3 cybersecurity certification, and a favorably adjudicated NACI investigation.
Top Skills:
CisaCismCisspDod 8570.01-MFismaGslcIavasNist RmfNist Sp 800-53Penetration TestingScapStigsVulnerability Management
Big Data • Fintech • Mobile • Payments • Financial Services
Lead and mature Affirm's third-party security risk program by designing controls, automating GRC workflows, evaluating third-party/cloud security, building integrations and dashboards, and advising stakeholders. Drive automation using Python and agentic coding tools, operate orchestration across systems, manage a portfolio of risk reviews, and establish metrics, processes, and reporting to scale security risk management.
Top Skills:
AWSAzureBi ToolsClaudeCopilotCursorGCPGrc PlatformsIamIdentity ProvidersLoggingPythonSQLTicketing SystemsVendor Management Tools

Artificial Intelligence • Machine Learning • Software • Defense
Owner of Vannevar's authentication and authorization platform: build tenant-isolated auth systems, self-service user/group/permission admin UI, tooling to visualize and validate access, feature-flag and platform management interfaces, and shared authorization capabilities across products.
Top Skills:
Api DesignDistributed SystemsJavaJwtsKeycloakNode.jsOauth 2.0OpenfgaOpenid Connect (Oidc)PostgresPythonRbac/AbacReactSAMLSession ManagementSsoTypescript
AdTech • Artificial Intelligence • Big Data • Machine Learning • Marketing Tech • Mobile • Software
The Security Engineer will manage Liftoff's SIEM, lead the adoption of AI-augmented SOC tools, triage alerts, and improve incident response processes while collaborating on various security functions.
Top Skills:
AIAWSDetection-As-CodePantherSecurity AutomationSIEM
Artificial Intelligence • Machine Learning • Software • Defense
Lead and grow a Security Platform engineering team to design and operate centralized identity and access services (IdP integrations, SSO, authorization frameworks). Define roadmap, partner cross-functionally, and drive adoption of secure-by-default access controls across products.
Top Skills:
Access ManagementAuthenticationAuthorizationAuthorization Policy FrameworksDistributed SystemsIdentity PlatformIdpSso

Agency • Information Technology
Manages enterprise information security governance, risk, and compliance initiatives. Develops security policies and frameworks, leads data classification and threat modeling, conducts risk assessments, oversees vulnerability remediation, evaluates security controls, supports audits, and prepares risk metrics and executive reports. Partners with technical teams to embed security requirements and promotes governance best practices across the organization.
Top Skills:
Audit ReadinessCompliance ManagementCybersecurityData ClassificationInformation Security GovernanceRisk AssessmentSecurity ControlsSecurity DashboardsSecurity FrameworksThreat ModelingVulnerability Management

Let Your Resume Do The Work
Upload your resume to be matched with jobs you're a great fit for.
Success! We'll use this to further personalize your experience.
Top Companies in Washington, DC Hiring Senior Cyber Security Roles
See All






Popular Washington, DC Senior Level Job Searches
Senior Level Jobs in Washington, DC
Senior Remote Jobs in Washington, DC
Senior Content Jobs in Washington, DC
Senior Customer Success Jobs in Washington, DC
Senior IT Jobs in Washington, DC
Senior Cyber Security Jobs in Washington, DC
Senior Tech Support Jobs in Washington, DC
Senior Data & Analytics Jobs in Washington, DC
Senior Analysis Reporting Jobs in Washington, DC
Senior Analytics Jobs in Washington, DC
Senior Business Intelligence Jobs in Washington, DC
Senior Data Engineer Jobs in Washington, DC
Senior Data Science Jobs in Washington, DC
Senior Machine Learning Jobs in Washington, DC
Senior Data Management Jobs in Washington, DC
Senior UX Designer Jobs in Washington, DC
Senior Software Engineer Jobs in Washington, DC
Senior Android Developer Jobs in Washington, DC
Senior C# Jobs in Washington, DC
Senior C++ Jobs in Washington, DC
Senior DevOps Jobs in Washington, DC
Senior Front End Developer Jobs in Washington, DC
Senior Golang Jobs in Washington, DC
Senior Hardware Engineer Jobs in Washington, DC
Senior iOS Developer Jobs in Washington, DC
Senior Java Developer Jobs in Washington, DC
Senior Javascript Jobs in Washington, DC
Senior Linux Jobs in Washington, DC
Senior Engineering Manager Jobs in Washington, DC
Senior .NET Developer Jobs in Washington, DC
Senior PHP Developer Jobs in Washington, DC
Senior Python Jobs in Washington, DC
Senior QA Jobs in Washington, DC
Senior Ruby Jobs in Washington, DC
Senior Salesforce Developer Jobs in Washington, DC
Senior Scala Jobs in Washington, DC
Senior Finance Jobs in Washington, DC
Senior HR Jobs in Washington, DC
Senior Legal Jobs in Washington, DC
Senior Marketing Jobs in Washington, DC
Senior Operations Jobs in Washington, DC
Senior Office Manager Jobs in Washington, DC
Senior Operations Manager Jobs in Washington, DC
Senior Product Manager Jobs in Washington, DC
Senior Project Manager Jobs in Washington, DC
Senior Sales Jobs in Washington, DC
Senior Account Executive (AE) Jobs in Washington, DC
Senior Account Manager (AM) Jobs in Washington, DC
Senior Sales Leadership Jobs in Washington, DC
Senior Sales Development Representative Jobs in Washington, DC
Senior Sales Engineer Jobs in Washington, DC
Senior Sales Operations Jobs in Washington, DC
All Filters
Total selected ()
No Results
No Results
