

Ready to join a team that’s all in? At Imprivata, we deliver unified access and security management programs that eliminate friction, empowering healthcare and mission-critical organizations to work smarter, faster, and more securely.
We believe work can be more than a job or task—it’s a collective spirit; the type that emboldens creativity, embraces challenge, and fosters excitement. We are constantly raising the bar on what’s possible, owning the outcome of our triumphs and trials, staying nimble amidst change, and cultivating an environment where we win together. Here, your ideas matter, your differences are celebrated, and your work drives real results—for your career, your teammates, and our customers.
When you join Imprivata, you embark on a shared journey of ambition and growth. We’re committed to building an inclusive workplace where everyone feels valued and supported. If you’re looking for a place to match your passion with purpose—and where every day you can make an impact—you’ll find it here.
We are seeking an IT Support and Access Governance Manager to join our team. This is a hybrid opportunity based in our Waltham, MA office.
Job Summary
The IT Controls and Access Governance Manager is responsible for building and operating Imprivata’s IT-owned access governance and controls program across systems, services and sensitive data. The role partners closely with the CISO and Security organization, system administrators, application owners, Finance, Legal, Internal Audit and external auditors to translate security and compliance requirements into executable IT processes, reliable evidence and measurable remediation.
The manager establishes a repeatable, risk-based control framework across the application portfolio, beginning with higher-risk systems. The role operates the governance process across Security, IT, and the business by maintaining the control system of record, coordinating access reviews and certifications, measuring control performance, tracking exceptions and remediation, escalating deficiencies, and helping ensure approved access is implemented and auditable. The manager partners closely with Security, which owns security policy, risk appetite, and control objectives; IT, which owns technical implementation, administration, service operations, and remediation; and business stakeholders, who define the operational needs that access and controls must support.
Duties and Responsibilities
- Build and continuously improve an enterprise access governance and IT controls program spanning SaaS applications, infrastructure, developer platforms, data services and other technology-enabled business processes.
- Create and maintain a risk-based inventory of in-scope systems, data types, privileged roles, access paths, control owners, review frequencies, evidence requirements and remediation expectations.
- Assess each system’s data risk, access model and control maturity; document gaps; prioritize remediation; and develop practical roadmaps with system administrators and business owners.
- Design and operate recurring access review and certification processes, including executive and application-owner summaries that require validation of user access, privileged access, service accounts, roles, entitlements and exceptions.
- Support the CISO in translating security requirements into access standards for sensitive and regulated data, including alignment with Data Security Posture Management (DSPM) findings; maintain standards and facilitate review and approval while Security retains policy and control-objective ownership and IT retains implementation ownership.
- Lead the initial governance rollout using risk-based prioritization that considers systems supporting financial reporting, segregation-of-duties conflicts, source-code protection, security risks and the sensitivity of the data involved.
- Establish control metrics, dashboards and executive reporting that communicate review completion, exceptions, inappropriate access, overdue remediation, privileged access, joiner-mover-leaver performance and control health over time.
- Own the operating cadence and governance workflow for the access governance lifecycle; identify manual failure points; and coordinate the build-out of a program that improves timeliness, accuracy and auditability
- Run governance workflows, confirm required approvals are present, track exceptions and escalate overdue or material items. The role does not independently approve access or accept security risk.
- Partner with system administrators to implement and improve integrations, connectors, workflows, role models, approval paths, reconciliation routines and reporting within IGA, IAM, ITSM and application platforms, while technical administration remains with IT.
- Use scripting, APIs, data analysis, workflow automation and AI agents to reduce manual evidence collection, identify anomalous or excessive access, draft review packages, route approvals and monitor control exceptions—while preserving human accountability for approvals and decisions.
- Maintain control documentation, operating standards, procedures, control narratives, process maps, runbooks and other governance documentation; facilitate training and adoption for administrators, managers and executives.
- Serve as a senior contributor to IT Services leadership by identifying systemic process improvements, clarifying ownership, supporting operational planning and helping the team mature its ITIL-based practices.
- Track findings and remediation commitments through closure, perform root-cause analysis, and escalate material or persistent control deficiencies to the appropriate leaders.
- Other duties as assigned and required
Required Qualifications
- Bachelor’s degree in Information Technology, Computer Science, Cybersecurity, Business Information Systems or a related field, or equivalent combination of education and relevant experience.
- 5 to 7 years of progressive experience in identity and access management, IT controls, IT audit, security operations, systems administration, compliance or a related technical discipline.
- Hands-on experience administering, configuring, integrating or governing enterprise applications and identity platforms; experience with Salesforce, NetSuite, GitHub, Microsoft Entra ID, Okta, SailPoint, Saviynt, ServiceNow or comparable technologies is strongly preferred.
- Demonstrated experience with access reviews, access certification, role-based access control, privileged access, entitlement management, segregation of duties, user lifecycle management, provisioning, deprovisioning and reconciliation.
- Working knowledge of IT general controls and audit concepts, including access management, change management, system operations, evidence quality, completeness and accuracy, control design and operating effectiveness.
- Ability to understand application authorization models, directories, APIs, data flows and system integrations well enough to partner credibly with technical administrators and identify the art of the possible.
- Experience building repeatable processes, control documentation, metrics, dashboards, audit workpapers or management reporting that can withstand internal and external audit scrutiny.
- Strong analytical and problem-solving skills, sound judgment and process discipline, with the ability to connect technical access issues to business, financial reporting, privacy, security and compliance risk.
- Demonstrated ability to influence without authority, facilitate decisions, manage cross-functional dependencies and communicate clearly with technical teams, business owners, executives and auditors.
- Passion for automation and practical application of AI agents, data analytics and workflow technologies to improve control coverage, reduce manual effort and increase the frequency and quality of governance activities.
- Experience with ITIL practices, Lean Six Sigma, continuous improvement, process mapping or structured change management is a plus.
- Relevant certifications such as CISA, CISM, CISSP, CRISC, ITIL Foundation, Lean Six Sigma or an identity-platform certification are a plus.
This position offers a total compensation range of $133,000.00 to $143,000.00 (inclusive of base salary and variable compensation, such as bonuses and incentives). In addition, more information about Imprivata’s benefit offerings can be found here. This range represents the high and low end of Imprivata’s compensation range for this position. Actual compensation will vary and may be above or below the range based on various factors, such as a candidate’s location, skills, experience, and qualifications.
At Imprivata, we have a top-notch work environment, developmental opportunities, a competitive total rewards package, and the desire to have fun. If you have the skills and qualifications as we have described above, we want to hear from you!
Imprivata provides equal employment opportunities, regardless of race, religion, age, sex, national origin, disability status, protected veteran status, sexual orientation, gender identity or expression, or any other characteristic protected by federal, state or local laws.
#LI-Hybrid #LI-SF1
Skills Required
- Bachelor's degree in Information Technology, Computer Science, Cybersecurity, Business Information Systems, or a related field, or equivalent education and relevant experience.
- 5 to 7 years of progressive experience in identity and access management, IT controls, IT audit, security operations, systems administration, compliance, or a related technical discipline.
- Hands-on experience administering, configuring, integrating, or governing enterprise applications and identity platforms.
- Experience with Salesforce, NetSuite, GitHub, Microsoft Entra ID, Okta, SailPoint, Saviynt, ServiceNow, or comparable technologies.
- Experience with access reviews, access certification, role-based access control, privileged access, entitlement management, segregation of duties, user lifecycle management, provisioning, deprovisioning, and reconciliation.
- Working knowledge of IT general controls and audit concepts, including access management, change management, system operations, evidence quality, completeness and accuracy, control design, and operating effectiveness.
- Ability to understand application authorization models, directories, APIs, data flows, and system integrations.
- Experience building repeatable processes, control documentation, metrics, dashboards, audit workpapers, or management reporting suitable for internal and external audit scrutiny.
- Strong analytical and problem-solving skills, sound judgment, process discipline, and ability to connect technical access issues to business, financial reporting, privacy, security, and compliance risk.
- Ability to influence without authority, facilitate decisions, manage cross-functional dependencies, and communicate with technical teams, business owners, executives, and auditors.
- Experience applying automation, AI agents, data analytics, and workflow technologies to improve control coverage and governance activities.
- Experience with ITIL practices, Lean Six Sigma, continuous improvement, process mapping, or structured change management.
- Relevant certifications such as CISA, CISM, CISSP, CRISC, ITIL Foundation, Lean Six Sigma, or an identity-platform certification.
What the Team is Saying




Imprivata Compensation & Benefits Highlights
-
Healthcare Strength — Medical coverage includes company funding of half the deductible via HSA/HRA alongside medical, dental, and vision options; feedback suggests healthcare is one of the stronger aspects of the package.
-
Leave & Time Off Breadth — A flexible time-off policy is promoted rather than a fixed vacation bank, and feedback suggests this flexibility supports work-life balance in many teams.
-
Parental & Family Support — Paid parental leave and caregiver resources via Care.com, plus dependent and domestic-partner coverage, indicate a family-oriented set of benefits that goes beyond basic insurance.
Imprivata Insights

What We Do
For more than two decades, Imprivata has been redefining how life- and mission-critical industries secure and manage digital identities. We empower healthcare and enterprise organizations to enable fast, compliant, and secure access to technology—allowing clinicians and staff to stay focused on what matters most: patient care and operational excellence. Our digital identity platform is purpose-built for complex environments where every second counts and security can never take a back seat. From authentication and access management to device, application, and identity governance, Imprivata provides a unified approach that balances usability with protection. Trusted by the world’s leading healthcare systems and enterprises in over 45 countries, we deliver solutions that improve efficiency, safeguard data, and drive digital transformation. At Imprivata, our commitment goes beyond technology—we partner closely with our customers to ensure their success, every step of the way.
Why Work With Us
At Imprivata, every voice matters. We’re a global team driven by innovation, compassion, and collaboration. Together, we live our values—Raise the Bar, Own the Outcome, Stay Nimble, and Win Together—while making a real impact on healthcare, technology, and the communities we serve.
Gallery


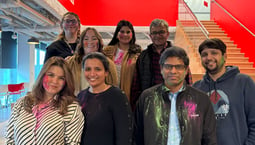
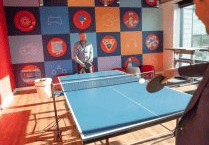
Imprivata Offices
Hybrid Workspace
Employees engage in a combination of remote and on-site work.
Imprivata offers a flexible hybrid work model with three in-office days and two remote. Collaboration is key, and schedules are coordinated with managers to balance flexibility and connection.
