Based in our Belfast office, you will be a key player in our Governance, Risk & Compliance (GRC) team, helping Rapid7 maintain its reputation for transparency and security across the EMEA and APAC regions.
About the Team
Rapid7's GRC team operates at the intersection of technical excellence and business enablement, partnering deeply with InfoSec, Legal, and Engineering to build resilient, compliant, and transparent security posture for our customers.
About the Role
As a Security Governance Analyst, your primary responsibility will be to serve as a key practitioner executing compliance initiatives and bridging the gap between technical teams and regulatory frameworks. Specifically, your focus will be to:
- Execute GRC deliverables within SLAs, ensuring compliance programs run predictably and with high quality.
- Translate complex auditor requirements into actionable, practical steps for internal technical and engineering teams.
- Identify gaps, spot project delays, and flag risks early to pivot proactively toward effective solutions.
- Assist in evaluating the design and effectiveness of security controls to support the overall audit lifecycle.
- Advocate for security controls across the business to foster an organizational culture where security is a shared responsibility.
The skills and qualities you'll bring include:
- Bring 2+ years of experience in information security, IT audit, or a related compliance domain within cloud-first environments.
- Demonstrate foundational knowledge of security frameworks such as ISO 27001, SOC2, or NIST CSF.
- Break down complex compliance objectives into clear, time-bound milestones while executing quickly and assessing progress.
- Hold self and others responsible for driving outcomes, delivering commitments, and establishing clear project ownership.
- Communicate complex technical risks and rationale clearly to non-technical stakeholders to build alignment.
- Build global cross-functional partnerships across legal, engineering, and security teams to deliver sustainable business value.
- Apply strong self-awareness to adapt to group dynamics, seek feedback, and learn continuously from challenges.
- Embody our core values to foster a culture of excellence that drives meaningful impact and collective success.
We know that the best ideas and solutions come from multi-dimensional teams. That's because these teams reflect a variety of backgrounds and professional experiences. If you are excited about this role and feel your experience can make an impact, please don't be shy - apply today.
#LI-PB1
About Rapid7
At Rapid7, our vision is to create a secure digital world for our customers, our industry, and our communities. We do this by harnessing our collective expertise and passion to challenge what's possible and drive extraordinary impact. We're building a dynamic and collaborative workplace where new ideas are welcome.
Protecting 11,500+ customers against bad actors and threats means we're continuing to push the envelope just like we' ve been doing for the past 20 years. If you 're ready to solve some of the toughest challenges in cybersecurity, we're ready to help you take command of your career. Join us.
Skills Required
- 2+ years of experience in information security, IT audit, or a related compliance domain within cloud-first environments
- Foundational knowledge of ISO 27001, SOC 2, or NIST CSF security frameworks
- Ability to translate complex compliance objectives into clear, time-bound milestones and execute quickly
- Ability to drive outcomes, deliver commitments, and establish clear project ownership
- Ability to communicate complex technical risks and rationale clearly to non-technical stakeholders
- Ability to build cross-functional partnerships across Legal, Engineering, and Security teams
- Self-awareness, adaptability, receptiveness to feedback, and continuous learning
- Commitment to the company's core values and culture of excellence
What the Team is Saying



Rapid7 Compensation & Benefits Highlights
-
Leave & Time Off Breadth — Time off is described as robust, with unlimited PTO for U.S. employees alongside company-wide disconnect days and standard holidays. Feedback suggests this breadth provides meaningful flexibility and recharge time.
-
Healthcare Strength — Healthcare is characterized as comprehensive, including medical, dental, vision, and mental-health resources, often available from the start date. Feedback suggests these offerings stand out as a core strength of the package.
-
Equity Value & Accessibility — Equity participation is available through an ESPP and, for many roles, RSUs or stock options. Feedback suggests these programs add meaningful value to total compensation.
Rapid7 Insights

What We Do
At Rapid7, our vision is to create a secure digital world for our customers, our industry, and our communities. We do this by harnessing our collective expertise and passion to challenge what’s possible and drive extraordinary impact. We’re building a dynamic and collaborative workplace where new ideas are welcome. Protecting 11,000+ customers against bad actors and threats means we’re continuing to push the envelope - just like we’ve been doing for the past 20 years. If you’re ready to solve some of the toughest challenges in cybersecurity, we’re ready to help you take command of your career. Join us.
Why Work With Us
With our products, research, and open source communities, we’re building a secure digital future for everyone. This means constantly learning and evolving in an industry that’s anything but stagnant. You’ll be faced with tough challenges, and given the support to find creative solutions that drive our business, and your career forward.
Gallery
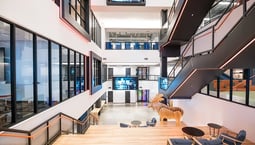
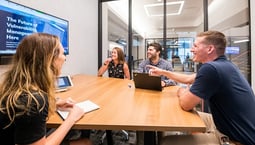
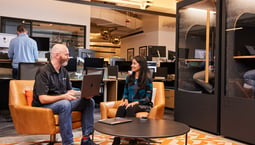
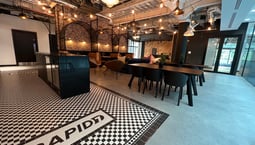
Rapid7 Offices
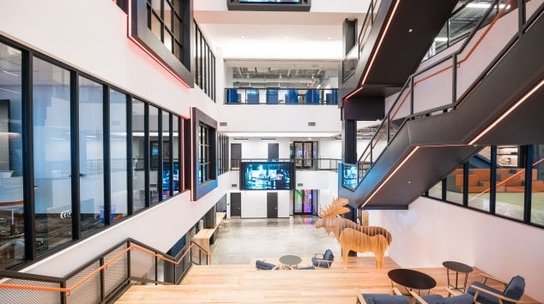
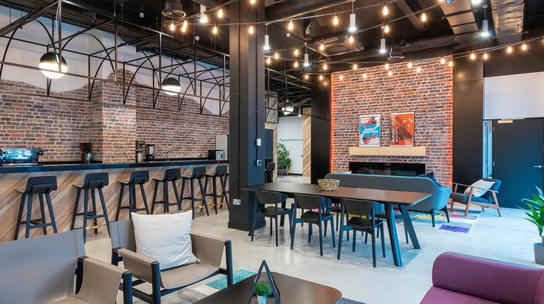
Hybrid Workspace
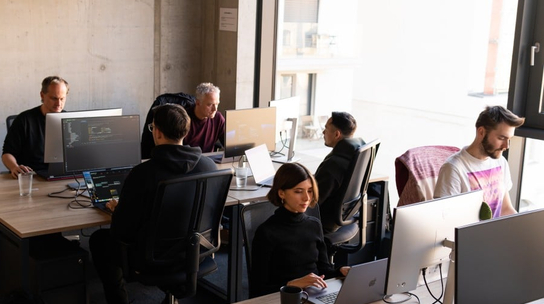
Employees engage in a combination of remote and on-site work.
Our default working model is hybrid, with employees working three days per week in the office. This approach underpins our commitment to flexibility and adaptability while supporting our dedication to development, teamwork and customer purpose.