

Maximum of 25 job preferences reached.
Top Cybersecurity Jobs

Software
Own identity, endpoint, network, and security engineering for a distributed robotics company operating in a CMMC 2.0 Level 2 environment. Responsibilities include securing Microsoft and Google environments, managing devices and networks, implementing zero-trust access, maintaining DNS and email authentication, conducting audits, developing NIST 800-171-aligned standards and incident response runbooks, establishing AI tooling guardrails, managing vendors, and handling hardware logistics.
Top Skills:
AndroidAWSClaude CodeCloudflare DnsCloudflare TunnelCloudflare Zero TrustCmmc 2.0DkimDmarcDnsEntra IdFirewallsGcc HighGoogle WorkspaceIntuneiOSLinuxmacOSManaged SwitchesMicrosoft 365Microsoft DefenderMicrosoft PurviewMta-StsNist 800-171RoutingSpfSshSsh Certificate AuthoritiesTailscaleVlansVpnWindowsWireguard
Aerospace • Defense
Lead design and implementation of hybrid CMMC Level 2 security for cloud and on-premise manufacturing/engineering systems. Partner with non-cyber stakeholders to enable secure workflows, manage SIEM/firewalls/identity/vulnerability tools, produce compliance artifacts (SSPs, RARs, POA&Ms), mentor junior staff, and solve complex network segmentation and OT security challenges.
Top Skills:
Cad/CamCloudDevOpsFirewallsIdentity PlatformsMicro-SegmentationOn-Premise Ot/HardwareSIEMSite-To-Site VpnVulnerability ManagementZero-Trust Network Access

Healthtech • Information Technology
Protect internal and client environments through security operations, incident response, vulnerability management, risk assessments, security monitoring, audits, and continuous improvement. The role investigates alerts and incidents, maintains security controls, supports firewall and cloud security, manages awareness training, develops documentation, and communicates risks and mitigation strategies to stakeholders. This fully remote position supports healthcare organizations in strengthening their cybersecurity posture.
Top Skills:
Active DirectoryCloud PlatformsEndpoint ProtectionFirewallsGroup PolicyIds/IpsMulti-Factor AuthenticationNetworkingSIEMVulnerability Management Platforms

Mining Operations
Cybersecurity intern supporting an IT team in a manufacturing environment. Responsibilities may include vulnerability management, security assessments, configuration reviews, monitoring, investigations, documentation of security controls, and security awareness initiatives across IT and manufacturing OT environments. The intern will research technical questions, troubleshoot issues, document findings, and complete mentored cybersecurity projects.
Top Skills:
BashCis ControlsDnsEndpoint SecurityFirewallsLinuxMfaMicrosoft Entra IdNetwork+NistPowershellPythonSecurity+SIEMTcp/IpVlansVulnerability ScannersWindowsZero Trust

Information Technology • Machine Learning • Professional Services • Security • Consulting
Supports cybersecurity consulting projects involving infrastructure and application security, vulnerability scanning, penetration testing, forensic investigations, incident findings, security documentation, and client workshops. The role also includes client relationship development, proposal writing, and sales-cycle participation. Candidates need IT operations experience, relevant technical exposure, strong communication skills, a degree or progress toward one, occasional travel availability, and U.S. citizenship.
Top Skills:
NessusNmapWireshark

Aerospace • Information Technology • Professional Services • Security • Software
Leads cybersecurity strategy, governance, risk management, architecture, operations, compliance, and incident response for NASA programs. Advises NASA customers and internal stakeholders, oversees cybersecurity and engineering teams, manages audits and continuous monitoring, tracks security metrics, drives technology adoption, and ensures alignment with NASA, NIST, and federal requirements. The role also supports customer relationships, secure service delivery, and cyber program growth.
Top Skills:
Nist Cybersecurity FrameworkServicenow

Biotech
Develop and maintain enterprise cybersecurity strategy, roadmaps, target-state architectures, and security standards. Advise executives and technical teams on cloud, data, AI, application, infrastructure, identity, privacy, and regulatory security. Lead secure AI strategy and governance, assess emerging threats and technologies, guide cybersecurity investments, and support transformation, modernization, and acquisition initiatives.
Top Skills:
Application SecurityArtificial IntelligenceAutonomous AgentsAWSAzureCis ControlsCloud SecurityData ProtectionGenerative AiGoogle Cloud PlatformIdentity And Access ManagementIso 27001Large Language ModelsMachine LearningNist Ai Risk Management FrameworkNist Cybersecurity FrameworkOperational TechnologyZero Trust Architecture

Information Technology • Professional Services • Consulting
Leads cybersecurity engineering, RMF authorization, vulnerability management, system security documentation, architecture security, risk assessments, and classified information protection for Air Force systems. Supports ATO/ATC, continuous monitoring, eMASS administration, ACAS scanning, STIG implementation, cross-domain solutions, policy development, acquisition security, and cybersecurity training. Advises government leadership and coordinates with government and commercial stakeholders to achieve compliance and mission objectives.
Top Skills:
AcasCloud Service ModelsCommercial Solutions For Classified (Csfc)Cross Domain Solutions (Cds)EmassEndpoint SecurityNetwork SecurityNiapNsa Type 1 EncryptionRisk Management Framework (Rmf)StigsTenable NessusUsaf Cds-E

Aerospace
Supports cybersecurity for C-130 and other aeronautical systems at the Air Force Life Cycle Management Center. Advises the ISSM, develops cybersecurity strategies and RMF artifacts, supports IATT and ATO authorization, reviews program documentation, analyzes system components and vulnerabilities, identifies risks and safeguards, and verifies cybersecurity controls and mitigations. Requires aircraft or weapon-system experience, a Secret clearance, U.S. citizenship, and occasional travel.
Top Skills:
AtoAvionics SystemsCybersecurity ControlsIattNetworkingRisk Management Framework (Rmf)Weapon Systems
19 Days AgoSaved
Healthtech • Insurance
Performs risk-based cybersecurity control assessments, technical validation, configuration reviews, vulnerability and exploitability testing, attack-path analysis, and audit support. The role uses GRC and continuous-control-monitoring processes to automate evidence collection, track remediation, develop risk metrics, and improve reporting. Partners with cybersecurity, technology, risk, audit, and business teams to translate technical findings into practical remediation and strengthen cyber resilience.
Top Skills:
Attack-Path AnalysisAutomationCis ControlsCloud SecurityContinuous Control MonitoringData ProtectionEndpoint SecurityGrc PlatformsHipaaHitrustIdentity SecurityIso 27001Mitre Att&CkNetwork SecurityNistPenetration TestingScriptingVulnerability ManagementWorkflow Tools

Information Technology
Support the Air Force Rapid Sustainment Office by executing Risk Management Framework activities for networked, standalone, and cloud systems. Responsibilities include system categorization, security control selection and assessment, vulnerability and risk identification, remediation planning, RMF documentation, policy enforcement, and coordination of accreditation tasks. The role requires independently recommending cybersecurity solutions and applying DoD and Air Force security policies to achieve RMF acceptance and system accreditation.
Top Skills:
Air Force Instruction 17 CyberspaceCloud ComputingCnssi 1253Dod 8570.01-MDodi 8500.01Dodi 8510.01Nist 800-Series Special PublicationsNist Sp 800-53Risk Management Framework (Rmf)

Healthtech
Leads enterprise threat intelligence, detection engineering, threat hunting, phishing resiliency, and AI-enabled security operations. Builds and mentors multidisciplinary cybersecurity teams, advises executives, manages intelligence partnerships and vendors, maps detections to MITRE ATT&CK, directs red and purple team exercises, and drives measurable improvements in detection coverage, response times, control validation, and cyber risk reduction.
Top Skills:
Agentic AiAi-Driven Security SolutionsAutomationCisCyber Threat IntelligenceDetection EngineeringMitre Att&CkNistPurple TeamingRed TeamingSecurity Operations Center (Soc) TechnologiesThreat HuntingThreat Intelligence Platforms
New
Cut your apply time in half.
Use ourAI Assistantto automatically fill your job applications.
Use For Free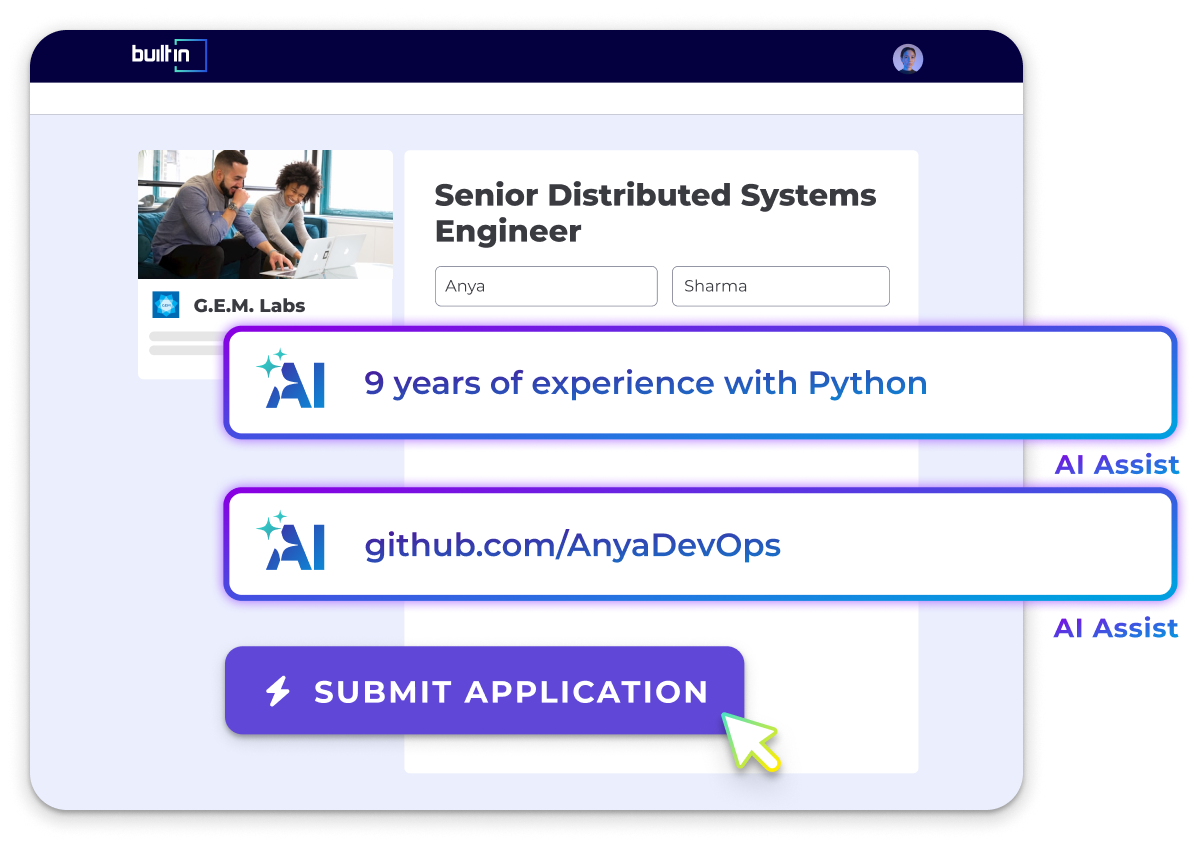

Information Technology • Business Intelligence • Consulting
Leads cybersecurity programs and services for a government client, overseeing governance, risk management, compliance, secure system design, vulnerability management, security operations, and operational defense. Manages project delivery, Agile planning, schedules, budgets, staffing, risks, vendors, deliverables, and stakeholder communications. Oversees recruitment, onboarding, skills assessment, and performance of cybersecurity and technology personnel across development and staff augmentation engagements while ensuring contractual, security, and service-level requirements are met.
Top Skills:
AgileCybersecurity GovernanceRisk ManagementScrumSecurity OperationsSoftware Development Life Cycle (Sdlc)Vulnerability Management

Edtech • Professional Services
Leads cybersecurity governance, risk, and compliance activities, including policy and standards development, third-party risk assessments, internal risk analysis, compliance reporting, regulated-data safeguards, business continuity, awareness training, phishing simulations, and incident-response documentation. Coordinates stakeholders, maintains risk and exception records, supports audits and assessments, and prepares quantitative risk and compliance metrics for senior IT leadership.
Top Skills:
Business ContinuityCmmcCybersecurity GrcDisaster RecoveryFerpaGlbaHipaaIncident ResponseNist Cybersecurity FrameworkNist Sp 800-171Nist Sp 800-53Pci DssPhishing Simulations

Business Intelligence • Consulting • Financial Services
Provide cybersecurity expertise for mission-critical enterprise systems by evaluating security controls, conducting vulnerability assessments and threat modeling, and recommending risk mitigation. Ensure alignment with NIST, ISO 27001, GDPR, and DoD RMF requirements. Collaborate with engineering and leadership to integrate secure development practices, review security tool outputs, mentor teams, and present assessment findings. The role supports government and defense-related environments and requires eligibility for TS/SCI clearance and a CI polygraph.
Top Skills:
Ci/CdCloud SecurityDevsecopsDod RmfEncryptionEndpoint ProtectionFirewallsGdprIamIds/IpsIso 27001Network SecurityNistSdlcSIEMThreat ModelingZero-Trust Architecture

Fintech • Information Technology • Insurance • Financial Services • Big Data Analytics
Provide independent assurance and advisory services over technology, cybersecurity, data, cloud, AI, and business transformation initiatives. Plan and execute audits (risk assessment, scoping, testing, reporting), evaluate ITGCs and automated controls, and use data analytics, automation, and AI tools to improve audit effectiveness and communicate findings to stakeholders.
Top Skills:
AIAnalyticsAutomationCloud TechnologiesCybersecurityData ManagementErpOracleWorkday

Financial Services
Leads Raymond James’s IT compliance program and governance framework. Oversees compliance methodologies, risk assessments, monitoring, testing, and regulatory change management across technology, cybersecurity, privacy, AI, cloud, and third-party risk. Advises senior leadership on emerging compliance risks and partners with technology, security, privacy, legal, risk, audit, and business teams to maintain regulatory compliance and independent oversight.
Top Skills:
Artificial IntelligenceCloud ComputingCybersecurityData GovernanceData PrivacyDatabasesInformation SecurityInformation TechnologySpreadsheets
Greentech • Other
Serves as the strategic bridge between Cybersecurity and IT Infrastructure teams and the Digital organization. Advises senior leaders, communicates security and infrastructure risks, reports on program progress, defines cybersecurity requirements, coordinates third-party risk assessments, supports transformation initiatives, promotes security policies, and partners with Compliance, Legal, and IT teams to deliver secure, scalable infrastructure.
Top Skills:
Application DevelopmentCybersecurityIt InfrastructureSecurity And Privacy Compliance

Information Technology
Designs and develops secure systems and architectures for U.S. Navy missions. Responsibilities include analyzing engineering and security requirements, hardening systems, reducing attack surfaces, applying secure coding and operating-system security practices, evaluating architectures against adversary threats, and implementing cybersecurity countermeasures across system lifecycles.
Top Skills:
CameoCross Domain SolutionsCryptographic AlgorithmsCybersecurityFpga SecurityMagicdrawOperating SystemsSecure CodingVirtualization
Big Data • Fintech • Mobile • Payments • Financial Services
The CISO will develop and manage the Bank's information security programs, ensuring compliance and protecting customer data while mitigating risks. They will also lead a security team, oversee third-party risk, and promote a culture of security awareness across the organization.
Top Skills:
Cloud ComputingCompliance (FdicCybersecurityFfiec)Incident ResponseInformation Security FrameworksRisk ManagementSecurity Operations

Fintech
The Sr. Manager of Information Risk & Controls drives the risk management evolution by leading risk identification, developing frameworks, and collaborating with teams across Invesco.
Top Skills:
Artificial IntelligenceAWSAzureCloud ComputingCybersecurityData GovernanceGCPIso 27000 SeriesMachine LearningNist Csf

Edtech
Conduct mixed-method behavioral research on cybersecurity, privacy, artificial intelligence, risk, trust, and human behavior. Design and lead interviews, focus groups, surveys, and experiments; analyze quantitative and qualitative data; publish findings; support grant proposals; mentor student researchers; manage project milestones; and disseminate results with interdisciplinary and international collaborators.
Top Skills:
Artificial IntelligenceCybersecurityHlmMatlabPrivacyPythonRSem

Fintech • Financial Services
Lead Citi’s enterprise Insider Threat program within the Cybersecurity Fusion Center. Responsibilities include defining strategy, managing and developing multidisciplinary teams, implementing data-centric detection and response processes, applying AI and advanced analytics, integrating behavioral and technical indicators, advising senior stakeholders, coordinating governance and risk controls, and engaging industry and government partners. The role requires extensive cybersecurity leadership, insider threat expertise, incident response experience, and the ability to drive global transformation.
Top Skills:
Artificial IntelligenceCybersecurityData AnalyticsMachine LearningThreat Intelligence Platforms
Fintech • Financial Services
Lead the development and execution of Citi’s enterprise insider threat program. Responsibilities include strategic planning, AI-driven threat detection, data-centric process implementation, threat triage and response, stakeholder engagement, governance, risk management, metrics, reporting, and incident response support. The role partners with cybersecurity, legal, HR, compliance, risk, technology teams, industry peers, vendors, and government agencies while helping drive organizational transformation and mentor team members.
Top Skills:
Artificial IntelligenceCybersecurityCybersecurity Fusion CentersData AnalyticsMachine LearningThreat Intelligence Platforms

Aerospace • Logistics • Transportation • Defense
Leads cybersecurity integration for newly acquired sites, including security assessments, firewall and VPN deployment, network segmentation, Zero Trust and Entra ID configuration, EDR and SIEM onboarding, email security, vendor coordination, documentation, and operational handoff. The role independently owns security architecture from assessment through steady-state transition, with approximately 75–80% travel to domestic and international acquisition sites and occasional after-hours or weekend cutovers.
Top Skills:
AclsCiscoCmmcConditional AccessDlpDynamic RoutingEdrEmail SecurityFirewallsFortinetIdentity ProtectionMfaMicrosoft 365Microsoft Entra IdNetwork SegmentationNgfwNist CsfNist Sp 800-171Palo AltoPowershellPythonSIEMVlansVpnZero Trust Network Access

Let Your Resume Do The Work
Upload your resume to be matched with jobs you're a great fit for.
Success! We'll use this to further personalize your experience.
Top Companies Hiring Cybersecurity Roles
See All






Popular Job Searches
All Filters
Total selected ()
No Results
No Results
