

Maximum of 25 job preferences reached.
Top Cybersecurity Jobs
Energy • Cybersecurity • Defense • Industrial
Analyzes and mitigates information-system security risks through vulnerability assessment, penetration testing, cyber defense capability development, RMF/SA&A implementation, and security operations support. The role designs cybersecurity tools, evaluates hardware and software, manages security documentation, supports incident handling and training, and collaborates with ISSMs, ISSOs, and technical stakeholders. Work includes prototype development, data-management capabilities, technology research, and risk assessments for enterprise and portable electronic devices.
Top Skills:
Cloud ComputingCryptographic Key ManagementData MiningData WarehousingDoe Order 206.1AIcs/ScadaNist Sp 800-53Omb Circular A-130Penetration TestingPit SystemsRmfSa&ASplunk

Appliances • Industrial
Cybersecurity Intern supporting security operations, vulnerability management, incident response, security awareness, IAM, and risk management. Responsibilities include monitoring and triaging alerts, assisting with vulnerability remediation, participating in investigations, reviewing SOC reports, supporting phishing simulations and IAM projects, and developing automation scripts. The role provides hands-on experience with enterprise security tools and processes while collaborating with cybersecurity professionals across a global organization.
Top Skills:
DnsEdrIamAzureMicrosoft Defender For EndpointMicrosoft Entra IdMicrosoft SentinelPowershellSIEMTcp/IpVpnWindows
Reposted One Month AgoSaved
Automotive • Big Data • Information Technology • Robotics • Software • Transportation • Manufacturing
Lead and execute adversary emulation and purple team operations to validate detections, logging, and response. Build repeatable MSV-based validation workflows, develop custom offensive tooling (C2, payloads, automation), test cloud and endpoint attack paths (AWS, GCP, Azure), and partner with Detection Engineering and Incident Response to convert findings into improved detections, documentation, and hunts.
Top Skills:
Att&CkAWSAzureC2 FrameworksGCPMsv

Information Technology • Professional Services • Cybersecurity • Defense
Serves as the Cybersecurity and Computer and Network Defense Subject Matter Expert, overseeing the technical and operational effectiveness of capabilities in coordination with government customer representatives and sponsor staff. Requires 11 years of relevant experience, a bachelor’s degree, and an active TS/SCI clearance with Full Scope Polygraph.
Top Skills:
Computer And Network DefenseCybersecurityFull Scope PolygraphTs/Sci
Information Technology • Professional Services • Cybersecurity • Defense
Ensures systems and products meet government cybersecurity and information assurance standards through verification, validation, testing, threat analysis, and design reviews. Develops cyber threat profiles, evaluates security performance, maintains analytical procedures, prepares technical recommendations for government intelligence and operations officials, and supports the security posture of networks and systems.
Top Skills:
A+CybersecurityInformation AssuranceNetwork OperationsNetwork+Security+

Artificial Intelligence • Computer Vision • Machine Learning • Robotics • Defense • Manufacturing
Build and operate CrowdStrike Falcon Next-Gen SIEM detection and monitoring capabilities. Responsibilities include onboarding and normalizing log sources, authoring and tuning CQL searches and detection rules, maintaining dashboards, integrating telemetry across endpoint, identity, and cloud environments, reducing false positives, and partnering with IT and engineering to close security gaps and improve compliance readiness.
Top Skills:
AWSAzureCi/CdCrowdstrike CqlCrowdstrike Falcon EdrCrowdstrike Falcon Next-Gen SiemCrowdstrike Parsing StandardCspmEcsFalcon Fusion SoarGCPGitKubernetesTinesTorqXsoar
Healthtech • Insurance • Pet
Supports security operations and incident response through alert monitoring, threat investigation, containment, evidence preservation, threat intelligence, threat hunting, vulnerability prioritization, automation, and case management. The role investigates identity, endpoint, cloud, email, network, application, third-party, AI, and breach-related security events; coordinates remediation with asset owners; maintains security metrics and documentation; and participates in business-hour coverage and on-call escalation.
Top Skills:
AzureCysa+Edr/XdrGciaGcihIso 27001Microsoft 365Microsoft DefenderMicrosoft SentinelMitre Att&CkNist CsfNydfs Cybersecurity RequirementsPci DssSc-200Security+SIEM

Reposted 14 Days AgoSaved
Healthtech • Professional Services • Software • Telehealth
Lead technology strategy, cybersecurity, infrastructure, compliance (HIPAA, NIST, SOC 2, HITRUST, FedRAMP), product security, cloud operations, vendor management, incident response, and AI governance. Oversee reliability, disaster recovery, secure development practices, audits, and cross-functional partnerships to support healthcare and public-sector customers.
Top Skills:
Ai And Machine LearningBackup And RecoveryCloud PlatformsDevsecopsEndpoint ProtectionFedrampGovrampHipaaHitrustIdentity And Access ManagementIso 27001Logging And MonitoringMobile Application SecurityNist 800-171Nist 800-53Nist CsfSaaSSoc 2
Financial Services
Lead cybersecurity strategy and architecture across products, applications, and technologies. Advise engineering teams, communicate complex risks to leadership, develop reusable security frameworks, create mitigation solutions, and evaluate emerging technologies. The role requires influencing cross-functional teams, shaping enterprise-wide architecture, and applying cloud-native, application, API, web, and mobile security expertise across a complex financial-services environment.
Top Skills:
Api SecurityArtificial IntelligenceCloud-Native TechnologiesCybersecurity ArchitectureMachine LearningMobile Application SecurityWeb Application Security
Professional Services
Supports cybersecurity consulting engagements involving IT audits, SOC examinations, IT risk assessments, controls-based audits, regulatory compliance reviews, and cybersecurity maturity assessments using frameworks such as NIST, PCI DSS, and ISO. Conducts research and special analyses, builds client relationships, and participates in networking and business development. The role requires pursuing a relevant bachelor's degree, strong analytical and communication skills, a minimum 3.0 GPA, and potential travel.
Top Skills:
IsoNistPci Dss

Other
Designs and oversees enterprise cybersecurity architecture, networks, policies, and information security systems for the judicial branch. Responsibilities include cloud security, firewall and segmentation design, threat and vulnerability analysis, incident response, disaster recovery coordination, compliance, security testing, audits, stakeholder collaboration, and staff training. The role also researches security technologies, supports regulatory compliance, and requires occasional out-of-state travel.
Top Skills:
AWSAzureCloud SecurityDfirFirewallsGdprGCPIds/IpsIncident ResponseNist Csf 2.0Pci-DssVpn

Information Technology
Build and operate cybersecurity AI infrastructure supporting model training, evaluation, deployment, and serving. Develop Databricks and AWS platforms, security telemetry pipelines, GitHub Actions CI/CD, DevSecOps controls, infrastructure as code, identity and secrets management, and model evaluation workflows. Partner with AI/ML engineers, data scientists, and security operators while conducting technical reviews and guiding platform design.
Top Skills:
SparkAWSAws OidcAws Secrets ManagerDatabricksDatabricks Asset BundlesDockerGithub ActionsIamKubernetesMitre AtlasMlflowNist Ai RmfOwasp Llm Top 10PythonPytorch DistributedRaySIEMSoarSQLTerraformTerragrunt
New
Cut your apply time in half.
Use ourAI Assistantto automatically fill your job applications.
Use For Free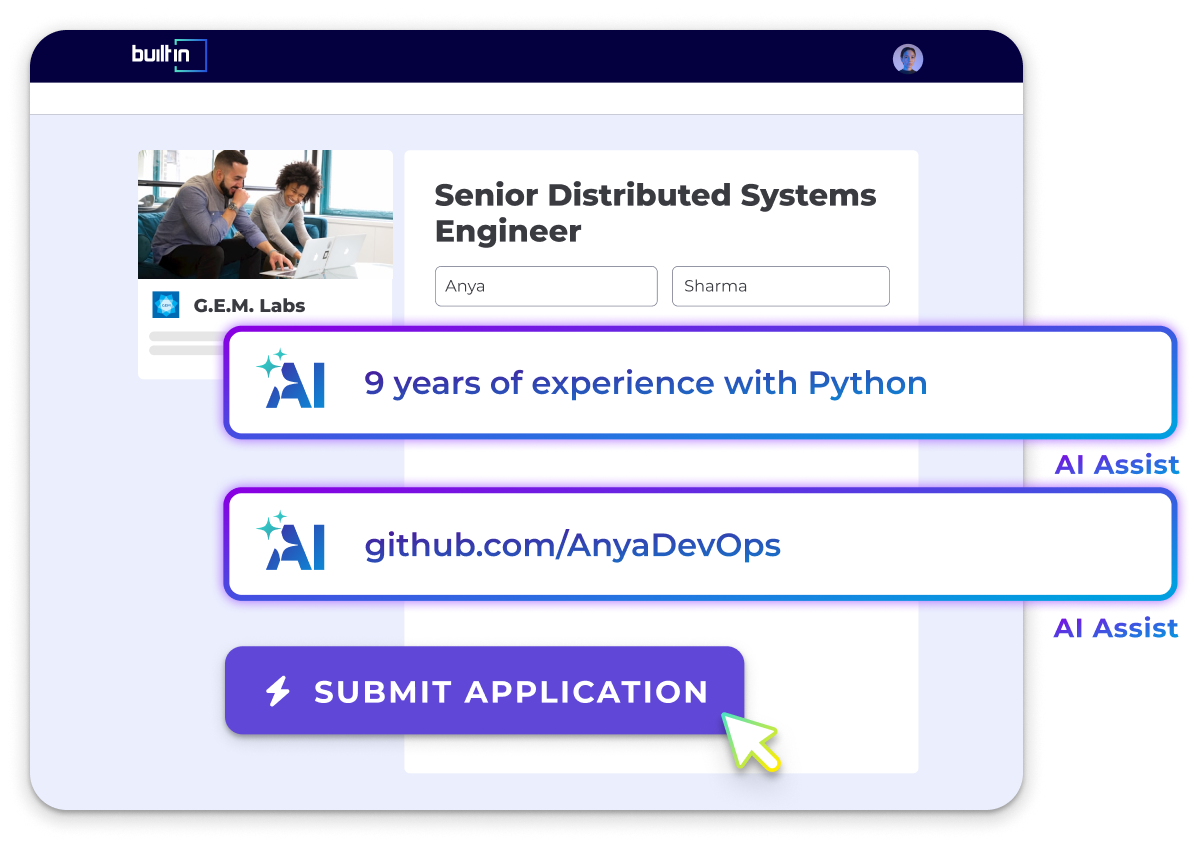
Information Technology
Build and operate Booz Allen’s cybersecurity AI infrastructure platform using Databricks, AWS, GitHub Actions, and infrastructure as code. Develop governed security telemetry pipelines, model evaluation and serving workflows, CI/CD, DevSecOps controls, and repeatable deployments. Partner with AI engineers, data scientists, and security operators to operationalize agentic AI capabilities. Lead technical design, code reviews, platform direction, and production monitoring while enforcing least-privilege access and secure handling of sensitive data.
Top Skills:
SparkAWSAws IamAws OidcAws Secrets ManagerDatabricksDatabricks Asset BundlesDockerGitGithub ActionsKubernetesMitre AtlasMlflowNist Ai RmfOwasp Llm Top 10PythonPytorch DistributedRaySIEMSoarSQLTerraformTerragruntUnity Catalog

Aerospace
Designs and implements cybersecurity architecture across corporate and development environments. Translates NIST SP 800-171 and CMMC Level 2 requirements into technical controls, supports ATO activities, and partners with infrastructure teams on Palo Alto architecture, segmentation, remote access, and network rules. Defines CUI boundaries, data flows, and security diagrams while addressing gaps across cloud, SaaS, endpoints, networks, servers, and software services.
Top Skills:
AWSAws GovcloudCmmc Level 2ContainersCrowdstrike FalconCyberarkElasticEndpoint SecurityEntra IdKubernetesMicrosoft Gcc HighMicrosoft IdentityNetwork SecurityNist Sp 800-171Palo AltoSIEMTenableTerraformVulnerability Management

Information Technology • Software • Cybersecurity • Defense
Develop and maintain RMF security artifacts for federal building and facility control systems. Gather technical information, support system categorization and risk assessments, review vulnerability scans, create and track POA&Ms, assist with STIG compliance, maintain system inventories, and coordinate with government cybersecurity teams, system owners, engineers, and security officers to support ATO activities and recurring reporting.
Top Skills:
AcasCnssi 1253EmassFedrampFips 199Fips 200Nist Sp 800-53Nist Sp 800-82Ot/Ics/ScadaPurdue Enterprise Reference ArchitectureRmfScapSecurity+ CeStigZero Trust
Information Technology • Software • Cybersecurity • Defense
Leads onsite cybersecurity operations for federal facility and control systems. Responsibilities include patching, hardening, monitoring, vulnerability management, RMF documentation, system inventories, compliance, ATO readiness, and coordination with government cybersecurity teams, facility personnel, OEM vendors, and stakeholders. Supervises two RMF Specialists, mentors staff, supports risk assessments, and leads cyber phase-in and transition activities.
Top Skills:
Advanced MeteringBuilding Automation SystemsCnssi 1253FedrampFips 199Fips 200LinuxNist Sp 800-53Nist Sp 800-82Ot/Ics/ScadaPurdue Enterprise Reference ArchitectureRmfZero Trust

Information Technology
Monitor SIEM and cybersecurity tools in a 24x7x365 environment; detect, analyze, and respond to threats, unauthorized activity, APTs, and attacks. Review logs and network traffic, conduct root cause analysis, use threat intelligence and OSINT, support cybersecurity tools, and implement Defense-in-Depth controls. Develop scripts and tools using SPL, Python, or PowerShell to improve detection and incident response capabilities.
Top Skills:
Data Loss PreventionDevice HardeningDigital ForensicsFirewallHost-Based AntivirusIds/IpsMalware AnalysisOsintPowershellPythonSIEMSplVulnerability Management

Automotive • Professional Services • Software • Consulting • Energy • Chemical • Renewable Energy
Supports global cybersecurity governance, risk, and compliance programs by administering KnowBe4, coordinating awareness campaigns and phishing simulations, maintaining policies and governance records, tracking metrics and remediation, supporting audits and evidence collection, and preparing dashboards and executive reports. The role also assists with ServiceNow governance workflows, AI and non-human identity governance, stakeholder coordination, and process improvement.
Top Skills:
Cis ControlsIso 27001Knowbe4ExcelMicrosoft PowerpointMicrosoft TeamsMicrosoft WordNist 800-53Nist Cybersecurity FrameworkServicenow
Aerospace • Information Technology • Software
Lead DoD Risk Management Framework authorization activities across system development, testing, authorization, and operations. Develop and maintain ATO/IATT packages, SSPs, POA&Ms, security control documentation, and assessment evidence in eMASS. Analyze NIST, DISA STIG, vulnerability, and configuration requirements; coordinate with ISSMs, ISSOs, SCAs, AOs, engineers, and government stakeholders. Support continuous monitoring, system changes, vulnerability remediation, security assessments, and secure configuration guidance across Linux, Windows, network, and virtualized environments.
Top Skills:
AcasAtoCnssi 1253Disa StigsDodi 8510.01EmassFirewallsHyper-VIattKvmLinuxNessusNetwork SegmentationNist Sp 800-37Nist Sp 800-53RmfRoutingScapStig ViewerSubnetsTcp/IpVlansVMwareWindows
Financial Services
Participate in a 9-week onsite cybersecurity internship supporting security assessments, vulnerability scanning, threat monitoring, penetration testing, red teaming, and AI testing. Work with security engineers to design and maintain cybersecurity solutions, prepare threat models, execute test cases, compile reports, and establish testing infrastructure for web and mobile applications.
Top Skills:
Ai TestingApplication SecurityMobile Application SecurityNetwork SecurityPenetration TestingRed TeamingThreat MonitoringVulnerability ScanningWeb Application Security

Information Technology • Consulting
Supports client and internal cybersecurity compliance programs through control assessments, evidence review, risk analysis, policy and documentation development, vendor cybersecurity reviews, and audit coordination. The role prepares remediation roadmaps, risk summaries, control crosswalks, inventories, and audit materials while applying NIST, CIS, SOC 2, and ISO 27001 frameworks. It also translates technical findings into clear client deliverables and helps maintain compliance templates and processes.
Top Skills:
Cis ControlsCjisCmmcFedrampHipaaIso/Iec 27001Microsoft 365Microsoft Entra IdMicrosoft IntuneNist Cybersecurity Framework (Csf)Nist Sp 800-53Soc 2 Type Ii
Information Technology
Leads multiple Enterprise Security Operations Center teams monitoring classified and unclassified networks. Oversees incident detection, analysis, response, remediation, post-incident reviews, and root-cause planning. Provides technical guidance, manages projects, coordinates with IT teams and external partners, and communicates cybersecurity concepts to technical and non-technical stakeholders. Requires Top Secret clearance, relevant degree, cybersecurity experience, and CISM or CEH certification.
Top Skills:
FirewallsIntrusion Detection And Prevention Systems (Idps)Log AnalysisSecurity Information And Event Management (Siem)
Aerospace
Maintains cybersecurity operations and security posture for an Air Force logistics system. Integrates cybersecurity throughout the system lifecycle, monitors security events and configuration changes, manages authorization and corrective actions, maintains documentation, reports cybersecurity impacts, and ensures personnel training, certifications, clearances, and compliance with Department of War and Air Force cybersecurity requirements.
Top Skills:
Agile DevelopmentCloud ComputingRisk Management Framework (Rmf)

Information Technology
Leads global managed cybersecurity service delivery, including MDR, CTEM, cloud security, SOC operations, governance, client outcomes, and service performance. Owns managed-services growth, revenue, margins, forecasting, modernization, AI adoption, transformation programs, and executive client relationships. Builds and develops distributed cybersecurity teams while partnering cross-functionally on portfolio strategy, delivery quality, operational resilience, and business expansion.
Top Skills:
AIAnalyticsAutomationCloud SecurityCtemIncident ResponseMdrSIEMSocVulnerability Management

Information Technology • Professional Services • Defense • Manufacturing
Provides governance, risk, and compliance support for federal information systems under FISMA and the NIST RMF. Manages authorization activities, reviews FedRAMP packages, evaluates security controls, conducts risk and gap assessments, maintains SSPs, SARs, SAPs, and POA&Ms, and supports continuous monitoring. The role collaborates with system owners, ISSOs, cloud providers, and senior stakeholders; prepares compliance reporting and oversight responses; and contributes to cybersecurity policy, control tailoring, remediation, and quality assurance activities.
Top Skills:
Atlassian ConfluenceCsamFedrampFismaJIRAMicrosoft 365Nist Risk Management FrameworkNist Sp 800-30Nist Sp 800-37Nist Sp 800-53Servicenow

Let Your Resume Do The Work
Upload your resume to be matched with jobs you're a great fit for.
Success! We'll use this to further personalize your experience.
Top Companies Hiring Cybersecurity Roles
See All






Popular Job Searches
All Filters
Total selected ()
No Results
No Results
