

Maximum of 25 job preferences reached.
Top Cybersecurity Jobs

Food • Hospitality
Leads Brinker International’s enterprise cybersecurity strategy, threat detection, incident response, resilience, governance, compliance, vendor risk management, and restaurant payment security. Oversees protection of corporate, cloud, restaurant, and third-party environments while ensuring PCI DSS, SOX, privacy, and security framework compliance. Manages cybersecurity teams, audits, assessments, training, business continuity, and executive risk communication.
Top Skills:
Cloud InfrastructureHybrid InfrastructureIn-Store NetworksIso 27001NistPayment Processing SystemsPci DssPoint-Of-Sale SystemsSaaSSox
Professional Services
Lead and operate security control domains (identity, cloud, network, endpoint, monitoring). Deploy and harden tools, author architecture and runbooks, lead cross-team rollouts, mentor engineers, support SOC detection/response, and maintain audit-ready evidence and automation.
Top Skills:
AWSAzureBicepCentralized LoggingCloud SecurityEdrEncryptionEndpoint SecurityGCPIamIdentity ManagementInfrastructure-As-CodeKey ManagementLogging PipelinesMonitoringNetwork SegmentationOpaPolicy-As-CodePulumiSecrets ManagementSentinelSIEMTerraformVulnerability Scanning

Logistics • Transportation • Industrial
Manage security, compliance, and risk authorization for a DevSecOps software factory. Execute DoD RMF processes, maintain eMASS A&A artifacts, validate NIST and CNSSI controls, oversee vulnerability remediation and STIG compliance, conduct security impact and risk assessments, monitor logs, support incident response, and integrate security requirements into DevSecOps pipelines.
Top Skills:
AcasCnssi 1253 Rev. 5DevsecopsEmassIavm/DtoLinuxNist Sp 800-53 Rev. 5Risk Management Framework (Rmf)StigWindows

Information Technology • Professional Services • Consulting • Defense
Manage security, compliance, and authorization for a DevSecOps software factory platform. Execute DoD RMF and A&A processes; maintain SSPs, POA&Ms, SARs, and ATO artifacts in eMASS. Validate vulnerability scanning, patching, hardening, and STIG compliance across Linux, Windows, and network devices. Conduct risk assessments and security impact assessments, monitor logs, support incident response, maintain compliance dashboards, and advise engineering and DevSecOps teams on security requirements.
Top Skills:
AcasCnssi 1253 Rev. 5DevsecopsDod RmfEmassIavm/DtoLinuxNist Sp 800-53 Rev. 5StigsWindows
Information Technology • Professional Services • Cybersecurity
Develops AI-enabled software and rapid prototypes to improve defensive cybersecurity operations. The role collaborates with mission operators and applies Python, LLMs, and corporate AI resources to support vulnerability analysis, patching, incident response, adversary emulation, threat analysis, and COMSEC monitoring for government and Defense Industrial Base environments.
Top Skills:
Artificial IntelligenceLarge Language Models (Llms)PythonSoftware Development
Information Technology • Professional Services • Cybersecurity
Supports cybersecurity compliance and authorization activities for Naval Nuclear Laboratory systems, including NIST and RMF directives, security plans, assessment reports, POA&Ms, risk-based decisions, and compliance remediation. The role assists system owners with authorization packages using RSA Archer and ensures adherence to DOE, NNL, DoD, and applicable cybersecurity standards. Regular onsite work is required in Niskayuna, NY, or West Mifflin, PA, with remote work permitted 25% of the time.
Top Skills:
CcskCisspDod Cloud Computing SrgFedrampLan/WanNistNist 800-171Risk Management Framework (Rmf)Rsa ArcherSaaSSecurity+ CeStigs

Consulting
Leads vulnerability management across client applications, including analyzing findings, assigning remediation, tracking closure, and validating fixes. Supports POA&M activities, federal cybersecurity compliance, patching deadlines, dashboards, KPIs, leadership briefings, Splunk alert monitoring, secure development, audits, and assessments. Requires cybersecurity or IT risk management experience, federal Public Trust eligibility, and familiarity with vulnerability tools, NIST, FISMA, and OWASP.
Top Skills:
APIsAtlassian JiraConfluenceCvss V3EpssFismaInvictiMitre Att&CkNist Sp 800-53Owasp Top 10Power BISplunk
Consulting
Leads cybersecurity risk management across client applications, managing POA&M lifecycles, prioritizing remediation, conducting business impact analyses, and maintaining continuity documentation. The consultant coordinates with system owners, engineering, and security teams; validates fixes; prepares leadership and federal oversight reports; supports audits and assessments; and applies NIST, FISMA, and federal security requirements.
Top Skills:
APIsCvss V3EpssFismaGrc PlatformsMitre Att&CkNist Sp 800-37Nist Sp 800-53Power BI
Information Technology • Software
Investigate and triage advanced security alerts across endpoint, identity, email, and network telemetry. Lead Tier 2 incident response through containment, eradication, and recovery; document investigations, escalate high-severity incidents, produce customer-facing summaries, mentor Tier 1 analysts, and improve SOC processes and detection workflows.
Top Skills:
EdrEmail SecurityEndpoint SecurityFirewallsIdentity SecurityMicrosoft SentinelSIEMSoc Mdr

AdTech • Beauty • Marketing Tech • Retail • Pharmaceutical
Protect P&G’s global IT environment from cyber threats through security engineering or analysis. Responsibilities include designing and monitoring security platforms, investigating incidents, responding to threats, assessing vulnerabilities, driving remediation, researching emerging attack techniques, strengthening security controls, and communicating risks to technical and business stakeholders.
Top Skills:
Ci/CdCybersecurity

Information Technology
Lead cross-functional cybersecurity programs spanning product, cloud, enterprise, vulnerability management, compliance, and incident readiness. Own roadmaps, budgets, risks, dependencies, metrics, executive reporting, assessments, audits, certifications, and vendor engagements. Coordinate incident response and remediation while partnering with engineering, IT, legal, privacy, compliance, and business teams. Track emerging risks and regulatory requirements, strengthen security-by-design practices, and use AI and automation to improve execution.
Top Skills:
AIAutomationBug Bounty ProgramsCloud SecurityCompliance FrameworksCybersecurityEnterprise SecurityIncident ResponsePenetration TestingProduct SecuritySecurity AssessmentsSecurity CertificationsSecurity DashboardsVulnerability Management

Information Technology • Consulting • Cybersecurity
Provides cybersecurity engineering leadership for classified DoD and U.S. Space Force systems. Designs and assesses security solutions, integrates controls across networks, supports RMF and ATO activities, conducts risk analyses, evaluates system changes, and ensures compliance with NIST, DoD, DAF, and Intelligence Community requirements. The role coordinates with government stakeholders and technical teams, tracks remediation activities, and presents security findings and recommendations to senior leadership.
Top Skills:
Authorization To Operate (Ato)Classified NetworksDod Cybersecurity StandardsIntelligence Community Cybersecurity StandardsNistRisk Management Framework (Rmf)
New
Cut your apply time in half.
Use ourAI Assistantto automatically fill your job applications.
Use For Free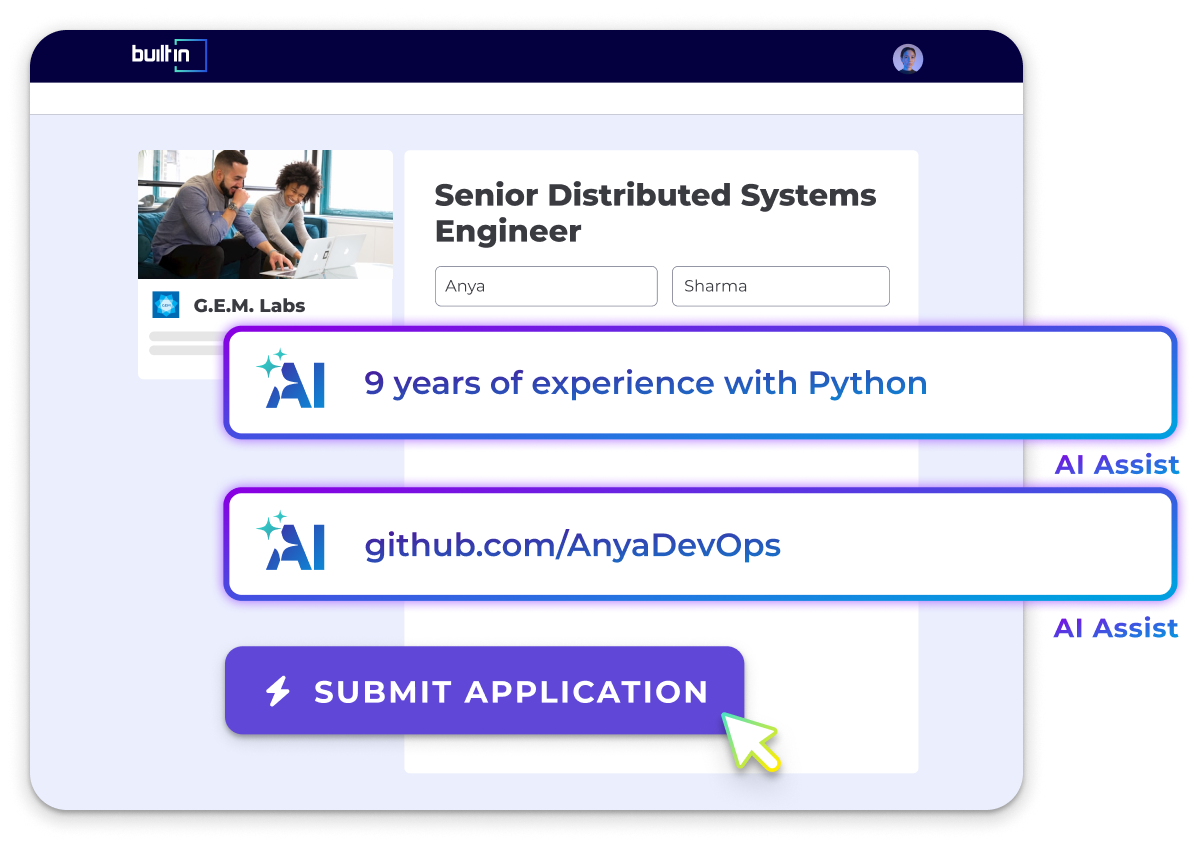
Information Technology • Consulting • Cybersecurity
Serves as the primary cybersecurity advisor for assigned DoD information systems. Implements, assesses, and maintains RMF security controls; identifies risks, vulnerabilities, and compliance issues; advises leadership; and ensures alignment with DoD cybersecurity policies. The role supports SAP/SCI environments, collaborates with engineering and program teams, and requires an active high-level security clearance, extensive DoD cybersecurity experience, and occasional travel.
Top Skills:
Casp+Dod Risk Management Framework (Rmf)Securityx
Consulting
Leads and grows a global digital risks and cybersecurity consulting business. Responsibilities include strategy, business development, sales, complex cyber advisory and incident response engagements, AI risk and governance services, threat analysis, executive recommendations, project profitability, team leadership, recruitment, and mentoring. The role advises clients on cyber resilience, information security risk, governance, forensics, analytics, emerging technology risk, and multi-jurisdictional cyber investigations.
Top Skills:
Ai Risk GovernanceAnalyticsComputer ForensicsCyber Incident ResponseCybersecurityData Loss PreventionElectronic DiscoveryInformation ProtectionInformation SecurityIso 27001Iso/Iec 42001NistThreat Intelligence
AdTech • Beauty • Marketing Tech • Retail • Pharmaceutical
Supports P&G’s Cyber Defense organization by helping design, test, deploy, monitor, and improve security solutions. Interns may investigate cybersecurity incidents, identify vulnerabilities, drive remediation, research emerging threats and tactics, and strengthen security controls across networks, applications, infrastructure, and CI/CD pipelines. The role also involves communicating security risks, collaborating with cross-functional teams, and promoting compliance with cybersecurity standards and best practices.
Top Skills:
Ci/Cd PipelinesCyber Threat IntelligenceCybersecurityIncident ResponsePenetration TestingSecurity InfrastructureVulnerability Management
Greentech
Designs and evolves secure, resilient IT and OT infrastructure and network architectures. The role eliminates single points of failure, strengthens business continuity, identifies and mitigates cyber vulnerabilities, validates managed service provider remediation, and protects manufacturing systems, legacy operating systems, and critical business products. Responsibilities include Microsoft and VMware infrastructure, redundant networking, security controls, scripting automation, and collaboration with OT engineers and product owners.
Top Skills:
Azure AdBashCis ControlsCyberarkIcsIds/IpsMerakiMicrosoft 365Microsoft DefenderMicrosoft Entra IdMicrosoft IntuneMicrosoft SentinelNist CsfOt SecurityPowershellSIEMSoarVMwareWafWindows ServerZero Trust

AdTech • eCommerce • Food • Marketing Tech • Retail
The Security Engineering Manager oversees security policies, manages incident responses, monitors threats, and coordinates investigations to protect the technology environment. They also handle reporting and assurance on security incidents and ensure operational stability.
Top Skills:
Cis ControlsIso/Iec 27001Mitre Att&CkNistSIEMSoc
AdTech • eCommerce • Food • Marketing Tech • Retail
The Security Engineering Manager safeguards technology by enforcing security policies, managing incident responses, monitoring threats, and reporting on security incidents. Must collaborate across IT and business functions, ensuring compliance and conducting training.
Top Skills:
Cis ControlsIso/Iec 27001Mitre Att&CkNistSIEMSoc

Information Technology • Software • Analytics • Cybersecurity
Designs and maintains cybersecurity assurance processes, conducts system and network security assessments, evaluates defense-in-depth effectiveness, validates security requirements, supports certification and accreditation, executes Security Test and Evaluation activities, monitors corrective actions, and guides junior cybersecurity personnel. May lead teams or tasks without direct people-management responsibility.
Top Skills:
Certification And Accreditation (C&A)CybersecurityDcid 6/3NispomSecurity Test And Evaluation (St&E)

Aerospace • Logistics • Security • Software • Cybersecurity
Develops and validates hardware and software security solutions for DoD sensor payloads and mission systems. Responsibilities include systems security architecture, requirements development, anti-tamper and cybersecurity implementation, reverse engineering, security testing, RMF compliance, technical release analysis, exportability assessments, cryptographic protection, A&A documentation, and POA&M maintenance. The role collaborates with government, program, business development, and international stakeholders and provides technology-release training. This is a full-time, on-site position in Rolling Meadows, Illinois.
Top Skills:
Anti-TamperAssessment And AuthorizationCnssi 1253Cryptographic Security ProtocolsCybersecurityCybersecurity Risk Management FrameworkDaapmDodi 5200.39Firmware EncryptionHardware AssuranceJsigNist 800-53Poa&MReverse EngineeringSecure Key HandlingSecurity Test And EvaluationSoftware EncryptionSystems Engineering
Aerospace • Logistics • Security • Software • Cybersecurity
Develop and integrate hardware and software anti-tamper and cybersecurity solutions for DoD sensor, targeting, and electronic warfare systems. Perform secure architecture, requirements development, security testing, validation, reverse engineering, risk management, technical release analyses, exportability assessments, and compliance with U.S. Government security policies. Support Assessment and Authorization, Security Plans, POA&Ms, technology release training, cryptographic security, and collaboration with government and international program stakeholders.
Top Skills:
Anti-TamperAssessment And AuthorizationCnssi 1253Cryptographic Security ProtocolsCybersecurityCybersecurity Risk Management FrameworkDaapmDodi 5200.39JsigNist 800-53Poa&MReverse EngineeringSecurity Test And EvaluationSystems Engineering

Fintech • Payments
Leads enterprise cybersecurity governance, risk, and compliance initiatives; independently addresses complex security risks, develops mitigation strategies, establishes governance methods, and guides cross-functional teams. The role sets priorities for a security risk and governance team, drives high-impact improvements, and mentors team members. Requires 8+ years of relevant experience and a bachelor’s degree or equivalent combination of education and experience.
Aerospace • Logistics • Security • Software • Cybersecurity
Leads a team of information system security professionals supporting classified systems and secure networks. Oversees cybersecurity compliance, risk mitigation, Assessment and Authorization, certification testing, documentation, audits, inspections, investigations, and accreditation. Implements government policies and security frameworks, develops process improvements, ensures continuous compliance, and coordinates with executives, program management, and customers. Provides mentorship, training, performance management, and financial oversight while supporting systems requiring Top Secret clearance and SAP/SAR eligibility.
Top Skills:
Assessment And Authorization (A&A)CcisoCismCisspCybersecurityDaagGslcIcdsInformation SystemsJsigNetwork SecurityRisk Management Framework (Rmf)Special Access Programs (Sap/Sar)

Biotech
Leads product cybersecurity and regulatory compliance for regulated products. Responsibilities include threat modeling, security architecture reviews, risk assessments, secure SDLC guidance, vulnerability remediation, SBOM and supply-chain security, regulatory submission evidence, audits, and cross-functional cybersecurity workstream coordination.
Top Skills:
AWSHitrustIso 27001Nist CsfSbomSecure Product Development Framework (Spdf)Secure SdlcThreat Modeling

Information Technology
As an IAM Engineer, you'll support IAM projects for government clients, manage user privileges, and help secure identities against cyber threats.
Top Skills:
Active DirectoryCybersecurityElk StackIcamLdapMicrosoft Identity ManagerOne IdentityPingidentityPivPkiSailpointSaviyntSecurity ArchitectureSecurity OperationsSplunkThreat Response

Let Your Resume Do The Work
Upload your resume to be matched with jobs you're a great fit for.
Success! We'll use this to further personalize your experience.
Top Companies Hiring Cybersecurity Roles
See All






Popular Job Searches
All Filters
Total selected ()
No Results
No Results
