We are seeking a hands-on SecOps Specialist with strong SIEM/SOAR and Cyber Analyst capabilities.
You will work closely with SOC analysts, IT, cloud, infrastructure, and engineering teams to improve security visibility, reduce response times, and continuously enhance the organization’s cyber resilience.
The ideal candidate combines strong analytical and investigative capabilities with practical experience in security monitoring, log analysis, detection engineering, scripting, and security-tool integrations.
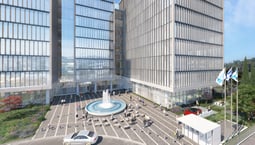
This position requires on-site presence at our Jerusalem campus 4 days per week, with the option to work from home one additional day.
What will your job look like:
Develop, test, tune, and maintain SIEM detection rules, correlation logic, dashboards, and alert thresholds.
Integrate security tools and services using APIs, webhooks, scripts, and automation platforms.
Analyze logs and telemetry to identify suspicious or malicious activity, assess impact, and determine the appropriate response.
Monitor, triage, and investigate security alerts from SIEM, EDR, cloud, identity, email, and network-security platforms.
Build and enhance SOAR playbooks to automate alert enrichment, investigation, case management, notifications, and approved containment actions.
Validate SIEM data coverage, log quality, parsing, ingestion health, and retention across security-relevant systems.
Collaborate with IT, cloud, infrastructure, identity, network, and engineering teams to contain incidents and drive remediation.
Create and maintain incident-response runbooks, investigation guides, detection documentation, and automation procedures.
Translate investigation findings and post-incident lessons learned into improved detections, automation workflows, and security controls.
All you need is:
1-2 years of hands-on experience in Security Operations, SOC, Cyber Analysis, Incident Response, or Detection Engineering - Must.
Practical experience operating and maintaining SIEM platforms, including log onboarding, parsing, developing and tuning detection rules and alerting use cases - Must
Excellent written and verbal communication skills for documentation and reporting in English.
Experience analyzing security telemetry from different systems such as EDR, Windows and Linux systems, identity services, cloud environments, email-security tools, firewalls, DNS, proxy, VPN, and network devices.
Strong understanding of common attack techniques, the cyber kill chain, and the MITRE ATT&CK framework.
Nice to have:
Proficiency in SIEM query languages such as KQL or SQL.
Experience with scripting or automation using Python, PowerShell, Bash, REST APIs, JSON, or webhooks.
Familiarity with SOAR platforms and automation workflows for alert enrichment, investigation, case management, and response.
Skills Required
- 1–2 years of hands-on experience in Security Operations, SOC, Cyber Analysis, Incident Response, or Detection Engineering
- Practical experience operating and maintaining SIEM platforms, including log onboarding, parsing, detection-rule development and tuning, and alerting use cases
- Excellent written and verbal communication skills in English for documentation and reporting
- Experience analyzing security telemetry from EDR, Windows and Linux systems, identity services, cloud environments, email-security tools, firewalls, DNS, proxy, VPN, and network devices
- Strong understanding of common attack techniques, the cyber kill chain, and the MITRE ATT&CK framework
- Proficiency in SIEM query languages such as KQL or SQL
- Experience with scripting or automation using Python, PowerShell, Bash, REST APIs, JSON, or webhooks
- Familiarity with SOAR platforms and automation workflows for alert enrichment, investigation, case management, and response

What We Do
Mobileye is leading the mobility revolution with its autonomous-driving and driver-assistance technologies, harnessing world-renowned expertise in computer vision, machine learning, mapping, and data analysis. Founded in 1999, Mobileye has pioneered such groundbreaking technologies as REM™ crowdsourced mapping, True Redundancy™ sensing, and the RSS™ safety model. These technologies are driving the ADAS and AV fields towards the future of mobility – enabling self-driving vehicles and mobility solutions, powering industry-leading advanced driver-assistance systems and delivering valuable intelligence to optimize mobility infrastructure. Mobileye technology is used in over 170 million vehicles worldwide. In 2022, Mobileye became an independent company while still being majority-owned by Intel. Mobileye’s headquarters and R&D center are based in Jerusalem, with additional offices across Israel and around the world.
Why Work With Us
Our technology enables self-driving vehicles and mobility solutions, powers industry-leading advanced driver assistance systems, and delivers valuable intelligence to optimize mobility infrastructure.
Gallery