


Opportunity Overview
We’re looking for an experienced Lead Governance, Risk and Compliance (GRC) Manager to lead and mature our enterprise security governance, risk management, regulatory compliance, and customer assurance programs. In this role, you will drive operational excellence across compliance frameworks, security risk management, third-party assurance, and customer-facing security initiatives while strengthening the processes and technology that support our growing business.
This is a hands-on leadership role suited for an experienced GRC professional who can independently manage complex initiatives, influence cross-functional stakeholders, and build scalable, repeatable operations. You’ll work closely with Security, Engineering, IT, Legal, Sales, Customer Success, and executive leadership to advance our security posture, accelerate customer trust, and enable business growth.
What you’ll do:
- Lead and mature Cohere’s GRC program, establishing scalable governance processes, operating procedures, risk management practices, and measurable performance indicators aligned with business objectives.
- Own the deployment, configuration, and optimization of enterprise GRC platforms, including control mapping, evidence automation, risk registers, continuous monitoring, and compliance reporting.
- Direct compliance and certification initiatives across HITRUST, HIPAA, ISO 27001, and applicable regulatory requirements, ensuring ongoing audit readiness and effective control execution.
- Lead customer security assurance activities, including security questionnaires, due diligence requests, customer audits, executive briefings, and security discussions with prospective and existing clients.
- Partner with Sales, Customer Success, and Marketing to develop security-focused go-to-market materials, establish and maintain a customer-facing Trust Center, and strengthen security as a competitive differentiator.
- Review and negotiate security-related contractual requirements in partnership with Legal, including Data Protection Agreements (DPAs), Business Associate Agreements (BAAs), security exhibits, and customer security obligations.
- Oversee enterprise risk management activities, including risk assessments, remediation tracking, exception management, and the enforcement and reporting of vulnerability remediation SLAs across Engineering, Platform, DevOps, and Data teams.
- Govern identity and access compliance, including periodic access reviews, privileged access certifications, segregation of duties, and remediation of access control deficiencies.
- Establish and maintain cross-functional GRC engagement with business units to align security policies, controls, risk ownership, and compliance obligations with operational priorities.
- Develop and deliver executive-level presentations, dashboards, and reporting that communicate compliance posture, risk exposure, remediation performance, customer assurance metrics, and program maturity.
- Build and scale a high-performing GRC function, establishing repeatable processes, developing team capabilities, managing external assessors and partners, and driving continuous improvement with minimal day-to-day oversight.
- 8+ years of progressive experience in information security, governance, risk management, compliance, or IT audit, including 2+ years leading GRC initiatives, programs, and/or teams.
- Professional certifications such as CISM, CISSP, CRISC, CISA, CGRC, or HITRUST CCSFP.
- Deep working knowledge of HITRUST, ISO 27001, and HIPAA including direct experience managing assessments, implementing controls, coordinating audits, and maintaining certification readiness.
- Demonstrated experience deploying and administering enterprise GRC platforms, including implementation, workflow design, control mapping, evidence collection, reporting, and process automation.
- Familiarity with the NIST Cybersecurity Framework, NIST AI Risk Management Framework, ISO 27017, ISO 27018, ISO 42001, and privacy-related security requirements.
- Deep understanding of enterprise risk management, including risk registers, control assessments, risk treatment plans, vulnerability remediation SLAs, and formal exception management.
- Demonstrated project and program management capabilities, including managing concurrent initiatives, developing operational roadmaps, establishing KPIs, and delivering results independently.
- Proven experience leading customer assurance programs, including security questionnaires, customer-facing security meetings, due diligence reviews, and responding to enterprise customer requirements.
- Experience with GRC platforms such as Vanta, Anecdotes, ZenGRC, Drata, ServiceNow GRC, or similar enterprise solutions.
- Demonstrated success developing GRC program maturity models, executive scorecards, and risk-based reporting frameworks.
- Excellent written and verbal communication, executive presentation, and analytical reporting skills, with the ability to translate complex security and compliance requirements into actionable business insights.
- Working knowledge of contractual security requirements, including reviewing and redlining security exhibits, DPAs, BAAs, and customer agreements in collaboration with Legal.
- Demonstrated ability to partner with Sales, Customer Success, and business stakeholders to develop customer assurance materials, security documentation, and go-to-market enablement resources.
- Experience designing, launching, or administering a customer-facing Security Trust Center and associated assurance workflows.
- Background in healthcare technology, SaaS, AI/ML-driven organizations, or other highly regulated environments.
Pay & Perks:
💻 Fully remote opportunity with about 5% travel
🩺 Medical, dental, vision, life, disability insurance, and Employee Assistance Program
📈 401K retirement plan with company match; flexible spending and health savings account
🏝️ Flex Time Off + company holidays
👶 Up to 14 weeks of paid parental leave
🐶 Pet insurance
The salary range for this position is $133,000 to $145,000 annually; as part of a total benefits package which includes health insurance, 401k and bonus. In accordance with state applicable laws, Cohere is required to provide a reasonable estimate of the compensation range for this role. Individual pay decisions are ultimately based on a number of factors, including but not limited to qualifications for the role, experience level, skillset, and internal alignment.
Interview Process*:
- Connect with Talent Acquisition for a Preliminary Phone Screening
- Meet your Hiring Manager!
- Case Study
- Cross functional interview
*Subject to change
About Cohere Health:
Cohere Health’s clinical intelligence platform and agentic AI-powered solutions connect health plans’ strategic goals and providers’ needs, optimizing the speed, cost, and quality of care. With an enterprise approach that streamlines payer-provider decision-making across the care continuum–including policy, prior authorization, payment accuracy, and more–the company improves collaboration and reduces burden, resulting in up to 8x ROI and 94% provider satisfaction.
With the acquisition of ZignaAI, we’ve further enhanced our platform by launching our Payment Integrity Suite, anchored by Cohere Validate™, an AI-driven clinical and coding validation solution that operates in near real-time. By unifying pre-service authorization data with post-service claims validation, we’re creating a transparent healthcare ecosystem that reduces waste, improves payer-provider collaboration and patient outcomes, and ensures providers are paid promptly and accurately.
Cohere Health’s innovations continue to receive industry wide recognition. We’ve been named to the 2025 Inc. 5000 list and in the Gartner® Hype Cycle™ for U.S. Healthcare Payers (2022-2025), and ranked as a Top 5 LinkedIn™ Startup for 2023 & 2024. Backed by leading investors such as Deerfield Management, Define Ventures, Flare Capital Partners, Longitude Capital, and Polaris Partners.
The Coherenauts, as we call ourselves, who succeed here are empathetic teammates who are candid, kind, caring, and embody our core values and principles. We believe that diverse, inclusive teams make the most impactful work. Cohere is deeply invested in ensuring that we have a supportive, growth-oriented environment that works for everyone.
We can’t wait to learn more about you and meet you at Cohere Health!
Equal Opportunity Statement:
Cohere Health is an Equal Opportunity Employer. We are committed to fostering an environment of mutual respect where equal employment opportunities are available to all. To us, it’s personal.
Skills Required
- 8+ years of progressive experience in information security, governance, risk management, compliance, or IT audit
- 2+ years leading GRC initiatives, programs, or teams
- Professional certification such as CISM, CISSP, CRISC, CISA, CGRC, or HITRUST CCSFP
- Direct experience managing HITRUST, ISO 27001, and HIPAA assessments, controls, audits, and certification readiness
- Experience deploying and administering enterprise GRC platforms, including workflow design, control mapping, evidence collection, reporting, and automation
- Familiarity with NIST Cybersecurity Framework, NIST AI Risk Management Framework, ISO 27017, ISO 27018, ISO 42001, and privacy-related security requirements
- Strong understanding of enterprise risk management, risk registers, control assessments, risk treatment plans, vulnerability remediation SLAs, and exception management
- Project and program management experience, including concurrent initiatives, roadmaps, KPIs, and independent delivery
- Experience leading customer assurance programs, security questionnaires, customer security meetings, due diligence reviews, and enterprise customer requirements
- Experience with GRC platforms such as Vanta, Anecdotes, ZenGRC, Drata, ServiceNow GRC, or similar
- Experience developing GRC maturity models, executive scorecards, and risk-based reporting frameworks
- Excellent written and verbal communication, executive presentation, and analytical reporting skills
- Working knowledge of contractual security requirements, including security exhibits, DPAs, BAAs, and customer agreements
- Experience partnering with Sales, Customer Success, and business stakeholders on customer assurance and security enablement materials
- Experience designing, launching, or administering a customer-facing Security Trust Center
- Background in healthcare technology, SaaS, AI/ML-driven organizations, or other highly regulated environments
What the Team is Saying


Cohere Health Compensation & Benefits Highlights
-
Leave & Time Off Breadth — Leave policies include up to 184 hours (23 days) of PTO annually plus 10 company holidays, with additional recharge days also noted. This breadth of time off is consistently highlighted as a standout element of the package.
-
Parental & Family Support — Paid parental leave is advertised at up to 14 weeks, offering substantial support for growing families. This level of leave is positioned as a meaningful advantage relative to many employers.
-
Healthcare Strength — Medical, dental, vision, life and disability coverage are provided alongside HSA/FSA options and EAP resources. Multiple plan options and first‑day eligibility mentions indicate broad healthcare support.
Cohere Health Insights

What We Do
Cohere Health’s clinical intelligence platform and agentic AI-powered solutions connect health plans’ strategic goals and providers’ needs, optimizing the speed, cost, and quality of care. With an enterprise approach that streamlines payer-provider decision-making across the care continuum–including policy, prior authorization, payment accuracy, and more–the company improves collaboration and reduces burden, resulting in up to 8x ROI and 94% provider satisfaction. With the acquisition of ZignaAI, we expanded our AI-native platform with a comprehensive Payment Integrity Suite that spans data mining, clinical and coding validation, authorization and claims reconciliation, and end-to-end payment integrity services across pre- and post-pay workflows. By connecting clinical and payment insights, our transparent, AI-powered solutions help health plans proactively improve payment accuracy, reduce waste and vendor dependency, strengthen provider relationships, and build smarter, more efficient payment integrity programs. Cohere Health’s innovations continue to receive industry-wide recognition. We’ve been recognized on TIME’s World Top HealthTech Companies 2025 list, the 2025 Inc. 5000 list, in the Gartner® Hype Cycle™ for U.S. Healthcare Payers (2022-2025), and ranked as a Top 5 LinkedIn™ Startup for 2023 & 2024.
Why Work With Us
Cohere Health brings together a community of healthcare and technology team members, passionate about changing the challenging parts of healthcare. If you enjoy solving challenging problems and learning about healthcare, then Cohere Health is a great career choice.
Gallery
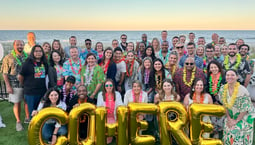
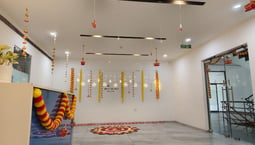
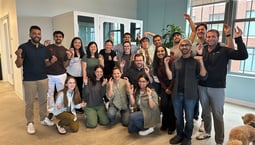

Cohere Health Offices
Remote Workspace
Employees work remotely.
Cohere Health employees work from all 50 states throughout the US - Cohere Health hosts retreats at our headquarters in Boston. Cohere Health employees based in Hyderabad, India, work in-office 5 days a week.
