

Maximum of 25 job preferences reached.
Top Cybersecurity Jobs
Security
Build and operate secure DevSecOps pipelines using SAST, DAST, container scanning, SBOM/SCA, artifact validation, and vulnerability gates. Produce RMF/cATO evidence, support secure coding compliance, drive CWE/CVE remediation, validate rollback readiness, and help developers adopt secure-by-default CI/CD automation across cloud and mission environments.
Top Skills:
CatoChecksum EnforcementCi/CdContainer RegistriesContainer SecurityCveCweDastFortifyGitlab Ci/CdGrypeImage SigningPoa&MRmfSastSbomScaSspTrivyZap
Security
Maintains cybersecurity compliance for DoD systems throughout the RMF lifecycle. Responsibilities include managing POA&Ms, eMASS and DITPR-DON records, VRAM vulnerability data, FISMA documentation, security assessment reports, engineering change reviews, and compliance with DISA STIGs, NIST, NSA, and DoD policies. The analyst supports vulnerability remediation, system change assessments, and cybersecurity workforce certification requirements.
Top Skills:
AcasDadmsDisa StigsDitpr-DonEmassFismaNessusNistNsa Configuration GuidanceRmfVram
Security
Maintain Authority to Operate for Navy education systems, coordinate secure access, monitor vulnerabilities and incidents, manage compliance reporting, support audits, and integrate security into DevSecOps. The role includes incident investigation, threat analysis, remediation, cloud and enterprise security architecture, cybersecurity documentation, vendor coordination, risk management, and implementation of secure tools, applications, migrations, and deployment processes.
Top Skills:
ArmisCi/CdCloud SecurityCmrsCoamsDcsDevsecopsDockerEmassFirewallsIds/IpsKubernetesNice FrameworkNiprNist 800-53Ppsm RegistryQradarSIEMSiprSplunk
Agency
Manage complex, citywide cybersecurity programs and multiple concurrent projects across agencies, vendors, and stakeholders. Responsibilities include vendor selection, RFI/RFP development, budgeting, scheduling, contractor management, risk assessment, reporting, dashboard strategy, PMO development, workflow implementation, proof-of-concept trials, and executive communications. The role supports Cyber Command leadership and may require varied shifts in a 24/7 operational environment.
Top Skills:
Salesforce

Automotive • Big Data • Information Technology • Robotics • Software • Transportation • Manufacturing
Lead advanced cyber investigations and detection engineering across endpoint, network, cloud, identity, application, and manufacturing environments. Develop and tune detections in SIEM/EDR/NDR/SOAR, conduct threat hunting, apply MITRE ATT&CK, automate workflows with scripting/AI, mentor analysts, and collaborate across security teams to improve detection fidelity and response.
Top Skills:
AICloud-Native Security PlatformsEdrEdr PlatformsEndpoint SecurityIds/IpsMitre Att&CkNdrNetwork TelemetryPacket AnalysisPowershellPythonSecurity OrchestrationSIEMSoar

Healthtech • Insurance
Leads the Cyber & Information Security portfolio and program governance for a healthcare organization. Oversees prioritization, dependencies, risks, budgeting, execution, reporting, process optimization, and executive visibility across security initiatives. Supports CISO and Board engagements, coordinates governance materials and follow-up, participates in business continuity exercises, advises leadership on operational risks, and mentors team members. Requires substantial experience managing complex technology or security programs in regulated environments.
Top Skills:
Computer ScienceCybersecurityInformation Systems

Information Technology • Consulting • Cybersecurity
Lead pre-sales security architecture engagements by designing and validating defense-in-depth solutions across hybrid, cloud, application, identity, endpoint, network, and data environments. Conduct security assessments, create remediation roadmaps, integrate security platforms, and support DevSecOps, SOC, detection engineering, incident response, compliance, and risk programs. Collaborate with sales, engineering, clients, and executive stakeholders to communicate technical trade-offs and deliver scalable enterprise security strategies.
Top Skills:
AbnormalApi SecurityArctic WolfAWSAzureCasbCi/CdCiamCisCrowdstrikeCspmCybersecurityDarktraceDastDevsecopsDlpDmarcEdrEppIamIgaInfrastructure As CodeIsoKnowbe4KubernetesMdrMfaMicrosoft DefenderMicrosoft EntraMicrosoft SentinelNacNetskopeNgfwNistOktaPalo Alto NetworksPamProofpointQualysRapid7RaspRbacSaseSastScaSentineloneSIEMSoarSoc 2TenableThreat Intelligence PlatformsWafXdrZero TrustZscaler

Information Technology
Designs and implements cybersecurity controls, evaluates network, system, and application vulnerabilities, identifies advanced threats, and develops remediation strategies. The role involves monitoring and improving cyber defenses, responding to security breaches, communicating security risks to stakeholders, and supporting mission-critical infrastructure and national security initiatives.
Top Skills:
Big Data AnalyticsCybersecurityDod 8570.1MEvent CorrelationInfrastructure ControlsNetwork SecuritySecurity DevicesSecurity+Vulnerability Assessment
Information Technology • Consulting • Cybersecurity
Serve as a cybersecurity advisor to federal agency CIOs and CISOs. Translate cybersecurity policies, coordinate audits and federal mandates, improve enterprise security posture, develop security operating models, oversee ISSO security assessment and authorization activities, validate JCAM records, advise on system lifecycle requirements, perform risk assessments, and maintain security documentation. Requires strong communication, organizational skills, federal cybersecurity compliance expertise, hands-on JCAM experience, and an active Secret clearance.
Top Skills:
CaspCehCismCisspCybersecurityData ProtectionEndpoint ManagementFedrampFismaGrc Automation PlatformsInformation AssuranceIt Security AuditsJcamNist 800-53Poa&M RemediationRisk Management Framework (Rmf)Security Assessment And Authorization (Sa&A)SIEMVulnerability ManagementVulnerability Scanning
Artificial Intelligence • Cybersecurity
Lead the strategy, roadmap, and growth of Horizon3’s Tripwires threat detection and deception product. Own detection fidelity, deployment coverage, alerting, integrations, dashboards, analyst workflows, customer insight, and commercial outcomes. Partner with Engineering, Design, Sales, Marketing, Customer Success, and Security teams to deliver precise, low-noise alerts and integrate Tripwires with SOC response workflows. Define product metrics, influence executive direction, and guide launches and adoption.
Top Skills:
Active DirectoryAgileB2B SaasCybersecurityIncident Response WorkflowsNodezeroProduct AnalyticsScrumSecurity TelemetrySIEMSoarWebhooks

Fintech • Financial Services
Designs and delivers GM Financial’s cybersecurity architecture and program, including security controls, risk assessments, cloud and application security, network protections, compliance, and security strategy. Partners with technical and business stakeholders to reduce risks, assess systems, improve security maturity, guide infrastructure and application teams, and support cybersecurity education. The role also mentors team members and contributes to security automation, DevOps, container, and cloud security initiatives.
Top Skills:
Amazon Web Services (Aws)Application SecurityCi/CdCloud SecurityFirewallsGoGoogle Cloud Platform (Gcp)Identity And Access ManagementIdsInfrastructure As CodeKubernetesLanMicroservicesAzurePkiPythonRoutersRubySecurity As CodeVpnWan
Fintech • Financial Services
Executes cybersecurity governance and risk initiatives by developing policies, standards, and procedures; managing audits, remediation tracking, security requirements, and compliance reporting. Partners with business and technical teams to protect information assets, monitor adherence to controls, and address threats. The role requires knowledge of networking, infrastructure, security frameworks, IT service management, cloud technologies, and relevant regulations. It operates in a flexible hybrid environment with four office days weekly.
Top Skills:
AgileCloud TechnologiesDevOpsDnsHTTPIbm IseriesIbm PseriesIso 27001Microsoft CopilotMS OfficeNist 800-53Nist Cybersecurity FrameworkOsi ModelSshSslTcp/IpTmshTsmUmlVisioVlan
New
Cut your apply time in half.
Use ourAI Assistantto automatically fill your job applications.
Use For Free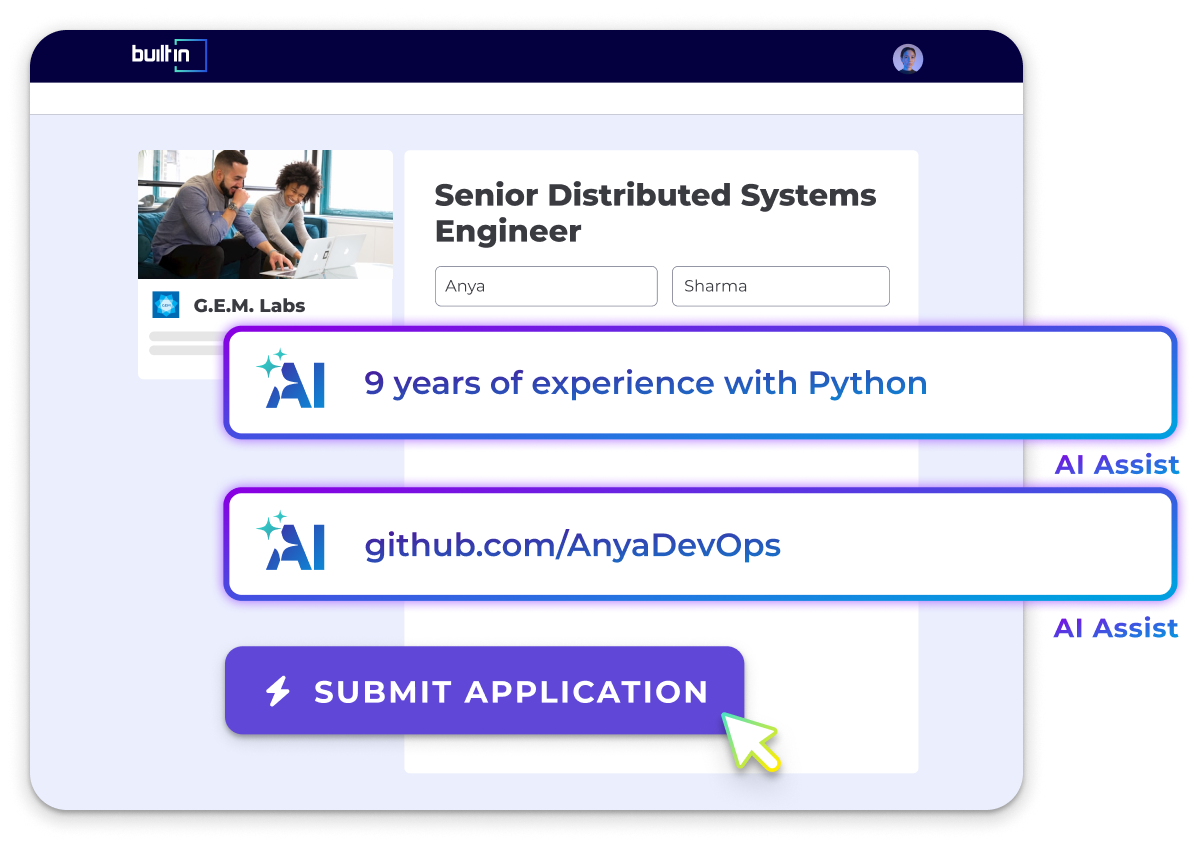
Aerospace • Professional Services • Defense
Provides cybersecurity engineering support to a NAVSEA contractor team. Responsibilities include implementing and monitoring cyber defense measures, assessing vulnerabilities, developing remediation strategies, maintaining security controls, responding to breaches, and ensuring compliance with cybersecurity policies and Assessment and Authorization requirements. The role is based primarily at the Washington Navy Yard, with occasional naval-centric travel to locations including Norfolk and San Diego.
Top Skills:
CybersecurityCybersecurity TestingEncryptionFirewallsInformation AssuranceRisk Management Framework (Rmf)
Automotive
Lead global IT audit for technology risk, develop risk-based audit plans, perform risk assessments and audits across software, infrastructure, and emerging technologies (AI, connected vehicles, SaaS). Partner with Cyber Defense, internal controls, and global audit teams to modernize audit practices, monitor remediation, and support transformation initiatives. Represent audit with senior technology leaders and drive benchmarking, industry research, and continuous improvement.
Top Skills:
AIApplication DevelopmentAspiceConnected VehicleContinuous MonitoringCybersecurityInfrastructure DesignIsoNistR155R156SaaSSoftware Engineering

Aerospace • Information Technology • Professional Services • Defense
Lead and oversee a large DoD enterprise IT and cybersecurity contract, interfacing with government leadership, managing staffing, subcontractors, risk, finances, compliance, SLAs, transitions, and delivery of cloud, infrastructure, DevSecOps, and security services across dispersed sites.
Top Skills:
AgileCloud EngineeringCybersecurityData ManagementDevsecopsEnterprise ArchitectureEnterprise InfrastructureItilNetwork EngineeringPmbok

Hardware • Software • Cybersecurity • Defense
Implement and assess cybersecurity controls across information systems and Microsoft Azure environments. Support DoD RMF activities, Zero Trust implementation, ACAS vulnerability scanning, remediation tracking, Azure Policy administration, Microsoft Defender for Cloud assessments, Xacta documentation, infrastructure automation, continuous monitoring, and security-control evidence collection. Collaborate with cloud engineers, system administrators, DevSecOps teams, ISSOs, and cybersecurity personnel while documenting configurations and remediation activities.
Top Skills:
AcasAzure PolicyDevsecopsInfrastructure As CodeAzureMicrosoft Defender For CloudRisk Management Framework (Rmf)XactaZero Trust

Aerospace
Supports ISSMs and ISSOs in securing DoD information systems across tactical Army programs. Implements cybersecurity policies, manages RMF documentation and ATO packages, reviews vulnerability and penetration-test findings, analyzes architectures and data flows, coordinates incident remediation, maintains security artifacts, and supports continuous monitoring, system hardening, secure application development, and DevSecOps practices.
Top Skills:
AcasAto PackagesDevsecopsDod RmfEmassHbssPenetration TestingSecure CodingStatic Code AnalysisSystem HardeningVulnerability ManagementVulnerability Scanning

Aerospace • Information Technology • Professional Services • Defense
Conduct cybersecurity assessments, residual risk analysis, and Risk Management Framework documentation for Department of War IT systems. Recommend secure architectures, administer mixed network environments, perform vulnerability testing, support military tactical and non-tactical systems, and contribute to cybersecurity reporting. The role is fully on-site and requires eligibility for a Secret security clearance.
Top Skills:
Assured Compliance Assessment Reports (Acas)CcnaCisspComptia Linux+Comptia Network+Comptia Security+Disa StigsEmassEmbedded Processor NetworkingMicrosoft Windows 10Real-Time Operating Systems (Rtos)Risk Management Framework (Rmf)RoutersSecurity Readiness Review (Srr) ScriptsSolarisUnix/LinuxVMwareWindows Server
Aerospace • Information Technology • Professional Services • Defense
Designs and maintains cybersecurity controls for Windows and Linux enterprise systems. Administers Trellix ePO, ACAS/Nessus, and Splunk; performs vulnerability and compliance assessments; supports RMF documentation, STIG/SCAP validation, monitoring, incident response, and remediation. The role collaborates with infrastructure teams, provides security recommendations, and develops technical procedures and assessment reports.
Top Skills:
AcasBashEdrFirewallsIds/IpsLinuxNessusNist RmfPowershellPythonScapSIEMSplunkStigsTrellix EpoWindows
Aerospace • Information Technology • Professional Services • Defense
Conduct vulnerability scans and security analyses on undersea combat platforms and support networks. Monitor SIEM data, detect and report cyber threats, analyze malicious activity, and develop and test mitigations. Apply cyber threat intelligence to address malware, phishing, and advanced persistent threats. Participation requires SkillBridge eligibility, military approval, U.S. citizenship, and an active Secret clearance.
Top Skills:
Advanced Persistent Threat (Apt) DetectionCyber Defense ToolsCyber Threat IntelligenceMalware AnalysisPhishing AnalysisSecurity Information And Event Management (Siem)Vulnerability Scanning
18 Days AgoSaved
Aerospace • Information Technology • Professional Services • Defense
Serve as the primary cybersecurity lead for classified information systems, managing RMF lifecycles, ATO authorization and renewals, security controls, compliance documentation, continuous monitoring, and coordination with DCSA, authorizing officials, system owners, engineers, administrators, and assessors. Support Cyber Operations by administering, testing, validating, and maintaining enterprise security systems and controls.
Top Skills:
Authorization To Operate (Ato)Dcsa Assessment And Authorization Process Manual (Daapm)Nist Risk Management Framework (Rmf)Nist Sp 800-53
Aerospace • Information Technology • Professional Services • Defense
Performs cybersecurity risk assessments, vulnerability analysis, remediation tracking, continuous monitoring, incident response support, and Splunk-based security event analysis. Develops dashboards, alerts, reports, documentation, and training while supporting ACAS scans, STIG compliance, threat detection, and classified-system requirements analysis. Collaborates with system administrators, network engineers, application owners, and cybersecurity teams to strengthen security operations and resolve vulnerabilities.
Top Skills:
AcasAWSAzureMicrosoft DefenderNessusQualysSIEMSplunkStigSyslogTrellix

Artificial Intelligence • Robotics • Software • Analytics
Supports DoD Assessment and Authorization processes under the Risk Management Framework. Validates cybersecurity controls, advises system owners and J683, manages authorizations, prepares and updates Security Authorization Packages, maintains authorization artifacts and databases, and reports deliverables. Requires expertise across all RMF A&A phases, eMASS and related toolsets, DoD cybersecurity controls, contract financial management, and IAM-III certification. The role is office-based, requires U.S. citizenship and TS/SCI clearance, and involves no travel.
Top Skills:
Dodi 8510.01EmassExcelMicrosoft OutlookMicrosoft PowerpointMicrosoft ProjectMicrosoft VisioMicrosoft WordRisk Management Framework (Rmf)

Information Technology • Security • Cybersecurity
Monitor network traffic, IDS alerts, security events, and logs to identify threats and false positives. Develop SOC procedures, produce situation reports, investigate incidents, create SIEM and IDS detection content, recommend proactive security blocks, and advise incident responders. The role requires shift work, multitasking under pressure, incident response experience, a bachelor’s degree, a relevant cybersecurity certification, and eligibility for a government clearance.
Top Skills:
Intrusion Detection Systems (Ids)SIEM

Information Technology • Professional Services • Cybersecurity
Monitor network traffic, IDS, SIEM events, and security logs; distinguish real threats from false alarms; investigate incidents; create detection content; maintain SOC procedures; advise incident responders; produce situation reports and security communications; and track investigations to resolution while working shifts.
Top Skills:
Intrusion Detection Systems (Ids)Security Information And Event Management (Siem)

Let Your Resume Do The Work
Upload your resume to be matched with jobs you're a great fit for.
Success! We'll use this to further personalize your experience.
Top Companies Hiring Cybersecurity Roles
See All





Popular Job Searches
All Filters
Total selected ()
No Results
No Results
