

Snap Inc is a technology company. We believe the camera presents the greatest opportunity to improve the way people live and communicate. Snap contributes to human progress by empowering people to express themselves, live in the moment, learn about the world, and have fun together.
The Company operates Snapchat, a visual messaging app that enhances your relationships with friends, family, and the world, and Specs Inc., a wholly-owned subsidiary dedicated to making computing more human, in addition to Bitmoji, Saturn, and other digital services.
Snap Engineering teams build fun and technically sophisticated products that reach hundreds of millions of Snapchatters around the world, every day. We’re deeply committed to the well-being of everyone in our global community, which is why our values are at the root of everything we do. We move fast, with precision, and always execute with privacy at the forefront.
We’re looking for a Security Technical Program Manager, Risk & Compliance to join Snap’s Security Governance, Risk & Compliance (GRC) team. In this role, you will design and build the continuous controls monitoring (CCM) capability that gives Snap real-time visibility into the health of its security and compliance controls. Your scope covers IT General Controls (ITGCs) and controls supporting SOX, CCPA, NIS2, ISO 27001, ISO 42001, SOC 2, PCI DSS, and related laws and regulations. You will set the technical standard for how controls are designed, built into our systems, monitored, and evidenced. You will partner closely with Engineering, Internal Audit, Legal, Privacy, and Finance so that compliance is something we can measure continuously, not a once-a-year exercise.
What you’ll do:
- Architect, build, and own Snap’s continuous controls monitoring program, including automated control testing, evidence collection, and dashboards that show control health across all in-scope frameworks.
- Define clear, testable control requirements and acceptance criteria across the ITGC domains of access management, change management, IT operations, and system development, as well as framework-specific controls for privacy, payments, and operational resilience.
- Partner with engineering teams early in the design of new or re-platformed systems so that capabilities like audit logging, segregation of duties, change approval, and evidence retention are built in before launch rather than added later.
- Review significant infrastructure, platform, and AI/agent framework changes for compliance and risk mitigation impact while designs are still flexible, and keep an up-to-date view of how changes affect control scope, key control populations, and evidence needs.
- Build and maintain our GRC platform that supports a unified common controls framework and maps requirements across SOX, CCPA, NIS2, ISO 27001, ISO 42001, SOC 2, and PCI DSS, so each control is designed once, tested once, and reused across frameworks.
- Design services, integrations, and agentic automations, that pull control evidence directly from source systems such as cloud platforms, identity providers, CI/CD tooling, ticketing systems, and infrastructure-as-code, and that validate the completeness and accuracy of control populations.
- Identify, track, and root-cause control gaps surfaced through monitoring, internal reviews, or audits. Work with control owners and partner engineering teams on durable, engineering-driven fixes, and confirm that remediation actually resolves the issue before re-testing.
- Act as a second-line partner, advising and challenging control owners without taking ownership of their controls, and maintaining a clear boundary between GRC monitoring and Internal Audit’s independent testing.
- Significantly increase automated evidence coverage, reduce manual audit preparation effort, and shorten the time from control failure to detection.
- Apply AI and LLM tools to accelerate control testing, evidence review, and compliance analysis, with sound judgment about where automation is reliable and where human review is still required.
Knowledge, skills, & abilities:
- Deep understanding of risk and compliance including common control frameworks and how auditors scope, test, and evaluate technology controls and deficiencies.
- Broad familiarity with privacy, security, and resilience frameworks including CCPA/CPRA, NIS2, ISO 27001, ISO 42001, SOC 2, and PCI DSS v4.0, and an understanding of where their requirements overlap and differ.
- Strong engineering fluency: comfortable reading and writing code, reviewing infrastructure-as-code, tracing a CI/CD pipeline end to end, and challenging a system design on its technical merits.
- Ability to translate regulatory and framework language into concrete requirements engineers can build against, and to translate engineering reality back into assurance language that auditors, regulators, and leadership can rely on.
- A strong preference for solving control gaps through system design and automation rather than manual procedures and workarounds.
- Comfort making sound decisions with incomplete information and adjusting priorities as scope and business needs evolve.
- Exceptional verbal and written communication skills, with the ability to tailor the message to engineers, executives, and auditors alike.
- Proven ability to influence cross-functional stakeholders across Engineering, Finance, Legal, Privacy, and Internal Audit without direct authority.
Minimum qualifications:
- Bachelor’s degree in computer science, information systems, or a related technical field, or equivalent experience
- 6+ years of experience in engineering, GRC engineering, IT audit, or technical controls assurance
- Hands-on experience leading or serving as a senior contributor on a risk, compliance, or ITGC program at a public company or a company preparing for regulatory compliance readiness
- Programming proficiency in Python or at least one systems language such as Java, Go, Rust, or C/C++
- Working experience with cloud infrastructure (GCP and/or AWS), developer platforms, release engineering, or financial systems control environments
Preferred Qualifications:
- Experience designing and launching a continuous controls monitoring or automated evidence collection program from the ground up
- A mix of IT audit or advisory experience (Big 4 or equivalent) and in-house experience at a large-scale technology company
- Experience defining or assessing controls over internally built systems, payment processing, billing, or revenue pipelines
- Experience defining or assessing controls for AI/ML systems or automated agents operating in production
- Experience building or maintaining a common controls framework that spans multiple regulatory and industry standards
- Familiarity with SOC 1, SOC 2, and/or ISO 27001 reliance, service organization control mapping, and complementary user entity controls
- Experience with NIST CSF 2.0, NIST AI Risk Management Framework
- CISSP, CISA, CISM, CCSP, CPA, or similar certifications a plus
"Default Together" Policy at Snap: At Snap Inc. we believe that being together in person helps us build our culture faster, reinforce our values, and serve our community, customers and partners better through dynamic collaboration. To reflect this, we practice a “default together” approach and expect our team members to work in an office 4+ days per week.
At Snap, we believe that having a team of diverse backgrounds and voices working together will enable us to create innovative products that improve the way people live and communicate. Snap is proud to be an equal opportunity employer, and committed to providing employment opportunities regardless of race, religious creed, color, national origin, ancestry, physical disability, mental disability, medical condition, genetic information, marital status, sex, gender, gender identity, gender expression, pregnancy, childbirth and breastfeeding, age, sexual orientation, military or veteran status, or any other protected classification, in accordance with applicable federal, state, and local laws. EOE, including disability/vets.
We are an Equal Opportunity Employer and will consider qualified applicants with criminal histories in a manner consistent with applicable law (by example, the requirements of the San Francisco Fair Chance Ordinance and the Los Angeles Fair Chance Initiative for Hiring, where applicable).
Our Benefits: Snap Inc. is its own community, so we’ve got your back! We do our best to make sure you and your loved ones have everything you need to be happy and healthy, on your own terms. Our benefits are built around your needs and include paid parental leave, comprehensive medical coverage, emotional and mental health support programs, and compensation packages that let you share in Snap’s long-term success!
Compensation
In the United States, work locations are assigned a pay zone which determines the salary range for the position. The successful candidate’s starting pay will be determined based on job-related skills, experience, qualifications, work location, and market conditions. The starting pay may be negotiable within the salary range for the position. These pay zones may be modified in the future.
Zone A (CA, WA, NYC):
The base salary range for this position is $190,000-$284,000 annually.
Zone B:
The base salary range for this position is $181,000-$270,000 annually.Zone C:
The base salary range for this position is $162,000-$241,000 annually.This position is eligible for equity in the form of RSUs.If you believe this job description is missing required pay transparency information, please submit a report through this form: Job Description Pay Range Disclosure.
Skills Required
- Bachelor's degree in computer science, a related technical field, or equivalent experience
- 6+ years of experience in security advisory, technical program management, or security solution delivery
- Deep security experience and familiarity with broad information security concepts and principles
- Proven experience running critical programs within a security field
- Experience working with engineers and driving large security projects with proven impact
- Exceptional verbal and written communication skills, including tailoring messages to different audiences
- Experience influencing cross-functional teams and stakeholders to drive security programs
- Experience with NIST CSF 2.0, NIS2, or ISO 27001
- CISSP, CISM, CCSP, or similar certification
What the Team is Saying



What We Do
We contribute to human progress by empowering people to express themselves, live in the moment, learn about the world, and have fun together.
Gallery

Snap Inc. Teams

Snap Inc. Offices
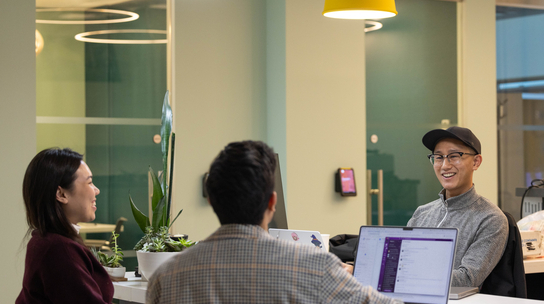
Hybrid Workspace
Employees engage in a combination of remote and on-site work.
Our “default together” approach is an 80/20 model where we are asking team members to spend 80% of the time, on average, in the office, with the remaining 20% of the time spent remote.
