

What We Do:
Cybercrime is growing, and more businesses are getting hit by threats that used to target only the biggest organizations. That pushes defenders like us to operate at the highest level, and it deepens our need for good people who want to make a meaningful impact.
Founded in 2015 by former NSA cyber operators, Huntress is a remote-first team working to make enterprise-grade cybersecurity accessible to businesses of all sizes. We work closely with security teams and service providers protecting complex environments, often without the time or headcount to handle it all. That’s why we build our technology in-house and back it with a 24/7 human-led Security Operations Center (SOC). As a result, our platform is never disconnected from the experts who manage it, ensuring our customers' protection.
Huntress now secures more than 6M endpoints and 16M identities worldwide. Those numbers keep growing because more businesses rely on us to help carry the load and operate with more confidence. Every day, you can see that commitment in how we stand with our customers and how we show up for each other.
Reports to: Senior Manager, Security Operations Center
Location: Remote Australia
Compensation Range: $110,000 to $140,000 AUD base plus bonus and equity
What You’ll Do:
You’re a hands-on SOC Analyst who thrives on detecting and responding to cybercrime. You’ll triage Active Hands-On Keyboard intrusions, track attackers through networks, and help remove them before they achieve their objectives. You’ll contextualise endpoint telemetry, analyse logs, leverage forensic artifacts, and understand malware to uncover the full scope of an intrusion.
You give a $ht about protecting customers and improving how the team operates, taking ownership of investigations and acting on the information available. You bring Warrior Spirit to complex incidents, staying resilient and composed under pressure. You are Outcome-Obsessed, measuring your work by the threats contained, customers protected, and actionable remediation delivered. Alongside alert triage and intrusion response, you’ll support sales, collaborate with Product to shape Huntress’ MDR service and platform, and have opportunities to contribute across Incident Response, Security Operations, Threat Hunting, and Detection Engineering. We’ll also support you in sharing your work through blogs, conference talks, webinars, and research publications that build your personal brand and the broader security community.
This role follows Perth time (AWST), Monday to Friday, 8:00 am to 4:00 pm. Applicants based elsewhere in Australia are welcome, provided you are able to work these hours converted to your local time.
Responsibilities:
- Triage, investigate, respond to, and remediate alerts generated by the Huntress platform.
- Review EDR/SIEM telemetry, log sources, and forensic artifacts to determine the root cause of attacks where possible and provide the remediation needed to remove the threat.
- Perform dynamic analysis of malware when required to extract indicators of compromise or determine a file’s malicious intent.
- Contribute to and refine detection capabilities and queue hygiene through crafting and tuning signals to address emerging threats.
- Investigate activity in Microsoft 365 and Google Workspace and deliver actionable remediation advice for compromised tenants.
- Continue to grow your skills and knowledge through real-world intrusion data, paid training opportunities, and responsible use of AI tools to support research, summarise findings, and accelerate routine analysis while validating outputs.
- Support customer success by assisting our SOC Support team with customer/partner escalations related to threat-related and SOC-relevant questions.
- Help through partnering with Product and Engineering Teams to continue to evolve Human Led Agentic workflows
What You Bring To The Team:
- You have 2+ years of experience in SOC, Incident Response, Managed Detection and Response, or Digital Forensics roles.
- You have demonstrated experience with at least one of Windows, Linux, or macOS, including attack surfaces, malware analysis, and basic threat actor tools and techniques.
- You understand common system administration skills and how threat actors abuse them to achieve their goals, including Active Directory, PowerShell, Group Policy, and local account creation.
- You are familiar with the techniques and tactics in MITRE ATT&CK, including credential dumping, lateral movement, persistence mechanisms, and exfiltration techniques.
- You have a working knowledge of core networking concepts, including common ports and protocols, NAT, public and private IP addresses, and VLANs.
- You have a passion for forensics and enjoy digging into logs, processes, and artifacts to understand intrusions and outmaneuver attackers.
- You communicate clearly in writing and verbally, simplify complex technical findings for diverse audiences, and demonstrate self-guided learning that keeps your skills current.
- You use AI to work faster and smarter in day-to-day security analysis, applying sound judgment and validating its output before acting on it.
- You enjoy working with a fun, supportive team, bring a genuine team-player mindset, and help deliver great outcomes with a smile, a laugh, and a dash of witty (but accurate) memes.
- A desire to hold your manager accountable for delivering ice cream at the Australian Security Offsite.
What We Offer:
- Fully remote work
- At least one annual trip to the US for Summer Summit, with additional local events in Australia!
- New starter home office set up reimbursement ($800 AUD)
- 12 weeks paid parental leave for both primary and secondary carers
- Monthly digital allowance for personal phone and internet costs ($185 AUD)
- Monthly home office tech stipend to upgrade or replace equipment ($40 AUD)
- Subsidised private health insurance through our preferred provider
- Stock options for all full-time employees
- Access to the BetterUp platform for coaching, personal, and professional growth
Huntress is committed to creating a culture of inclusivity where every single member of our team is valued, has a voice, and is empowered to come to work every day just as they are.
We do not discriminate based on race, ethnicity, color, ancestry, national origin, religion, sex, sexual orientation, gender identity, disability, veteran status, genetic information, marital status, or any other legally protected status.
We do discriminate against hackers who try to exploit businesses of all sizes.
Accommodations:
If you require reasonable accommodation to complete this application, interview, or pre-employment testing or participate in the employee selection process, please direct your inquiries to [email protected]. Please note that non-accommodation requests to this inbox will not receive a response.
Huntress uses artificial intelligence tools to assist in reviewing and evaluating job applications, including resume screening, skills assessment, and candidate matching and comparisons. These AI tools support our human recruiters in the initial review process, but do not make final hiring decisions without human involvement. By submitting your application, you acknowledge this use of AI in our recruitment process. Please review our Candidate Privacy Notice for more details on our practices and your data privacy rights.
#BI-Remote
Skills Required
- 2+ years of experience in SOC, Incident Response, Managed Detection and Response, or Digital Forensics roles
- Experience with at least one of Windows, Linux, or macOS, including attack surfaces, malware analysis, and threat actor tools and techniques
- Understanding of system administration and how threat actors abuse Active Directory, PowerShell, Group Policy, and local account creation
- Working knowledge of MITRE ATT&CK techniques and tactics, including credential dumping, lateral movement, persistence, and exfiltration
- Working knowledge of networking concepts, including ports, protocols, NAT, public and private IP addresses, and VLANs
- Passion for digital forensics and analyzing logs, processes, and artifacts
- Clear written and verbal communication skills, including the ability to explain complex technical findings
- Ability to use AI tools responsibly for security analysis and validate their outputs
- Ability to work Monday through Friday, 8:00 am to 4:00 pm Perth time
Huntress Compensation & Benefits Highlights
-
Retirement Support — A 5% employer retirement contribution is highlighted, often provided even when employees do not contribute. Feedback suggests this consistent, employer-funded support is a standout element, with regional pension equivalents offered internationally.
-
Healthcare Strength — Coverage spans medical, dental, vision, life, and disability insurance, with some programs available from the hire date in certain locations. Feedback suggests the breadth of coverage is a core part of the package.
-
Parental & Family Support — New parents are offered 12 weeks of paid parental leave. Feedback suggests this sits alongside additional time-off categories such as sick leave, bereavement leave, and floating holidays.
Huntress Insights

What We Do
Founded in 2015 by former NSA cyber operators, Huntress protects all businesses—not just the 1%—with enterprise-grade, fully owned and managed cybersecurity products at the price of an affordable SaaS application. The Huntress difference is our One Team advantage: our technology is designed with our industry-defining Security Operations Center (SOC) in mind and is never separated from our service. We protect 4M+ endpoints and 7M+ identities worldwide, elevating underresourced IT teams with protection that works as hard as they do. As long as hackers keep hacking, Huntress keeps hunting.
Why Work With Us
Huntress is a fully remote, global team of passionate experts and ethical badasses on a mission to break down the barriers to cybersecurity. Whether creating purpose-built security solutions, hunting down hackers, or impacting our community, our people go above and beyond to change the security game and make a real difference.
Gallery




Huntress Teams
Huntress Offices
Remote Workspace
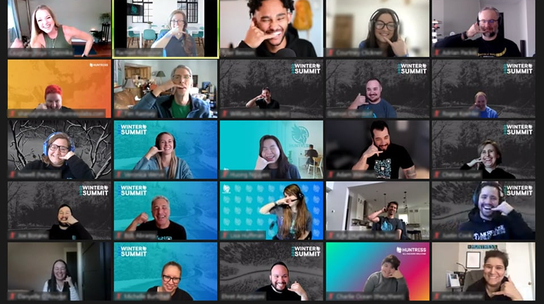
Employees work remotely.
We believe in hiring the best people regardless of location or time zone. We currently hire individuals in the US, Canada, the UK, Ireland, and Australia.
