Responsibilities
- Lead the region's security incident response, providing technical leadership during critical (Severity 0/1) incidents by driving complex investigations, cross-team coordination, and resolution.
- Manage all incident-related communications, providing clear status updates to executives, management, and key stakeholders such as Legal, Privacy, and Communications.
- Serve as the primary liaison with external bodies, including law enforcement, CERTs, and ISACs, during and after incidents.
- Coach and mentor team members in their day-to-day incident response activities.
- Own and deliver projects to advance the team's incident response capabilities, including building new tools, systems, and programs that uplift Atlassian's overall security posture.
- Enhance team readiness by creating and running regular training exercises and incident response drills.
- Conduct comprehensive post-incident reviews to identify root causes and drive improvements to the incident response process.
- Collaborate with other security teams to develop long-term strategies and plans to prevent future incidents.
- Produce and disseminate threat intelligence specific to Atlassian's products and infrastructure.
- Stay current with the latest security trends, threats, and technologies to ensure the team remains prepared for emerging risks.
At Atlassian, we strive to design equitable, explainable, and competitive compensation programs. We follow consistent hiring practices and account for each candidate's skills, knowledge, and experience when setting base pay within the range.
This role may also be eligible for benefits, bonuses, commissions, and equity.
Qualifications
- Bachelor's degree in Computer Science, Information Security, or a related field.
- At least 5 years of experience in security incident response, including leading high-severity incidents for enterprises and coordinating response efforts across multiple teams.
- Specialization in two or more of the following areas: Malware Analysis, Forensics, Threat Hunting, Network Analysis, or Cloud Endpoint Analysis.
- Strong technical foundation in security technologies (e.g., firewalls, IDS), cloud platforms (GCP), and network protocols.
- Experience building and maintaining security tools using a scripting or programming language (e.g., Python, Go).
- Expertise in creating and maintaining incident response playbooks.
- Excellent written and oral communication skills, with strong analytical abilities and the capacity to work effectively under high pressure.
More about the team
We value diverse skill sets and motivated individuals so that we can learn from one another and engage in interesting projects. We don't just click the same buttons over and over. You will be apart of the Security Detection and Response Organization-which includes Incident Response, Detection Engineering, Threat Intelligence, and Security Engineering-a group dedicated to improving Atlassian's security posture, products and engineering practices.
Benefits & Perks
Atlassian offers a wide range of perks and benefits designed to support you, your family and to help you engage with your local community. Our offerings include health and wellbeing resources, paid volunteer days, and so much more. To learn more, visit go.atlassian.com/perksandbenefits .
About Atlassian
At Atlassian, we're motivated by a common goal: to unleash the potential of every team. Our software products help teams all over the planet and our solutions are designed for all types of work. Team collaboration through our tools makes what may be impossible alone, possible together.
We believe that the unique contributions of all Atlassians create our success. To ensure that our products and culture continue to incorporate everyone's perspectives and experience, we never discriminate based on race, religion, national origin, gender identity or expression, sexual orientation, age, or marital, veteran, or disability status. All your information will be kept confidential according to EEO guidelines.
To provide you the best experience, we can support with accommodations or adjustments at any stage of the recruitment process. Simply inform our Recruitment team during your conversation with them.
To learn more about our culture and hiring process, visit go.atlassian.com/crh .
In line with local law, identity verification (which may include use of biometric data) is a condition of employment with Atlassian for employment fraud purposes.
Skills Required
- Bachelor's degree in Computer Science, Information Security, or a related field
- At least 5 years of security incident response experience
- Experience leading high-severity enterprise incidents and coordinating response across multiple teams
- Specialization in at least two of malware analysis, forensics, threat hunting, network analysis, or cloud endpoint analysis
- Strong technical foundation in security technologies such as firewalls and IDS
- Experience with cloud platforms, including GCP
- Strong knowledge of network protocols
- Experience building and maintaining security tools with a scripting or programming language such as Python or Go
- Expertise creating and maintaining incident response playbooks
- Excellent written and oral communication skills
- Strong analytical abilities and ability to work effectively under high pressure
What the Team is Saying



Atlassian Compensation & Benefits Highlights
-
Parental & Family Support — 26 weeks paid leave for birthing parents and 20 weeks for non‑birthing parents are offered, alongside inclusive family‑formation support such as fertility, adoption, and surrogacy. Additional resources include neurodiverse family support and conveniences like breastmilk shipping for business travel.
-
Healthcare Strength — Medical, dental, and vision coverage is paired with extensive mental‑health programs (e.g., Modern Health/EAP), plus disability and life insurance in many locations. Fertility and family‑formation benefits further expand the health offering.
-
Retirement Support — A 401(k) with a 4% company match and 100% immediate vesting is highlighted for U.S. employees. Retirement planning support is also included.
Atlassian Insights

What We Do
Atlassian creates teamwork solutions for high-performing teams. Our portfolio of collaboration and work management software products includes Jira, Confluence, Trello, Loom and Rovo. More than 300,000 businesses worldwide rely on Atlassian’s technology, including 80 percent of Fortune 500 companies. Our solutions support various business teams and they help organizations plan, track, and deliver their biggest ideas together.
Why Work With Us
At Atlassian, we believe we can accomplish so much more together than apart — which is why everything from our tooling — to our distributed workforce — to how our teams are structured is rooted in collaboration. Come join us and help unleash the potential of every team.
Gallery

Atlassian Teams
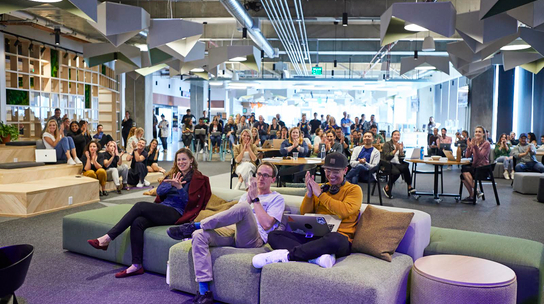
Atlassian Offices
Remote Workspace
Employees work remotely.
Atlassians have flexibility in where they work to support their family, personal goals, and other priorities. Our approach to distributed work allows us to tap into talent beyond our office locations, and to reimagine how work gets done.