


The key objectives of the TPRM Program are to:
- Assess the risk of third-party relationships which drive the rigor of risk management activities both during the third-party onboarding and ongoing monitoring lifecycle phases using the TPRM Program’s formula-based risk methodology;
- Act as a liaison across key internal stakeholder teams (Procurement, Legal, Enterprise Security and the Business) to ensure clear and accurate communication of third-party risks aligned to risk management activities in order to complete risk assessments in a timely manner;
- Identify TPRM program enhancements aimed at the effective and efficient management of third-party risk in order to support Business strategic initiatives.
Reporting to the TPRM Manager and working closely with the TPRM Risk Analyst, the Associate TPRM Risk Analyst will support day-to-day execution of the third-party risk lifecycle. This is a support-oriented analyst role focused on applying established TPRM procedures and risk methodology to standard engagements, maintaining complete and accurate assessment records, coordinating routine stakeholder activity, and escalating issues that require additional judgment.
Responsibilities:Risk Intake & Assessment Methodology
- Apply the TPRM Program’s formula-based inherent risk methodology and assign Criticality designations for standard third-party relationships, documenting the inputs, rationale, and supporting evidence
- Perform completeness and consistency checks on intake information, risk calculations, and assessment records; identify missing, inconsistent, or unclear information and escalate exceptions in accordance with defined thresholds.
Documentation Analysis & SME Coordination
- Gather, organize, and maintain third-party-provided information and documentation in accordance with TPRM assessment methodology and audit-readiness expectations.
- Identify and route required SME reviews using defined risk triggers, track responses, and document completed SME assessments and supporting evidence.
- Maintain accurate and timely records in Graphite Connect, Jira, and other approved systems of record.
Risk Review Support
- Support execution of third-party risk assessment remediation of identified gaps or findings based on defined risk triggers to obtain complete responses and supporting documentation.
- Support routine communication with third parties to resolve identified gaps, with primary responsibility for Medium-Risk and Low-Risk remediation activities.
- Track remediation actions, due dates, and supporting evidence; escalate High Risk, Critical, overdue, or otherwise judgment-intensive gaps.
- Support the third-party periodic review process, including leading communication to third parties to remediate identified gaps; escalate any gaps.
Status Reporting
- Compile assessment-level data, SME review status, remediation activity, and other required information to support standard status and portfolio reporting.
- Perform data-quality checks and identify field-level trends, recurring documentation gaps, or process issues for review.
- Prepare routine status updates and supporting materials for internal stakeholder discussions.
Experience & Education:
- 3-5 years of experience in Third-Party Risk Management (TPRM) or Governance, Risk & Compliance (GRC)
- Demonstrated experience performing substantive risk assessments and applying formula-based or quantitative risk methodologies
- Bachelor’s degree in a relevant field (Cybersecurity, Business, Information Systems).
Technical & Operational Proficiency:
- Proficiency with a TPRM platform, including the ability to interpret intake data, Data Level classifications, and inherent risk scoring logic.
- Operational understanding of standard control frameworks (NIST SP 800-53, ISO 27001, SOC 2, SIG Core/Lite, CAIQ).
- Working knowledge of regulatory requirements relevant to the third-party population (e.g., DORA, GDPR, NIS2, FedRAMP, PCI-DSS, OCC, CCPA).
Core Competencies:
- Attention to Detail: ability to gather and check third-party documentation accurately against TPRM methodology.
- Communication: clear, professional communication with third parties and internal stakeholders on lower-risk gaps.
- Reliability: ability to manage a defined queue of onboarding and periodic review tasks and escalate appropriately.
About MongoDB
MongoDB is built for change, empowering our customers and our people to innovate at the speed of the market. We have redefined the data platform for the AI era, enabling builders to create, transform, and disrupt industries with software. MongoDB’s unified data platform, the most widely available, globally distributed data platform on the market, helps organizations modernize legacy workloads, embrace innovation, and unleash AI. Our cloud-native platform, MongoDB Atlas, is the only globally distributed, multi-cloud data platform and is available across AWS, Google Cloud, and Microsoft Azure.
With offices worldwide and over 67,000 customers, including AI-native startups and approximately 75% of the Fortune 100, relying on MongoDB for their most important applications, we’re powering the next era of software.
Our compass at MongoDB is our Leadership Commitment, guiding how and why we make decisions, show up for each other, and win. It’s what makes us MongoDB.
To drive the personal growth and business impact of our employees, we’re committed to developing a supportive and enriching culture for everyone. From employee affinity groups, to fertility assistance and a generous parental leave policy, we value our employees’ wellbeing and want to support them along every step of their professional and personal journeys. Learn more about what it’s like to work at MongoDB, and help us make an impact on the world!
MongoDB is committed to providing any necessary accommodations for individuals with disabilities within our application and interview process. To request an accommodation due to a disability, please inform your recruiter.
MongoDB, Inc. provides equal employment opportunities to all employees and applicants for employment and prohibits discrimination and harassment of any type and makes all hiring decisions without regard to race, color, religion, age, sex, national origin, disability status, genetics, protected veteran status, sexual orientation, gender identity or expression, or any other characteristic protected by federal, state or local laws.
Req ID: 426443
MongoDB’s base salary range for this role is posted below. Compensation at the time of offer is unique to each candidate and based on a variety of factors such as skill set, experience, qualifications, and work location. Salary is one part of MongoDB’s total compensation and benefits package. Other benefits for eligible employees may include: equity, participation in the employee stock purchase program, flexible paid time off, 20 weeks fully-paid gender-neutral parental leave, fertility and adoption assistance, 401(k) plan, mental health counseling, access to transgender-inclusive health insurance coverage, and health benefits offerings. Please note, the base salary range listed below and the benefits in this paragraph are only applicable to U.S.-based candidates.
Skills Required
- 3-5 years of experience in Third-Party Risk Management or Governance, Risk & Compliance
- Experience performing substantive risk assessments
- Experience applying formula-based or quantitative risk methodologies
- Bachelor's degree in Cybersecurity, Business, Information Systems, or a relevant field
- Proficiency with a third-party risk management platform
- Ability to interpret intake data, data-level classifications, and inherent risk scoring logic
- Operational understanding of NIST SP 800-53, ISO 27001, SOC 2, SIG Core/Lite, and CAIQ
- Working knowledge of relevant regulatory requirements, including DORA, GDPR, NIS2, FedRAMP, PCI-DSS, OCC, and CCPA
- Strong attention to detail when reviewing third-party documentation
- Clear professional communication with third parties and internal stakeholders
- Ability to manage onboarding and periodic review tasks and escalate appropriately
What the Team is Saying


MongoDB Compensation & Benefits Highlights
-
Parental & Family Support — Parental leave is outlined at 20 weeks fully paid and gender‑neutral (with a one‑year tenure requirement), with return‑to‑work flexibility noted. Family‑building support includes 90% reimbursement up to $50,000 for fertility, adoption, or surrogacy, plus backup child/elder care services.
-
Healthcare Strength — Multiple medical plan options (Cigna and Kaiser HMO in CA) are offered, with low or no employee‑only payroll deductions on certain plans and preventive care covered at 100%. Separate dental (Cigna) and vision (EyeMed) benefits are also provided.
-
Wellbeing & Lifestyle Benefits — Mental‑health resources include Spring Health (up to 10 therapy video visits/year), Headspace for employees and dependents, an EAP, and a Mental Health First Aider program. Day‑to‑day perks and flexibility include flexible PTO, 11 U.S. holidays, and company‑paid in‑office lunches up to three days per week under the hybrid model.
MongoDB Insights

What We Do
The database market is big. How big? Well, according to IDC, it’ll reach $153 billion by 2027. And MongoDB is at the forefront of that innovation with thousands of customers across the globe. We empower developers and businesses to build and deploy the applications they want, wherever they want.
Why Work With Us
We are ambitious. We are passionate about creativity. And we believe the best paths are the ones we have yet to forge.
Gallery




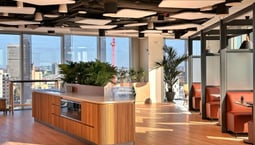


MongoDB Offices
Hybrid Workspace
Employees engage in a combination of remote and on-site work.
MongoDB provides multiple working model options for our employees, including the flexibility to work from home to opportunities for collaboration and social interaction in a MongoDB office.


