

Maximum of 25 job preferences reached.
Top Cybersecurity Jobs

Retail
Supports enterprise IT security operations by maintaining security applications and controls, managing risk and resilience, developing security procedures, contributing to threat operations and cybersecurity awareness, enforcing policies, and communicating technical security concepts to business and technology stakeholders.

10 Days AgoSaved
Professional Services • Consulting • Cybersecurity • Defense
Provides day-to-day IT and information assurance support for DoD Special Access Programs, including system administration, network and firewall maintenance, cybersecurity monitoring, authorization packages, vulnerability remediation, patching, account management, help desk support, VTC administration, COMSEC management, and compliance with DoD security policies.
Top Skills:
ComsecFile ServersFirewallsNetwork AppliancesSecurity Monitoring SystemsVtc Systems

Information Technology • Cybersecurity
Leads IT operations and serves as the company’s Microsoft and identity security authority. Owns Entra ID architecture, privileged access, lifecycle automation, SSO, endpoint platforms, SaaS integrations, compliance controls, audit readiness, and identity threat detection. Directs IT staff, manages projects and vendors, supports engineering environments, and automates provisioning and reporting using Graph, PowerShell, Power Automate, and Python. Partners across Security, Engineering, Marketing, and Web to remediate risks and deliver secure, auditable infrastructure.
Top Skills:
Auth0AWSAzureBashClaudeClaude CodeCloudflareConfluenceCursorDatto RmmGoogle WorkspaceJAMFJIRAJira Service ManagementKqlMcp ServersMicrosoft 365Microsoft DefenderMicrosoft Entra IdMicrosoft Entra Id P2Microsoft Graph ApiMicrosoft IntuneMicrosoft365DscOidcPower AutomatePowershellPythonSalesforceSAMLScimSftpSlackTerraformVpnZoom

Appliances • Industrial • Manufacturing
Supports IT governance, risk, and compliance activities, including security assessments, risk register maintenance, audit evidence collection, control testing, policy updates, and third-party risk reviews. The role coordinates with technical and non-technical stakeholders, monitors compliance activities, translates security information into reports, and helps maintain the organization’s cybersecurity posture and regulatory readiness.
Top Skills:
AWSAzureCis ControlsCobitDlpEdrGdprGCPGoogle SheetsHipaaIso/Iec 27001ExcelNist CsfSecSIEMSoxVulnerability Management
Fintech
Performs second-line IT and data risk management, including risk assessments, control testing, gap assessments, continuous monitoring, regulatory compliance reviews, issue remediation tracking, and executive reporting. Develops risk methodologies, supports audits and examinations, advises on regulatory changes, and partners with technology, cybersecurity, data, compliance, and audit teams. Mentors junior analysts and helps strengthen enterprise risk awareness and decision-making.
Top Skills:
ArcherFfiecGlbaGrcHipaaExcelMicrosoft Power BiMicrosoft PowerpointMicrosoft SharepointMicrosoft TeamsMicrosoft VisioNistServicenow
Aerospace
Provides day-to-day IT assurance, systems administration, cybersecurity, and authorization support for DoD Collateral, SCI, and Special Access Program environments. Responsibilities include maintaining servers, networks, firewalls, security monitoring systems, and VTC systems; troubleshooting; patching; account administration; preparing authorization packages; identifying vulnerabilities; implementing countermeasures; supporting RMF compliance; and managing COMSEC equipment and media accountability.
Top Skills:
Common CriteriaComsecFirewallsLanMicrosoft Exchange Server 2010/2016Microsoft Windows 7/10Microsoft Windows Server 2012 R2Pl2 SystemsPl3/Pl4 Cross-Domain SolutionsRisk Management FrameworkSecurity Monitoring SystemsVtc SystemsWan
Automotive • Energy • Industrial • Manufacturing
Leads IT security and infrastructure strategy, operations, risk assessments, incident response, cloud security, vendor management, budgets, standards, and technology projects. Oversees infrastructure across servers, networks, cloud services, manufacturing sites, warehouses, offices, and global IT operations. Manages teams and collaborates with business leaders, vendors, and international IT stakeholders to ensure secure, reliable, scalable, and compliant technology environments.
Top Skills:
Cloud Security TechnologiesCloud ServicesEnterprise ApplicationsInfrastructure Management ToolsLanMicrosoftSecurity TechnologiesWan
Digital Media • Marketing Tech
Manages IT security projects, infrastructure, audits, compliance, security alerts, risk remediation, disaster recovery, and technology integrations. Coordinates with vendors, global IT teams, and local resources while supporting cloud, infrastructure, and workplace technology. Ensures alignment with ISO 27001, HITRUST, ISMS, client requirements, and organizational security policies. The role also provides technical guidance, documentation, training, and support for site expansions and multi-location IT operations.
Top Skills:
Client-Server SystemsCloud ComputingDatabase SystemsHitrustInformation Security Management Systems (Isms)Iso 27001Microsoft Defender
Information Technology • Internet of Things • Other • Cybersecurity • Infrastructure as a Service (IaaS)
Leads Verizon’s IT Sarbanes-Oxley compliance lifecycle across financial reporting systems. Responsibilities include owning the ITGC roadmap, automating control validation, leading internal and external audits, remediating technical deficiencies, managing cross-functional compliance projects, and presenting audit risks to executive leadership. The role requires expertise in SOX frameworks, IT controls, CI/CD, SDLC, databases, cloud security, and executive communication.
Top Skills:
Ci/Cd PipelinesCloud Infrastructure SecurityDatabase ArchitectureIt General Controls (Itgc)Software Development Lifecycle (Sdlc)
Aerospace • Transportation • Travel
Administers and secures enterprise networks, servers, Microsoft cloud infrastructure, endpoints, identity platforms, and virtualization environments. Manages firewalls, Okta, MDM, RMM, patching, vulnerability remediation, privileged access, MFA, and zero-trust controls. Supports incident response, security monitoring, risk assessments, compliance audits, backup and disaster recovery, and infrastructure health reporting. Collaborates with IT and security teams, documents procedures and changes, participates in security improvement initiatives, and supports on-call response.
Top Skills:
AzureAzure Front DoorConditional AccessCrowdstrike FalconDelinea Secret ServerDruvaEdrEnterprise StorageEntra IdFederationFirewallsHyper-VIdentity ManagementIds/IpsIntuneLinuxMdmMfaMicrosoft 365Microsoft PurviewMicrosoft SentinelNetwork SegmentationNinjaoneOktaPatch ManagementPowershellRbacRmmRoutersSIEMSsoSwitchesVeeamVirtualizationVMwareVpnWeb Application FirewallWindowsWireless NetworksWorkspace OneZero Trust
Energy
Monitor and triage cybersecurity alerts, investigate and respond to incidents, conduct threat hunts, contain compromised systems, document investigations, and improve detection rules and security awareness materials. The analyst works with Microsoft security tools, external SOC teams, SIEM and EDR platforms, and supports cybersecurity service desk tickets while following incident response playbooks and SLAs.
Top Skills:
CrowdstrikeCyber Kill ChainEmail Gateway Security SolutionsKusto Query Language (Kql)Microsoft Defender XdrMicrosoft IntuneMicrosoft PurviewNist Sp 800-61PowershellPythonSentineloneSIEM

Reposted 12 Days AgoSaved
Professional Services • Financial Services
Leads and supports SOC 1 and SOC 2 examinations, IT SOX compliance engagements, and technology risk projects. Responsibilities include risk assessment, control testing, documentation, workpaper review, issue evaluation, client communication, engagement coordination, budget monitoring, and supervising junior staff. The role evaluates IT general and automated controls across access, change management, cybersecurity, continuity, vendor management, and related areas while providing practical recommendations and supporting methodology, proposals, and recruiting initiatives.
Top Skills:
AuditboardDrataFieldguideHitrustIso/Iec 27001NistPci DssSoc 1Soc 2Sox Section 404VantaWorkiva
New
Track Smarter, Apply Better.
Ditch the spreadsheets. Organize your job search with our freeApplication Tracker.
Use For Free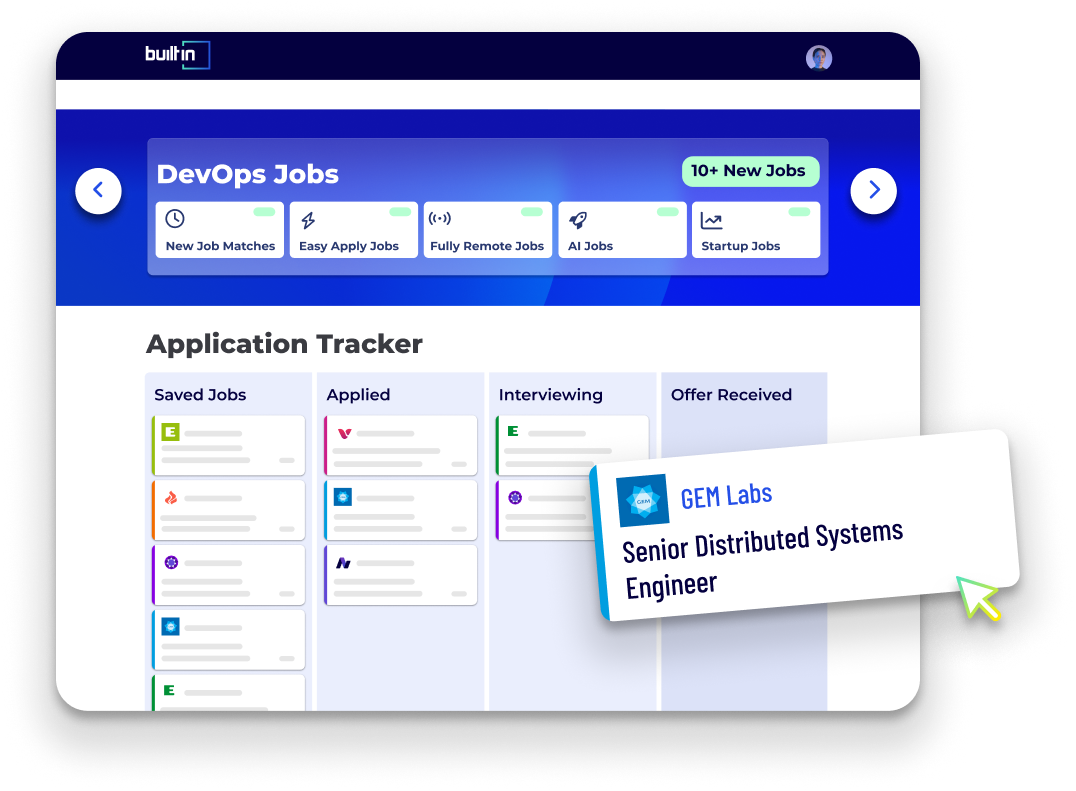

Healthtech
Leads IT compliance and governance activities, including IT general controls, SOX, PCI-DSS, information security, vendor risk assessments, disaster recovery, audits, and remediation tracking. The role manages audit-ready evidence, policies, procedures, control testing, root cause analysis, and stakeholder reporting while coaching junior team members. It is a remote position reporting to the Senior IT GRC Manager, with travel of up to 10%.
Top Skills:
Change ManagementDisaster RecoveryGdprHipaaIt General ControlsPci-DssSoxThird-Party Risk ManagementUser Access Management
Artificial Intelligence • Cloud • Fintech • Information Technology • Analytics • Financial Services • Cybersecurity
Leads IT audit engagements covering technology, cybersecurity, governance, and operational risks. Assesses technology risks and internal controls, evaluates control effectiveness, develops audit scopes and testing approaches, reviews workpapers, coaches audit teams, and communicates findings and recommendations to management. Requires 4–5 years of IT audit or technology risk experience, strong knowledge of cybersecurity and IT controls, and broad understanding of infrastructure, applications, data, cloud, and governance.
Top Skills:
Cloud TechnologiesCybersecurityIt ApplicationsIt Infrastructure

Logistics • Energy • Industrial • Manufacturing
Owns Solaris’s enterprise SDLC governance and SOX IT general controls program. Responsibilities include designing and operating controls, reviewing software releases, managing access and segregation-of-duties reviews, coordinating audits, evaluating SOC reports, tracking remediation, reporting compliance metrics, maintaining policies and evidence, and training stakeholders. The role partners with IT, cybersecurity, accounting, internal audit, vendors, and executives while building a scalable governance function.
Top Skills:
Azure DevopsCi/CdConfluenceExcelJIRANetSuitePower BISalesforceSap GrcSap S/4HanaServicemaxServicenowSharepointSuccessfactors

Legal Tech • Software
Leads second-line IT risk assurance, continuous ITGC testing, control architecture, risk register management, and control deficiency reporting. Serves as a subject matter expert on security frameworks and GRC, supports SOX and integrated audits, and leads FedRAMP Moderate/High pre-assessment reviews. Designs and optimizes risk and control matrices, interprets regulatory requirements, monitors control effectiveness, and briefs executives, auditors, regulators, and customers on technical risk and control matters.
Top Skills:
Ai ToolingGrc SystemsPowershellPythonSQL

13 Days AgoSaved
Agency • Information Technology • Professional Services
Supports IT data governance, compliance, risk assessments, audit readiness, data ownership, and responsible data management. The role coordinates data governance decisions, maintains compliance evidence, monitors data usage risks and key risk indicators, supports IM8 and Whole-of-Government reviews, develops guidance and training, and assists with data security risk assessments and policy updates. It works closely with the Chief Data Officer, Business Owners, Data Owners, auditors, and stakeholders to strengthen governance maturity and data stewardship.
13 Days AgoSaved
Agency • Information Technology • Professional Services
Monitor and strengthen the organisation’s cybersecurity posture through governance, risk management, compliance, vulnerability assessment, threat analysis, incident response, and security architecture reviews. The role develops security frameworks, advises project teams on secure design, tracks remediation, analyses logs and security events, coordinates cyber incident response, supports continuity planning, and leads security awareness and readiness exercises in alignment with Singapore Government and ITE cybersecurity standards.
Top Skills:
Business Continuity And Disaster RecoveryIncident ResponseLog AnalysisSdlcThreat IntelligenceVulnerability AssessmentZero Trust

Financial Services
Leads IT compliance risk management activities, including regulatory assessments, issue monitoring, policy reviews, compliance reporting, metrics development, and regulatory update communications. Advises internal stakeholders, supports committees and projects, identifies process improvements, and ensures alignment with IT controls, securities regulations, banking requirements, SOX Section 404, OCC, SEC, FINRA, and state securities regulations.
Top Skills:
DatabasesInformation Security ControlsSpreadsheets

Social Impact
Designs, implements, configures, and supports enterprise cybersecurity solutions across IAM, endpoint, network, email, application, cloud, and security awareness domains. Conducts vulnerability assessments, threat hunting, incident investigation, security tool tuning, policy development, and security architecture reviews. Serves as a security subject matter expert on technology projects, collaborates with an MSSP, provides incident escalation support, and maintains availability for critical security operations.
Top Skills:
AtpAzureAzure Active DirectoryAzure SentinelAzure VmCisco FirewallsCisco Umbrella Dns SecurityContent FilteringEdrEmail Security GatewaysEndpoint SecurityIamIntuneMicrosoft DefenderNetwork FirewallsNetwork Security GroupsOffice 365SsoVirtualizationVMwareWindows ServerXdr
Information Technology • Software
Monitors and responds to security alerts and incidents across SIEM, endpoint, cloud, email, and network security tools. Collaborates with IT teams and service providers, improves security policies and procedures, supports ISO 27001 and SOC compliance, assists with audits and security assessments, and provides regional IT security support, including occasional out-of-hours incident response.
Top Skills:
AntivirusCloud SecurityDatabasesDns ProtectionEndpoint ProtectionFirewallsIso 27001ExcelMicrosoft Office 365Microsoft TeamsNistPci-DssSharepointSIEMSoc 2Vulnerability ManagementWeb Filtering
Information Technology • Software
Leads IT operations and compliance, managing an IT Specialist, endpoint and identity systems, security incidents, vendors, and employee IT support. Owns SOC 2 and GovRAMP audits, compliance automation in Vanta, control mapping, risk assessments, policy maintenance, evidence collection, remediation, and continuous monitoring. Partners cross-functionally to close compliance gaps, support customer security reviews, and deliver effective onboarding and offboarding.
Top Skills:
AzureAzure VpnCisaCisspComptia Security+Google WorkspaceGovrampmacOSMdmMicrosoft 365Microsoft Active DirectoryMicrosoft Defender For EndpointNist Sp 800-53Patch ManagementSoc 2VantaWindows
Financial Services
Leads the cybersecurity program, including strategy, governance, security operations, incident response, risk and vulnerability management, compliance, architecture, access controls, awareness, vendor oversight, and executive reporting. The role secures cloud, endpoint, network, identity, email, application, and data environments while managing audits, remediation, security metrics, and long-term resilience initiatives.
Top Skills:
Active DirectoryAzureCis ControlsCisco Networking And Security PlatformsCisco UmbrellaCloudflareData Loss PreventionEdr/XdrEmail SecurityEncryptionExchange OnlineFirewallsFortinetIso 27001Microsoft 365Microsoft Defender AtpMicrosoft Entra IdMicrosoft ExchangeMultifactor AuthenticationNistSIEMVulnerability ManagementZero-Trust Security

Industrial
Administers and monitors cybersecurity systems, including firewalls, IDS/IPS, endpoint protection, and security monitoring tools. Detects and responds to incidents, conducts vulnerability assessments and penetration testing, enforces security policies, supports secure system deployments, maintains regulatory compliance, trains staff, and documents incidents and recommendations.
Top Skills:
AWSAzureEndpoint ProtectionFirewallsGCPIntrusion Detection And Prevention Systems (Ids/Ips)PowershellPythonSIEMVpns
Information Technology • Logistics • Security • Software
Provides IT, systems administration, knowledge management, and cybersecurity compliance support for an Army Headquarters organization at the Pentagon. Responsibilities include managing classified networks, user access, hardware, COMSEC accounts, RMF authorization packages, ATOs, ATCs, security inspections, remediation plans, IT acquisitions, continuity planning, and system integration. Requires Pentagon or DoD network experience, an active Top Secret clearance with SCI eligibility, and an IAT Level II certification.
Top Skills:
Authority To Connect (Atc)Authority To Operate (Ato)Comptia A+Comptia Network+Comptia Security+ComsecEmassEnterprise Task Management Software Solution (Etms2)ExcelJwicsMicrosoft Modern Desktop AdministratorMS OfficeNiprOutlookPowerPointRisk Management Framework (Rmf)SharepointSiprWord

Let Your Resume Do The Work
Upload your resume to be matched with jobs you're a great fit for.
Success! We'll use this to further personalize your experience.
Top Companies Hiring Cybersecurity Roles
See All






All Filters
Total selected ()
No Results
No Results
