


The key objectives of the TPRM Program are to:
- Assess the risk of third-party relationships which drive the rigor of risk management activities both during the third-party onboarding and ongoing monitoring lifecycle phases using the TPRM Program’s formula-based risk methodology
- Act as a liaison across key internal stakeholder teams (Procurement, Legal, Enterprise Security and the Business) to ensure clear and accurate communication of third-party risks aligned to risk management activities in order to complete risk assessments in a timely manner
- Identify TPRM program enhancements aimed at the effective and efficient management of third-party risk in order to support Business strategic initiatives
Reporting to the TPRM Manager, the TPRM Risk Analyst will be expected to have strong experience operating in a risk-based, data-driven model that will accommodate the business’s need to onboard vendors in a shortened timeframe, all while managing expectations and heightened scrutiny of both internal and external stakeholders including our customers. The TPRM Risk Analyst will understand and clearly communicate not only the “What” but also the “Why” in terms of third-party risk management activities in order to support efficient and effective third-party risk management as MongoDB continues to grow. This role requires substantial ability to interpret data and apply risk knowledge and judgment as the TPRM Risk Analyst manages a complex ecosystem of data, regulations, and stakeholder relationships while continuously identifying areas of enhancement to support effective third-party risk management.
We are looking to speak to candidates who are based in Dublin for our hybrid working model.
Responsibilities:Risk Assessment Validation & Remediation
- Strong experience in managing the full lifecycle of a Third Party from Sourcing to Payment
- Independently validate inherent risk rating and Criticality designation for all third-party relationships with minimal intervention while proactively flagging any concerns to the TPRM Manager
- Review third-party provided information and documentation for all third-party relationships in accordance with TPRM assessment methodology, proactively flagging any gaps or follow-up questions
- Lead communication to third parties to remediate gaps for all High Risk and Critical third-party relationships, including documentation of remediation plans
Reporting & Trend Analysis
- Independently lead portfolio-level trend analysis, build leadership- and audit-facing reporting, and translate findings into risk-based recommendations
Oversight & Periodic Review
- Lead identification, tracking, and review of the adequacy of completion of SME reviews and assessments for all third-party relationships at onboarding with minimal oversight from manager
- Independently provide oversight of the periodic review process, including identification and escalation of higher-risk findings or gaps
Mentorship & Stakeholder Support
- Mentor the Associate TPRM Risk Analyst and support the TPRM Manager in audit and customer discussions
Experience & Education:
- 7-10 years of experience in Third-Party Risk Management (TPRM) or Governance, Risk & Compliance (GRC)
- Demonstrated experience performing substantive risk assessments and applying formula-based or quantitative risk methodologies
- Bachelor’s degree in a relevant field (Cybersecurity, Business, Information Systems)
- Certifications (at least one required): CRISC (Certified in Risk and Information Systems Control), CISM (Certified Information Security Manager), CTPRP (Certified Third-Party Risk Professional), or CRVPM (Certified Regulatory Vendor Program Manager) up to or in process of Level V
Technical & Operational Proficiency:
- Proficiency with a well established TPRM platform, including the ability to interpret intake data, Data Level classifications, and inherent risk scoring logic
- Deep operational understanding of standard control frameworks (NIST SP 800-53, ISO 27001, SOC 2, SIG Core/Lite, CAIQ)
- Working knowledge of heightened regulatory requirements relevant to the third-party population (e.g., DORA, GDPR, NIS2, FedRAMP, PCI-DSS, OCC, CCPA)
Core Competencies:
- Analytical Rigor: ability to interpret data and apply risk knowledge and judgment to validate risk ratings and Criticality designations, not just process tickets
- Communication: ability to translate portfolio-level findings into clear, leadership- and audit-facing risk recommendations
- Check-and-Challenge: comfort with constructive challenge of third-party or SME responses to ensure gaps are identified and remediated
- Leadership: ability to mentor junior team members and represent TPRM in audit and customer-facing discussions
MongoDB is built for change, empowering our customers and our people to innovate at the speed of the market. We have redefined the data platform for the AI era, enabling builders to create, transform, and disrupt industries with software. MongoDB’s unified data platform, the most widely available, globally distributed data platform on the market, helps organizations modernize legacy workloads, embrace innovation, and unleash AI. Our cloud-native platform, MongoDB Atlas, is the only globally distributed, multi-cloud data platform and is available across AWS, Google Cloud, and Microsoft Azure.
With offices worldwide and over 67,000 customers, including AI-native startups and approximately 75% of the Fortune 100, relying on MongoDB for their most important applications, we’re powering the next era of software.
Our compass at MongoDB is our Leadership Commitment, guiding how and why we make decisions, show up for each other, and win. It’s what makes us MongoDB.
To drive the personal growth and business impact of our employees, we’re committed to developing a supportive and enriching culture for everyone. From employee affinity groups, to fertility assistance and a generous parental leave policy, we value our employees’ wellbeing and want to support them along every step of their professional and personal journeys. Learn more about what it’s like to work at MongoDB, and help us make an impact on the world!
MongoDB is committed to providing any necessary accommodations for individuals with disabilities within our application and interview process. To request an accommodation due to a disability, please inform your recruiter.
MongoDB is an equal opportunities employer.
Req. ID: 426442
Skills Required
- 7-10 years of experience in Third-Party Risk Management or Governance, Risk & Compliance
- Bachelor's degree in Cybersecurity, Business, Information Systems, or a relevant field
- At least one certification: CRISC, CISM, CTPRP, or CRVPM up to or in process of Level V
- Experience performing substantive risk assessments using formula-based or quantitative risk methodologies
- Proficiency with an established Third-Party Risk Management platform, including intake data, data classifications, and inherent risk scoring logic
- Operational understanding of NIST SP 800-53, ISO 27001, SOC 2, SIG Core/Lite, and CAIQ control frameworks
- Working knowledge of DORA, GDPR, NIS2, FedRAMP, PCI-DSS, OCC, and CCPA requirements
- Ability to interpret data, validate risk ratings, and apply risk judgment
- Ability to communicate risk recommendations to leadership, auditors, customers, stakeholders, and third parties
- Experience challenging and remediating third-party or subject matter expert responses
- Experience mentoring junior team members
- Based in Dublin and able to work in a hybrid model
What the Team is Saying


MongoDB Compensation & Benefits Highlights
-
Parental & Family Support — Parental leave is outlined at 20 weeks fully paid and gender‑neutral (with a one‑year tenure requirement), with return‑to‑work flexibility noted. Family‑building support includes 90% reimbursement up to $50,000 for fertility, adoption, or surrogacy, plus backup child/elder care services.
-
Healthcare Strength — Multiple medical plan options (Cigna and Kaiser HMO in CA) are offered, with low or no employee‑only payroll deductions on certain plans and preventive care covered at 100%. Separate dental (Cigna) and vision (EyeMed) benefits are also provided.
-
Wellbeing & Lifestyle Benefits — Mental‑health resources include Spring Health (up to 10 therapy video visits/year), Headspace for employees and dependents, an EAP, and a Mental Health First Aider program. Day‑to‑day perks and flexibility include flexible PTO, 11 U.S. holidays, and company‑paid in‑office lunches up to three days per week under the hybrid model.
MongoDB Insights

What We Do
The database market is big. How big? Well, according to IDC, it’ll reach $153 billion by 2027. And MongoDB is at the forefront of that innovation with thousands of customers across the globe. We empower developers and businesses to build and deploy the applications they want, wherever they want.
Why Work With Us
We are ambitious. We are passionate about creativity. And we believe the best paths are the ones we have yet to forge.
Gallery




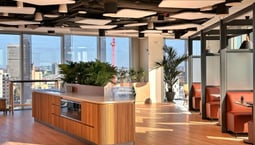


MongoDB Offices
Hybrid Workspace
Employees engage in a combination of remote and on-site work.
MongoDB provides multiple working model options for our employees, including the flexibility to work from home to opportunities for collaboration and social interaction in a MongoDB office.


