Employee Applicant Privacy Notice
Who we are:
Shape a brighter financial future with us.
Together with our members, we’re changing the way people think about and interact with personal finance.
We’re a next-generation financial services company and national bank using innovative, mobile-first technology to help our millions of members reach their goals. The industry is going through an unprecedented transformation, and we’re at the forefront. We’re proud to come to work every day knowing that what we do has a direct impact on people’s lives, with our core values guiding us every step of the way. Join us to invest in yourself, your career, and the financial world.
The role:
As a Senior Staff Identity and Access Management (IAM) Engineer at SoFi, you will be at the forefront of securing SoFi’s IAM ecosystem—architecting, automating, and scaling identity solutions across our workforce, cloud, and rapidly evolving AI infrastructure. In this high-impact role, you will eliminate manual toil through automation, champion Zero Trust values, and ensure seamless regulatory compliance. Beyond workforce identity, you will pioneer the future of our security posture by maturing cloud and non-human identity (NHI) capabilities—designing scalable access controls for AWS workloads, governing the full lifecycle of service accounts and API credentials, and partnering directly with engineering teams to embed identity-first security into next-generation AI-enabled systems. If you're ready to tackle complex identity challenges at scale and define how humans, machines, and AI securely interact, this is your opportunity to make a lasting mark.
What you’ll do:
As a Senior Staff Identity and Access Management Engineer, you will define and execute the multi-year architecture and strategy for SoFi's IAM, Cloud IAM, Non-Human Identity (NHI), and AI security capabilities across enterprise domains. Daily responsibilities and essential functions include:
- Define and drive the multi-year technical roadmap and architecture for Identity and Access Management across cloud, SaaS, and on-premises systems utilizing Okta, AWS, and associated identity technologies.
- Architect and automate secure, least-privilege identity controls for human and non-human identities across multi-account AWS environments, including federation, workload identities, credential lifecycle management, and infrastructure-as-code.
- Pioneer AI security architecture aligned to OWASP Top 10 for Agentic Applications, designing scalable controls for agent repositories, agent gateways, MCP servers, and least-privilege agent access.
- Partner with Engineering, Security, and Information Technology leadership to establish scalable identity and authorization standards for Okta, AWS, Secrets Management, and AI-enabled applications within a Zero Trust security architecture.
- Lead cross-functional initiatives and coordinate with IAM leadership and project management on technical planning, execution, and reporting across concurrent enterprise programs.
- Mentor and elevate Staff (IC4) and Senior (IC3) IAM engineers, leading design reviews and guiding the team to maintain our IAM governance and certification programs to meet strict financial services compliance obligations.
- Evaluate and select tools, methods, techniques, and evaluation criteria to meet operational goals, reduce systemic complexity, and remediate excessive, orphaned, and persistent access.
- Advise internal teams on third-party access architectures, security policies, and IAM best practices.
What you’ll need:
- Education & Minimum Experience Requirements: Bachelor’s Degree in Computer Science, Information Security, or a related field + 4+ years of experience in Identity and Access Management (IAM) or Security Engineering OR Master’s Degree + 3+ years of experience
- Proven experience designing, configuring, and deploying Okta’s Identity Platform at enterprise scale, including Okta Identity Governance and Okta Workflows.
- Demonstrated experience designing and automating identity and authorization controls in AWS, including AWS IAM Identity Center, IAM roles, cross-account access, federation, and least-privilege policy design.
- Hands-on experience managing the full lifecycle and security of non-human identities (NHI), such as service accounts, workload identities, API credentials, certificates, and secrets.
- Experience securing access for AI-enabled applications or autonomous agents, including service identity, data authorization, API/tool permissions, auditability, and AI infrastructure (e.g., MCP servers, open APIs, agent skills, and agent gateways).
- Deep knowledge of cybersecurity and IAM concepts, Zero Trust architectures, and regulatory compliance frameworks supporting medium-to-large organizations.
- Proven experience providing architectural oversight, design review leadership, and mentorship to engineers supporting Cloud Identity, Privileged Access Management (PAM), or Secrets Management solutions.
- Okta Certified Administrator certification.
- Exceptional problem-solving, research, written, and verbal communication skills, with the ability to work both autonomously and collaboratively across cross-functional engineering and security teams.
Nice to have:
- 12+ years of progressive experience in Identity and Access Management, Cloud Security, or Security Architecture within complex, regulated enterprises.
- Deep hands-on experience with AWS IAM in a multi-account environment, including permission boundaries, Service Control Policy (SCP)-aware authorization design, and IAM Access Analyzer.
- Experience defining, deploying, and auditing AWS IAM roles across multiple organizations using Terraform or equivalent Infrastructure as Code (IaC), CI/CD policy checks, and policy-as-code.
- Experience with automated NHI discovery, ownership attestation, risk reduction, and remediation of long-lived or unmanaged credentials.
- Strong understanding of financial services regulations and guidance including GLBA, PCI-DSS, SOC 1/SOC 2, and SOX.
- Advanced Okta certifications (e.g., Okta Certified Consultant, Architect, or Developer) and/or industry security certifications (e.g., CISSP, CISM).
Skills Required
- Bachelor's degree in Computer Science, Information Security, or a related field plus 4 or more years of IAM or Security Engineering experience, or a master's degree plus 3 or more years of experience
- Enterprise-scale experience designing, configuring, and deploying Okta Identity Platform, including Okta Identity Governance and Okta Workflows
- Experience designing and automating AWS identity and authorization controls, including IAM Identity Center, IAM roles, cross-account access, federation, and least-privilege policies
- Experience managing the lifecycle and security of non-human identities, including service accounts, workload identities, API credentials, certificates, and secrets
- Experience securing AI-enabled applications or autonomous agents, including service identity, data authorization, API and tool permissions, auditability, and AI infrastructure
- Deep knowledge of cybersecurity, IAM, Zero Trust architecture, and regulatory compliance frameworks
- Experience providing architectural oversight, leading design reviews, and mentoring engineers working with Cloud Identity, PAM, or Secrets Management
- Okta Certified Administrator certification
- Exceptional problem-solving, research, written, and verbal communication skills
- 12 or more years of progressive IAM, Cloud Security, or Security Architecture experience in complex regulated enterprises
- Advanced Okta certifications, such as Okta Certified Consultant, Architect, or Developer, and/or CISSP or CISM certification
- Experience with AWS IAM in multi-account environments, including permission boundaries, SCP-aware authorization design, and IAM Access Analyzer
- Experience deploying and auditing AWS IAM roles across multiple organizations using Terraform or equivalent IaC, CI/CD policy checks, and policy-as-code
- Experience with automated non-human identity discovery, ownership attestation, risk reduction, and remediation of long-lived or unmanaged credentials
- Understanding of financial services regulations including GLBA, PCI-DSS, SOC 1, SOC 2, and SOX
What the Team is Saying






SoFi Compensation & Benefits Highlights
-
Healthcare Strength — Health coverage, mental-health support, and wellness resources are prominent, including medical plans with HSA/FSA options, therapy/coaching access, and company-paid life and disability insurance. These offerings are positioned as a standout part of the total package.
-
Parental & Family Support — Up to 12 weeks of fully paid parental leave is complemented by fertility and adoption support, subsidized backup childcare and eldercare, caregiver leave, and pet insurance. The breadth of family benefits indicates strong support for different life stages and caregiving needs.
-
Leave & Time Off Breadth — Flexible vacation for exempt employees, paid holidays, sick time for non-exempt staff, paid volunteer time, and early-release “SoFi Fridays” expand time-away options. Together, these programs emphasize flexibility and recovery time.
SoFi Insights

What We Do
SoFi wasn’t built to be a bank. Or a technology company. We were built for one mission: help people achieve financial independence so they can realize their ambitions. Redefining an entire industry isn’t easy work—and it’s not for the faint of heart. It takes a certain kind of team. People with diverse perspectives and expertise, united by a common sense of purpose. People willing to challenge assumptions but always do the right thing. People proving that innovation and responsibility don’t have to compete, but can come together to create something truly unconventional in the world. For the last eight years, we’ve been charting this new path forward. We call it The SoFi Way. At SoFi, we don’t just talk about culture: we live it. The SoFi Way is how we show up every day, how we make decisions, and how we build for our members, clients, and each other.
Why Work With Us
Together with our members, we’re changing the way people think about and interact with personal finance. We’re a next-generation Fintech company using innovative, mobile-first technology to help our members reach their goals. The industry is going through an unprecedented transformation, and we’re at the forefront.
Gallery
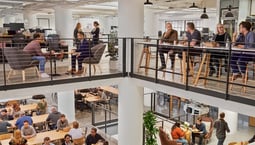


SoFi Offices
Hybrid Workspace
Employees engage in a combination of remote and on-site work.
For the majority of our workforce who work on a hybrid schedule, the in-office requirement is a handful of days per month!