

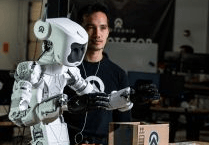
Apptronik is a human-centered robotics company developing AI-powered robots to support humanity in every facet of life. Our flagship humanoid robot, Apollo, is built to collaborate thoughtfully with people, starting with critical industries such as manufacturing and logistics, with future applications in healthcare, the home, and beyond.
We operate at the cutting edge of Applied AI, applying our expertise across the full robotics stack to solve some of society's most important problems. You will join a team dedicated to bringing Apollo to market at scale, tackling the complex challenges like safety, commercialization, and mass production to change the world for the better.
JOB SUMMARY
As Apptronik scales its humanoid robotics business, we are seeking a Director of Enterprise Security to build and lead our enterprise information security program. Reporting to the Director of IT, the CISO will own Apptronik's risk management and governance frameworks and drive the company toward ISO 27001 certification. This role is focused on enterprise security protecting corporate systems, data, identities, and SaaS estate. The successful candidate is a pragmatic security professional who can translate framework requirements into clear policy and well-prioritized controls, stand up an ISMS quickly, and partner effectively with IT, legal, HR, finance, and operations leaders.
ESSENTIAL DUTIES AND RESPONSIBILITIES
- Define and own Apptronik's enterprise information security strategy, roadmap, and policies, with clear executive-level reporting on risk posture, program maturity, and key initiatives
- Design, implement, and operate an ISO 27001-aligned Information Security Management System (ISMS) — including scoping, Statement of Applicability, risk treatment plans, and the full set of Annex A controls — and drive Apptronik to ISO 27001 certification
- Own information security risk management — establish the information security risk register, risk assessment methodology, risk acceptance and treatment processes, and recurring reporting to executive leadership
- Build and run the security governance program — policies, standards, control ownership, exception handling, internal audit, control testing, and management review cadence
- Operate the SOC 2 program in parallel with ISO 27001, mapping shared controls, owning evidence collection, and managing relationships with external auditors and assessors
- Establish the enterprise security architecture across cloud for corporate workloads, SaaS estate, and corporate endpoints
- Build and run vulnerability management, threat detection and response, and incident response capabilities for enterprise systems — selecting and operating EDR, SIEM, DLP, and email security tooling; defining playbooks; and leading tabletop exercises
- Own identity and access management governance in partnership with IT — enforcing least-privilege, SSO, MFA, conditional access, SCIM provisioning, privileged access management, and periodic access reviews across all enterprise systems
- Establish third-party security risk management and vendor security review processes; evaluate SaaS, cloud, and supply chain partners against contractual and regulatory security requirements
- Drive security awareness and training programs across the company, tailored to engineering, manufacturing, operations, and executive audiences
- Partner with the CIO to represent Apptronik in customer, partner, investor, and regulatory engagements, supporting security audits, due diligence, and enterprise security reviews.
- Build, mentor, and grow a high-performing security and GRC team over time; in the near term, operate as a working leader who designs and implements controls directly
SKILLS AND REQUIREMENTS
- 12+ years of progressive information security experience, including 5+ years leading enterprise security programs as a Director, Head of Security, or senior security leadership role.
- Deep, demonstrated fluency with ISO 27001 — including the ISMS lifecycle, scoping, Statement of Applicability, risk assessment methodology, and end-to-end implementation of Annex A controls
- Track record of building enterprise security programs from the ground up at high-growth companies and driving them through ISO 27001 certification (and ideally SOC 2 Type I/II in parallel)
- Strong expertise in risk management and governance — risk registers, risk treatment, control frameworks, policy development, exception handling, internal audit, and executive-level risk reporting
- Strong working knowledge of additional frameworks and regulations as relevant — NIST CSF, NIST 800-53, CIS Controls, GDPR, CCPA, and export controls (ITAR/EAR preferred) given the robotics context
- Hands-on architectural depth across cloud platforms (AWS, GCP, and/or Azure) for corporate/enterprise workloads, including IAM, network security, encryption, and logging
- Strong identity and access management expertise — Okta, SSO, MFA, conditional access, SCIM, lifecycle management, and privileged access controls
- Endpoint and corporate IT security experience across Linux, macOS, and Windows — MDM (Jamf, Intune), EDR, disk encryption, patch and configuration management
- Experience operating detection and response capabilities — SIEM, EDR, log pipelines, threat intelligence, and incident response — including leading real incidents end-to-end
- Demonstrated ability to translate framework requirements into pragmatic, well-prioritized controls without slowing the business unnecessarily
- Excellent written and verbal communication skills, including the ability to brief executives and the board, write clear policy, and engage external auditors and customers
- Strong leadership presence — sound judgment, calm under incident pressure, and the ability to build trust quickly across IT, legal, HR, finance, and operations
NICE TO HAVE
- Industry certifications such as CISSP, CISM, CISA, CCSP, ISO 27001 Lead Implementer or Lead Auditor
- Experience leading enterprise security at a hardware, robotics, manufacturing, automotive, or aerospace company
- Experience with GRC platforms (e.g., Vanta, Drata, OneTrust, ServiceNow GRC) to operationalize ISMS evidence and control monitoring
- Experience with additional frameworks such as NIST CSF audits, HITRUST, PCI-DSS, or TISAX
- Experience operating in environments subject to ITAR/EAR export controls or working with U.S. government / defense customers
- Prior experience scaling a security and GRC team from individual contributor to multi-discipline organization
EDUCATION and/or EXPERIENCE
- 12+ years of information security experience required, with substantial time in security leadership roles; Bachelor's degree in Computer Science, Information Security, Engineering, or a related field preferred — equivalent experience accepted
- Master's degree (e.g., MS in Information Security, MBA with security focus) is a plus
- Active senior security certifications (CISSP, CISM, CCSP, ISO 27001 Lead Implementer/Auditor, GIAC) strongly preferred
PHYSICAL REQUIREMENTS
- Prolonged periods of sitting at a desk and working on a computer
- Periodic travel between Apptronik sites, customer locations, and industry events
- Vision to read printed materials and a computer screen
- Hearing and speech to communicate
*This is a direct hire. Please, no outside Agency solicitations.
Apptronik provides equal employment opportunities to all employees and applicants for employment and prohibits discrimination and harassment of any type without regard to race, color, religion, age, sex, national origin, disability status, genetics, protected veteran status, sexual orientation, gender identity or expression, or any other characteristic protected by federal, state or local laws.
Skills Required
- 12+ years of progressive information security experience
- 5+ years leading enterprise security programs in a Director, Head of Security, or senior security leadership role
- Deep expertise in ISO 27001, including ISMS lifecycle, scoping, Statement of Applicability, risk assessment, and Annex A controls
- Experience building enterprise security programs from the ground up and driving ISO 27001 certification
- Strong risk management and security governance experience
- Working knowledge of NIST CSF, NIST 800-53, CIS Controls, GDPR, CCPA, and export controls
- Hands-on cloud security architecture experience with AWS, GCP, and/or Azure
- Strong identity and access management expertise, including Okta, SSO, MFA, conditional access, SCIM, and privileged access controls
- Endpoint and corporate IT security experience across Linux, macOS, and Windows
- Experience with MDM, EDR, SIEM, logging, threat intelligence, and incident response
- Excellent written and verbal communication skills, including executive and board briefings
- Strong leadership presence and ability to build trust across business functions
- CISSP, CISM, CISA, CCSP, ISO 27001 Lead Implementer or Lead Auditor, or GIAC certification
- Experience leading enterprise security at a hardware, robotics, manufacturing, automotive, or aerospace company
- Experience with GRC platforms such as Vanta, Drata, OneTrust, or ServiceNow GRC
- Experience with HITRUST, PCI-DSS, TISAX, NIST CSF audits, or ITAR/EAR environments
- Bachelor's degree in Computer Science, Information Security, Engineering, or a related field
- Master's degree in Information Security, Business Administration with security focus, or related field
Apptronik Compensation & Benefits Highlights
-
Healthcare Strength — Medical coverage includes multiple UnitedHealthcare plan options with an employer contribution toward premiums, and mental-health support is listed. Feedback suggests this core coverage meets the standard expectations for a tech employer.
-
Leave & Time Off Breadth — Flexible PTO, paid holidays and sick days, and paid parental/family leave are advertised, with an onsite Mother’s Room at the Austin HQ. Feedback suggests the breadth of time-off and family provisions is a notable part of the offering, even if specific durations aren’t publicly detailed.
-
Equity Value & Accessibility — Company equity and performance bonuses are included in the published package, with relocation assistance also noted on some profiles. Feedback suggests these elements can add upside to total compensation depending on role and grant terms.
Apptronik Insights

What We Do
Apptronik is building robots for the real world to improve human quality of life and to help solve the ever-increasing labor shortage problem. Our team has been building some of the most advanced robots on the planet for years, dating back to the DARPA Robotics Challenge. We apply our expertise across the full robotics stack to some of the most important and impactful problems our society faces, and expect our products and technology to change the world for the better. We value passion, creativity, and collaboration to help us overcome existing technological barriers in the industry to create truly innovative products.
Why Work With Us
At Apptronik, we don't see a future where man competes against machine. Instead, we envision a harmonious world where man and machine coexist. Our mission statement, "It is not Man vs. Machine, but Man + Machine," encapsulates our belief that the synergy between humans and robots will pave the way for a brighter, more advanced future.
Gallery
Apptronik Offices
Hybrid Workspace
Employees engage in a combination of remote and on-site work.
