

Maximum of 25 job preferences reached.
Top Remote Senior Level Cybersecurity & IT Jobs

Information Technology • Professional Services • Defense • Manufacturing
Conducts independent cybersecurity assessments of MARAD information systems across authorization, reauthorization, and continuous monitoring activities. Evaluates management, operational, and technical controls under NIST RMF; develops assessment plans, reports, risk assessments, and remediation recommendations; validates evidence and system compliance; supports ATO decisions; enters data into CSAM; and collaborates with federal cybersecurity stakeholders.
Top Skills:
Authority To Operate (Ato)Cyber Security Assessment And Management (Csam)Nist Risk Management Framework (Rmf)Nist Sp 800-30Nist Sp 800-37Nist Sp 800-53APlan Of Action And Milestones (Poa&M)

Information Technology • Professional Services • Cybersecurity • Defense
Manages information assurance and computer network defense activities, including security operations, vulnerability management, risk assessments, certification and accreditation, security documentation, configuration management, and policy enforcement. Supports classified information systems by maintaining security posture, assessing system changes, preparing security plans and accreditation packages, and providing technical documentation. Requires a bachelor’s degree or equivalent experience, six years of relevant experience, DoD IAT II or IAM II certification, and an active TS/SCI clearance with the ability to obtain a CI polygraph.
Top Skills:
Computer Network DefenseConfiguration ManagementInformation AssuranceMicrosoft PowerpointMicrosoft VisioMicrosoft WordVulnerability Management

Cybersecurity
Owns the FedRAMP-authorized AWS GovCloud environment, ensuring reliability, security, compliance, patching, vulnerability remediation, continuous monitoring, deployments, hardening, audits, incident response, and on-call support. The role requires hands-on Kubernetes, AWS, infrastructure-as-code, CI/CD, vulnerability management, automation, and regulated-environment experience, while collaborating with SRE and security teams.
Top Skills:
AnsibleAws GovcloudCloudFormationFips-Validated CryptographyGithub ActionsGoJenkinsKubernetesNessusOpenscapPythonQualysRubySIEMTenableTerraform
Artificial Intelligence • Healthtech
Designs, implements, and operates Azure-native security controls for identity, networking, and workloads. Manages Defender for Cloud and Microsoft Sentinel, implements Conditional Access, MFA, and Zero Trust patterns, embeds security into Infrastructure-as-Code pipelines, monitors cloud posture, supports incident response, drives remediation, and maintains compliance documentation and metrics. Partners with cloud and infrastructure security teams to ensure secure, resilient, and compliant Azure environments.
Top Skills:
Conditional AccessInfrastructure As CodeAzureMicrosoft Defender For CloudMicrosoft SentinelMulti-Factor AuthenticationPolicy As CodeZero Trust

Insurance
Leads the cybersecurity operations program, overseeing monitoring, incident response, vulnerability management, threat intelligence, endpoint security, identity protection, and security controls. Manages security technologies, vendors, incident playbooks, compliance support, dashboards, and on-call processes while protecting regulated healthcare and financial information. Partners with IT, compliance, legal, privacy, risk, and executive teams, and leads and develops security operations personnel.
Top Skills:
Cloud PlatformsConditional AccessEdr/XdrEmail SecurityMfaMitre Att&CkNetwork SecuritySaaSSIEM
New
Cut your apply time in half.
Use ourAI Assistantto automatically fill your job applications.
Use For Free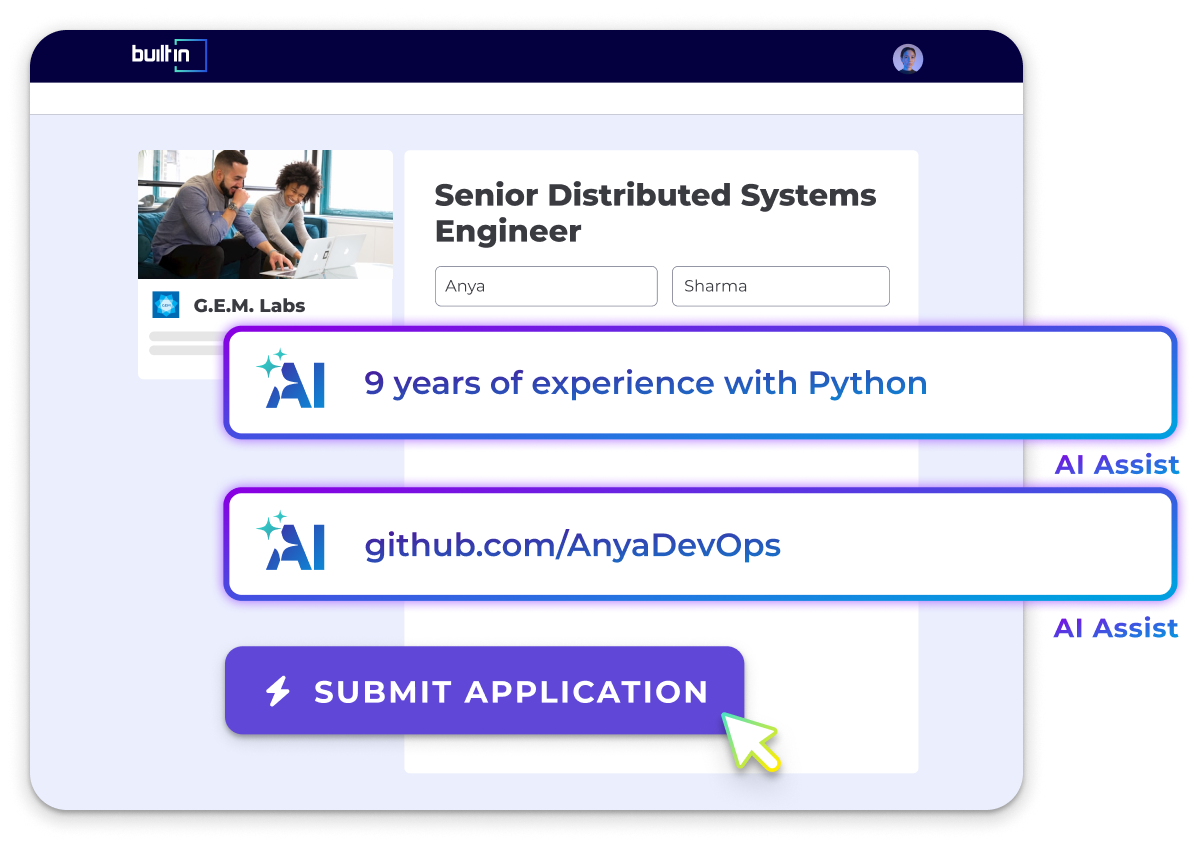

Database
Own technical wins for cybersecurity deals by designing ransomware-recovery, immutable and air-gapped vaulting, identity-resilience, and DSPM architectures. Lead discovery, demos, technical workshops, proof-of-concept pilots, reference architectures, executive presentations, and business cases. Partner with security sales specialists, customers, and technology partners while supporting technical qualification, deal progression, and roadmap feedback.
Top Skills:
Active DirectoryAi Security ToolsAir-Gapped VaultingAPIsBackup And Recovery SystemsData Security Posture ManagementHybrid CloudImmutable StorageMicrosoft Entra IdPowershellPython

Artificial Intelligence • Gaming • Software • Generative AI
Lead security engineering for a federal health supply chain and logistics software product line. Own security architecture through authorization, establish engineering standards, assess and remediate complex findings, advise stakeholders on risk, and mentor engineers. The role requires federal security framework expertise, cloud security experience, cross-team remediation leadership, and eligibility for a Public Trust background investigation. Preferred experience includes federal health IT, ATO packages, Kubernetes security, incident response, HIPAA, and Agile or SAFe environments.
Top Skills:
AWSAzureNist 800-53Risk Management Framework (Rmf)

Software
Designs and operates secure multi-cloud environments across GCP, Azure, and AWS. Responsibilities include cloud and network security architecture, SIEM alert monitoring and optimization, SaaS security, IAM, compliance assessments, incident response, firewall and access reviews, security documentation, and customer presentations. The role also supports security automation, risk remediation, and governance across frameworks including GDPR, SOC 2, ISO 27001, CMMC, and CSA STAR.
Top Skills:
Amazon Web Services (Aws)Arm TemplatesBashCloudFormationDevsecopsDockerEntra IdGoogle Cloud Platform (Gcp)IamKubernetesAzurePowershellPythonSIEMTerraform
Information Technology • Professional Services • Consulting • Cybersecurity
Conduct PCI DSS compliance assessments and audits for global clients, evaluating security controls, documentation, systems, and processes. Identify compliance gaps, document findings, prepare audit reports, and provide remediation guidance. The consultant communicates with client stakeholders, manages audit engagements, maintains quality standards, and stays current with PCI DSS and cybersecurity practices. Full professional fluency in Japanese is required, along with an active QSA certification and at least three years of information security and PCI DSS assessment experience.
Top Skills:
Access ControlsCmmcEncryptionFedrampHitrustIso 27001Network SecurityNetwork SegmentationPci DssSoc 2

Reposted 3 Days AgoSaved
Software
Lead incident response program design and execution, run tabletop exercises, own full IR lifecycle (detection to post-incident review), maintain IR plans/playbooks, coordinate with SOC/threat intel/engineering, support digital forensics, and apply cloud and AI security practices to improve detection and response.
Top Skills:
AIAutomationAutopsyAWSCspmFtkMagnet AxiomNistPicerlSIEMVelociraptorVolatility

Let Your Resume Do The Work
Upload your resume to be matched with jobs you're a great fit for.
Success! We'll use this to further personalize your experience.
Top Companies Hiring Remote Cybersecurity + IT Roles
See All






Popular Job Searches
All Filters
Total selected ()
No Results
No Results
