

Maximum of 25 job preferences reached.
Top Cybersecurity Jobs in Boston, MA

Artificial Intelligence • Hardware • Software • Quantum Computing
Lead design and customer engagements to make networks quantum-safe: inventory cryptography, design migration paths to PQC and hybrid key exchange, run proofs-of-concept (including QKD where relevant), produce reference architectures and playbooks, influence standards, and provide technical authority across sales, product, and engineering.
Top Skills:
CiscoConfig-As-CodeCrypto-AgilityFortinetIpsecJuniperKey ManagementMacsecNetwork TelemetryNokiaPalo AltoPkiPost-Quantum CryptographyPqcPythonQkdTlsVpnZero Trust
Cloud • Software • Cybersecurity
Leads RapidFort’s cybersecurity, risk, compliance, and assurance programs. Owns the ISO 27001 ISMS, SOC 2 Type 2, FedRAMP authorization, and CMMC Level 2 programs; directs security monitoring, incident response, vulnerability management, identity governance, penetration testing, vendor risk, and security architecture. Reports risk to executive leadership and the Audit Committee, manages customer security assurance, oversees a compliance specialist, and serves as incident commander for declared security events.
Top Skills:
Cmmc Level 2Container Image ScanningContinuous Control MonitoringDependency ScanningFedrampIso 27001MfaNist Sp 800-171Nist Sp 800-53Privileged Access ManagementSastSecrets DetectionSIEMSoc 2 Type 2

Cloud • Information Technology • Productivity • Security • Software
Leads AI governance and cybersecurity risk advisory engagements for large, regulated organizations. Advises C-suite executives and boards on AI threats, regulatory requirements, governance operating models, risk assessments, control frameworks, and cyber resilience. Owns complex engagement delivery, client relationships, team leadership, business development, proposals, engagement economics, and practice growth. Develops methodologies, thought leadership, and risk-management solutions covering AI governance, cloud security, identity management, data protection, incident response, and third-party risk.
Top Skills:
Ai GovernanceAicpa Soc 2Cis ControlsCloud SecurityCobitCsa CcmData ProtectionEu Ai ActFfiecGdprHipaaHitrustIdentity And Access ManagementIso 27001Iso 27002Iso/Iec 42001It Risk ManagementModel Risk ManagementNist Ai RmfNist Csf 2.0Nist Sp 800-171Nist Sp 800-30Nist Sp 800-53Third-Party Risk Management

Cybersecurity
Owns the FedRAMP-authorized AWS GovCloud environment, ensuring reliability, security, compliance, patching, vulnerability remediation, continuous monitoring, deployments, hardening, audits, incident response, and on-call support. The role requires hands-on Kubernetes, AWS, infrastructure-as-code, CI/CD, vulnerability management, automation, and regulated-environment experience, while collaborating with SRE and security teams.
Top Skills:
AnsibleAws GovcloudCloudFormationFips-Validated CryptographyGithub ActionsGoJenkinsKubernetesNessusOpenscapPythonQualysRubySIEMTenableTerraform
Artificial Intelligence • Healthtech
Designs, implements, and operates Azure-native security controls for identity, networking, and workloads. Manages Defender for Cloud and Microsoft Sentinel, implements Conditional Access, MFA, and Zero Trust patterns, embeds security into Infrastructure-as-Code pipelines, monitors cloud posture, supports incident response, drives remediation, and maintains compliance documentation and metrics. Partners with cloud and infrastructure security teams to ensure secure, resilient, and compliant Azure environments.
Top Skills:
Conditional AccessInfrastructure As CodeAzureMicrosoft Defender For CloudMicrosoft SentinelMulti-Factor AuthenticationPolicy As CodeZero Trust
New
Cut your apply time in half.
Use ourAI Assistantto automatically fill your job applications.
Use For Free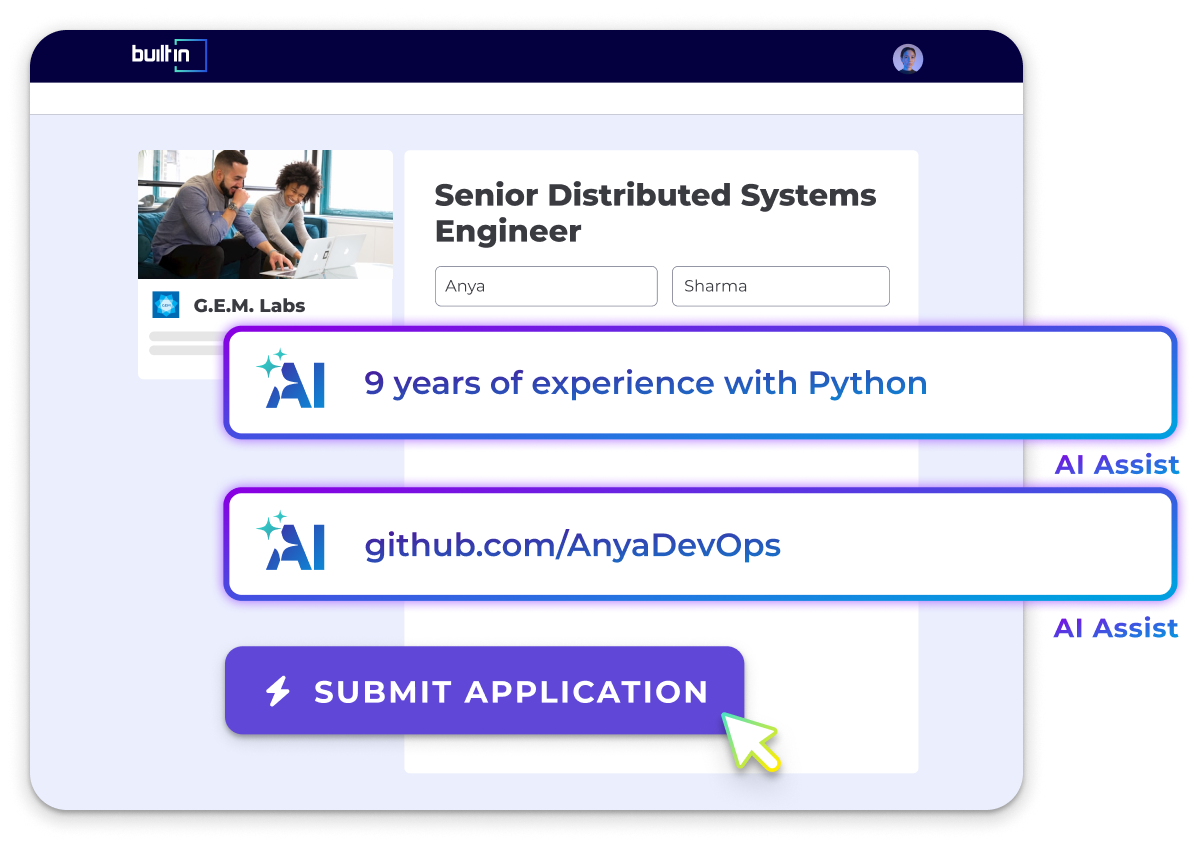
Information Technology
Leads Carina’s cloud infrastructure, internal IT, cybersecurity, risk management, compliance, and business continuity programs. Oversees AWS platform operations, infrastructure as code, deployment reliability, observability, incident response, disaster recovery, employee technology, identity systems, vendors, budgets, and governance. Advises executives on technology strategy, security posture, operational risk, and investments while partnering with Engineering and Data to provide a secure, reliable technology foundation.
Top Skills:
AWSAzureCdn/WafCi/CdCloud NetworkingEndpoint ManagementIdentity And Access ManagementInfrastructure As CodeManaged DatabasesMicrosoft 365Monitoring And AlertingObservabilityTerraform
Information Technology • Professional Services • Consulting • Cybersecurity
Lead SOC 2 and IT compliance engagements, including ITGC and application control testing, walkthroughs, documentation, control-gap analysis, and remediation recommendations. Review junior team members’ work, manage client communication, provide progress updates, and escalate issues. The role requires 3–4 years of IT audit experience, SOC 2 knowledge, bilingual English and Japanese communication, and a relevant bachelor’s degree. Experience with GRC tools, cloud environments, and professional certifications is preferred.
Top Skills:
AWSAzureCmmcDrataFedrampGCPGrcHipaaHitrustIso 27001ItgcPci DssSecureframeSoc 1Soc 2Vanta

Agency • Information Technology
Manages enterprise information security governance, risk, and compliance initiatives. Develops security policies and frameworks, leads data classification and threat modeling, conducts risk assessments, oversees vulnerability remediation, evaluates security controls, supports audits, and prepares risk metrics and executive reports. Partners with technical teams to embed security requirements and promotes governance best practices across the organization.
Top Skills:
Audit ReadinessCompliance ManagementCybersecurityData ClassificationInformation Security GovernanceRisk AssessmentSecurity ControlsSecurity DashboardsSecurity FrameworksThreat ModelingVulnerability Management

Artificial Intelligence • Software
Investigate fraud and insider-threat cases from initial signal through resolution. Gather and analyze logs, transactions, behavioral signals, and other evidence; triage alerts; reconstruct events; document findings objectively; maintain evidence chain of custody; and collaborate with Detection & Response, Legal, and HR. The role also contributes to investigation playbooks, detection improvements, and fraud and insider-risk prevention.
Top Skills:
DlpE-Discovery And Forensics ToolingPythonSIEMSQLUeba
Insurance • Software
Leads and matures the information security assurance program across governance, control frameworks, audits, regulatory response, PCI DSS, third-party risk, policy governance, security awareness, automation, and executive reporting. Manages a multidisciplinary team, oversees GRC platform operations, improves control testing and evidence collection, and partners with business, technology, regulators, auditors, and senior leadership to strengthen security posture and compliance.
Top Skills:
ArcherAuditboardCis ControlsFdicHipaaMetricstreamNist Cybersecurity FrameworkNydfs Part 500OnetrustPci DssServicenow Irm

Let Your Resume Do The Work
Upload your resume to be matched with jobs you're a great fit for.
Success! We'll use this to further personalize your experience.
Top Companies in Boston, MA Hiring Cybersecurity Roles
See All





Popular Job Searches
All Filters
Total selected ()
No Results
No Results
