

Maximum of 25 job preferences reached.
Top Cybersecurity Jobs in Boston, MA

Healthtech
Reviews and investigates security events, phishing reports, malware detections, and brand-monitoring alerts as a Tier 2 SOC analyst. Escalates incidents, supports containment and eradication, leads remediation, mentors junior analysts, documents procedures, and collaborates with security and IT teams across a multinational organization to improve threat detection and response capabilities.
Top Skills:
EdrIds/IpsSIEMSoarWaf
Software
Own the FedRAMP Moderate authorization and security compliance program, including SSP maintenance, POA&M management, continuous monitoring, 3PAO assessments, incident reporting, agency relationships, and change-impact reviews. Partner with engineering, DevOps, legal, and federal customers to maintain authorization and remediate findings. Improve compliance operations through automation, scripting, AI-assisted workflows, infrastructure-as-code, and compliance-as-code. Translate evolving NIST, FedRAMP, OMB, CISA, and AI governance requirements into actionable direction.
Top Skills:
AIAws GovcloudAzure GovernmentCompliance-As-CodeDevsecopsDisa StigsFedrampGoogle Cloud PlatformGrc PlatformsInfrastructure-As-CodeLlmsNist Ai Risk Management FrameworkNist Sp 800-53 Rev. 5Oscal

Healthtech • Software • Pharmaceutical • Manufacturing
Lead the enterprise vulnerability management and continuous threat exposure program across cloud, on-premises, endpoint, application, and product environments. Oversee scanning, vulnerability triage, risk prioritization, remediation tracking, SLA management, automation, executive reporting, compliance metrics, and incident-related exposure analysis. Partner with engineering and IT operations teams to reduce security risk and improve vulnerability management processes.
Top Skills:
AWSAzureCisa KevCvssEpssFrontier Ai ModelsLinuxPowershellPythonQualysRapid7TenableWindowsWiz
Healthtech • Biotech
Supports IT SOX audits, IT general controls, system documentation, access governance, role and entitlement management, account cleanup, policy development, and remediation tracking. The role partners with IT, InfoSec, Internal Audit, and business stakeholders to strengthen least-privilege access, maintain system hygiene, and ensure compliance in a regulated environment.
Top Skills:
Active DirectoryCoupaNetSuiteOkta

Artificial Intelligence • Insurance • Cybersecurity
Lead cyber incident response engagements from scoping through recovery across multi-system environments. Coordinate claims teams, breach counsel, forensic providers, policyholders, and other stakeholders; oversee investigations, manage timelines and scope creep, translate forensic findings for technical, legal, and executive audiences, and handle legally sensitive materials. The role also contributes to incident response methodologies, playbooks, and tooling.
Top Skills:
Digital Forensics And Incident Response (Dfir)
New
Cut your apply time in half.
Use ourAI Assistantto automatically fill your job applications.
Use For Free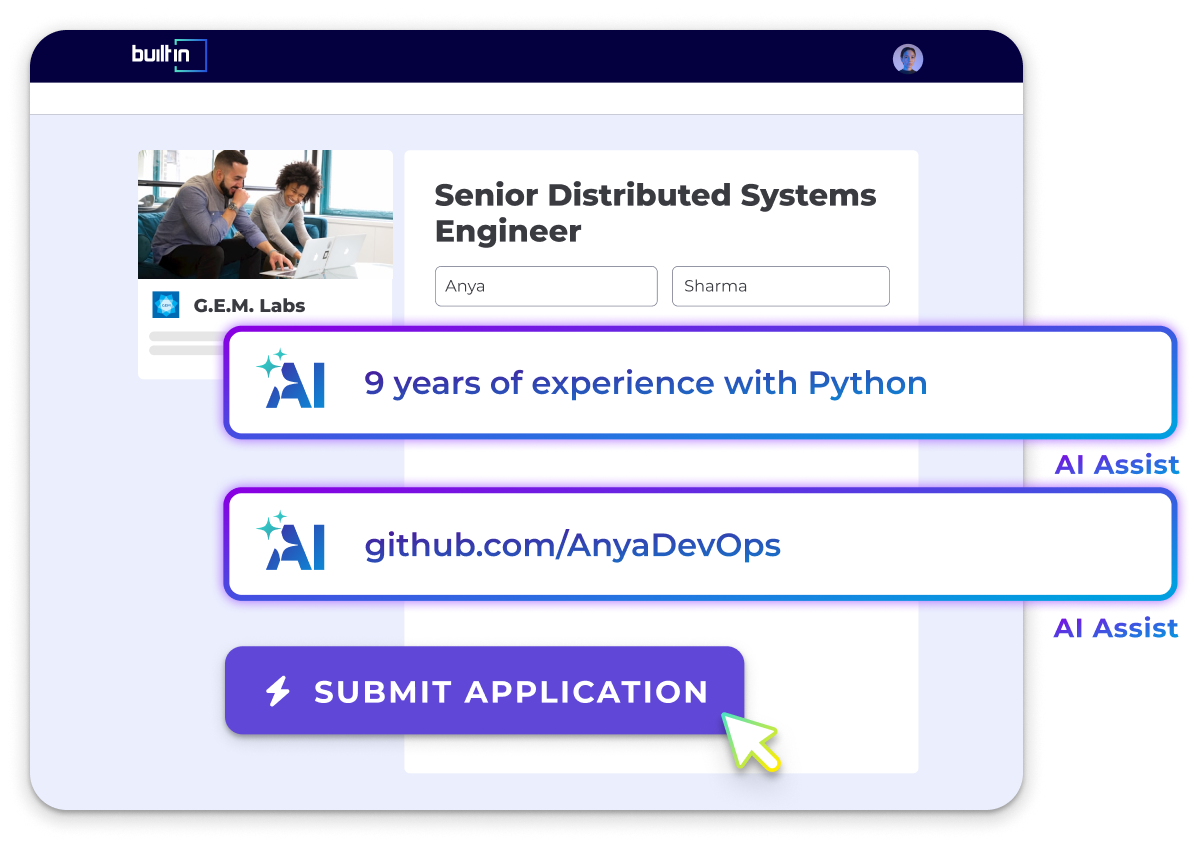

Information Technology • Consulting
Designs and maintains secure CI/CD pipelines, integrates automated security controls and testing, supports containerized and cloud-native environments, and performs vulnerability management, remediation, security assessments, and incident response. Collaborates with development, security, architecture, and operations teams to resolve risks and documents DevSecOps processes and integrations for a federal government client.
Top Skills:
Automated Build And DeploymentAutomated Security TestingCi/Cd PipelinesCloud SecurityCloud-Native EnvironmentsContainerizationCybersecurityDevsecopsGitInfrastructure-As-CodeSecurity-As-CodeVersion Control
Aerospace • Defense
Own and advance cybersecurity for satellites, flight software, ground systems, mission networks, communication links, and AWS infrastructure. Responsibilities include security architecture, threat modeling, vulnerability management, incident response, IAM, SIEM detection engineering, network defense, cloud security, DLP, security assessments, awareness training, and compliance with CMMC Level 2, NIST 800-171, and ITAR/EAR requirements. The role collaborates with aerospace, software, systems, and compliance teams and requires expertise in mission-system security.
Top Skills:
AWSAws ConfigAzure AdCloudFormationCloudtrailCmmcDlpEarElasticEmbedded SystemsGuarddutyIamIds/IpsIso 27001ItarMicrosoft SentinelNist 800-171OktaRf SecurityS3Satellite Communication ProtocolsSIEMSoc 2SplunkTerraformVpcVpn

Artificial Intelligence • Machine Learning • Software
Leads the IAM function and develops security strategies, standards, architectures, and operations for user, machine, and privileged identities. Oversees IAM, PAM, IGA, and secrets management solutions across hybrid environments; automates account lifecycle and access provisioning; secures Microsoft 365; partners with technology and product teams; measures compliance; and provides tier 2/3 support for identity technologies.
Top Skills:
Cloud EnvironmentsIdentity And Access Management (Iam)Identity Governance And Administration (Iga)Microsoft 365On-Premises EnvironmentsPrivileged Access Management (Pam)Secrets Management

Computer Vision • Security
Lead execution for BloodHound Enterprise SaaS features by partnering with product and engineering teams, synthesizing customer and market feedback, writing product requirements and user stories, supporting release readiness, and assisting go-to-market and enablement activities to improve defensive attack path management for Active Directory environments.
Top Skills:
Active DirectoryApi StandardsAzureBloodhound CeBloodhound EnterpriseCloud TechnologiesEntraSaaS

Aerospace • Information Technology • Security • Cybersecurity • Defense
Leads OT/ICS and enterprise cybersecurity architecture for a federal critical-infrastructure modernization program. Responsibilities include requirements development, NERC CIP traceability, market research, RFI and vendor evaluation, lab testing, alternatives analysis, product recommendations, and executive briefings. The role bridges utility operational technology and IT security, covering access control, monitoring, asset management, vulnerability management, SCADA environments, and industrial systems. It is fully remote in the U.S. with up to 25% domestic travel and requires Public Trust eligibility.
Top Skills:
Cisa Zero Trust ArchitectureConfiguration ManagementCyber-Asset ManagementData DiodesDodafEnterprise It CybersecurityFismaIcsIdentity And Access ManagementIndustrial ProtocolsLog MonitoringNerc CipNetwork MonitoringNist RmfOtPacket CapturePatch ManagementPivPrivileged Access ManagementProtective RelaysRtusScadaThreat VisibilityVulnerability Management

Let Your Resume Do The Work
Upload your resume to be matched with jobs you're a great fit for.
Success! We'll use this to further personalize your experience.
Top Companies in Boston, MA Hiring Cybersecurity Roles
See All






Popular Job Searches
All Filters
Total selected ()
No Results
No Results
