

Superhuman offers a dynamic hybrid working model for this role. This flexible approach gives team members the best of both worlds: plenty of focus time along with in-person collaboration that builds trust, sparks innovation, and strengthens team culture.
About SuperhumanGrammarly is now part of Superhuman, the AI productivity platform on a mission to unlock the superhuman potential in everyone. The Superhuman suite of apps and agents brings AI wherever people work, integrating with over 1 million applications and websites. The company’s products include Grammarly’s writing assistance, Superhuman Docs’ collaborative workspaces, Mail’s inbox management, and Go, the proactive AI assistant that understands context and delivers help automatically. Founded in 2009, Superhuman empowers over 40 million people, 50,000 organizations, and 3,000 educational institutions worldwide to eliminate busywork and focus on what matters. Learn more at superhuman.com.
The OpportunityWe're looking for a Security Engineer to join our Detection & Response Team to achieve our ambitious goals. This role will contribute to our D&R team as hands-on practitioner across incident response, detection engineering, threat hunting, and threat intelligence. You'll plan, execute, and debrief complex security operations, leveraging those insights to enhance our threat mitigation capabilities and build robust, automated security tooling across all Superhuman environments.
Additionally, you'll own key workstreams in executing and advancing our security vision, translating strategic objectives into tactical implementations through strong technical execution and innovative solution building, with particular emphasis on automation and AI-powered security solutions. You'll conduct research across security domains and automation technologies, identifying opportunities to enhance our capabilities through cutting-edge approaches and intelligent automation. Finally, you'll bring an attacker mindset into Superhuman’s engineering and security culture, thinking like a threat actor to defend our systems in a way that is grounded in how real attacks happen.
Superhuman's engineers and researchers have the freedom to innovate and uncover breakthroughs—and, in turn, influence our product roadmap. The complexity of our technical challenges is growing rapidly as we scale our interfaces, algorithms, and infrastructure. Curious how we build and operate our AI agents? Check out our engineering blog, and explore our threat-hunting AI here.
As a Security Engineer, you will:
Own the IR strategy end-to-end, building, maintaining, and operating the systems and tooling that strengthen our ability to detect, contain, and recover from security incidents at scale
Build and maintain automated threat detection systems, AI-driven alert triage solutions, and security intelligence pipelines that scale with business growth
Conduct threat hunting and detection engineering, developing detection-as-code, hunting-as-code, and intelligence-as-code capabilities.
Research and develop cutting-edge security automation and AI-powered security solutions to deepen and scale our ability to identify threats, including autonomous security agents.
Operate without traditional scope limitations, following attacker kill chains to uncover security gaps that scoped teams miss.
Lead complex security investigations, including insider threat scenarios and sophisticated attack campaigns.
Maintain incident response capabilities and serve as part of the Incident Command on-call schedule.
Embed attacker mindset thinking throughout the organization through education and collaboration with engineering teams.
Has 3+ years of relevant experience in security engineering, with expertise across multiple disciplines including incident response and detection engineering (threat intelligence, threat hunting experience is nice to have too)
Proven incident response leadership and complex security investigation experience.
Automation and development skills in Python, Go, or similar languages, with experience building production security tooling.
Knowledge of cloud security architecture.
Research mindset with an ability to identify novel attack vectors and develop creative, pragmatic solutions.
Thrives in ambiguous environments and can deliver meaningful results at a rapid pace while managing multiple competing priorities.
Has a demonstrated ability to work independently with minimal guidance, proactively manages tasks and priorities across multiple projects, analyzes and executes work efficiently, collaborates effectively with cross-functional teams, and thrives in fast-paced, results-driven environments.
Nice to have:
Experience with CI/CD security integration, identity and access management concepts, and security orchestration.
Experience with large-scale Kubernetes clusters.
Background in AI/ML applications for security, including experience with or interest in developing autonomous security systems.
Professional Growth: We believe that autonomy and trust are key to empowering our team members to do their best, most innovative work in a way that aligns with their interests, talents, and well-being
A connected team: Superhuman builds a product that helps people connect, and we apply this mindset to our own team. Our remote-first, hybrid model enables a highly collaborative culture rooted in our values. We work to foster belonging among team members in a variety of ways. This includes our team member resource groups, Superhuman Circles, which promote connection among those with shared identities including BIPOC and LGBTQIA+ team members, women, and parents. We also celebrate our colleagues and accomplishments with global, local, and team-specific programs.
Comprehensive benefits for candidates based in Germany and Ukraine: Superhuman offers all team members competitive pay along with a benefits package encompassing life care (including mental health care and risk benefits) and ample and defined time off. We also offer support to set up a home office, wellness and pet care stipends, learning and development opportunities, and more.
Relocation Support (available for Berlin only): Superhuman provides relocation support to make your move to Berlin seamless. Our package includes visa assistance, destination services to help you and your family settle in comfortably, and a relocation bonus to cover additional expenses, such as temporary housing.
At Superhuman, we value our differences, and we encourage all—especially those whose identities are traditionally underrepresented in tech organizations—to apply. Superhuman is an equal opportunity company. We do not discriminate on the basis of race or ethnic origin, religion or belief, color, gender expression or identity, sexual orientation, sexual identity, national origin, citizenship, age, marital status, veteran status, disability status, criminal prosecution, judgment in a criminal case, or any other characteristic protected by law.
For more details about the personal data Superhuman collects during the recruitment process, for what purposes, and how you can address your rights, please see the Superhuman Data Privacy Notice for Candidates here.
Skills Required
- 3+ years of relevant experience in security engineering
- Expertise in incident response and detection engineering
- Incident response leadership and complex security investigation experience
- Automation and development skills in Python, Go, or similar languages
- Experience building production security tooling
- Knowledge of cloud security architecture
- Research mindset and ability to identify novel attack vectors
- Ability to work independently and manage multiple competing priorities
- Experience with threat intelligence and threat hunting
- Experience with CI/CD security integration
- Knowledge of identity and access management concepts
- Experience with security orchestration
- Experience with large-scale Kubernetes clusters
- Background in AI/ML applications for security
- Experience or interest in developing autonomous security systems
What the Team is Saying


What We Do
Superhuman (formerly Grammarly) is the AI productivity platform on a mission to unlock the superhuman potential in everyone. The Superhuman suite of apps and agents brings AI wherever people work, integrating with over 1 million applications and websites. The company’s products include Grammarly’s writing assistance, Docs’ connected surface for teams, Mail’s inbox management, and Go, the proactive AI assistant that understands context and delivers help automatically. Superhuman empowers over 40 million people, 50,000 organizations, and 3,000 educational institutions worldwide to eliminate busywork and focus on what matters. Learn more at superhuman.com.
Why Work With Us
Our teams are dedicated to building technology to help people do and be their best. That takes bold optimism, purpose, and the drive to do hard things well. If you’re all in on shaping what’s next—and building it with care—come join us.
Gallery
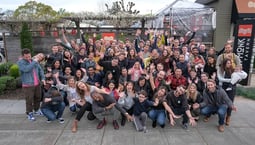


Superhuman Offices
Hybrid Workspace
Employees engage in a combination of remote and on-site work.
