Finding the right tool kit for a cybersecurity team is no easy task, but the experts at TransUnion, Alliant Credit Union and Caliola Engineering have some tips.
For the cybersecurity team at information technology company TransUnion, a tech stack is an ever-evolving ecosystem that goes through a rigorous vetting process.
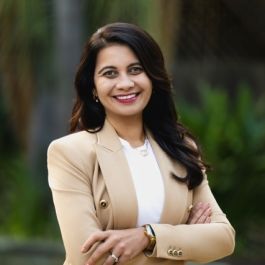
“We evaluate tooling the same way we evaluate risk; by asking what residual exposure it leaves behind, not just what debt or gap it claims to close,” Swathi Joshi, senior vice president of cyber defense, said.
A tool earns its place in their stack only if it measurably improves their ability to detect, contain or anticipate threats — not because it’s well-marketed or popular elsewhere in the industry.
At Alliant Credit Union, a banking and fintech company, the cybersecurity team has a similar approach to evaluation.
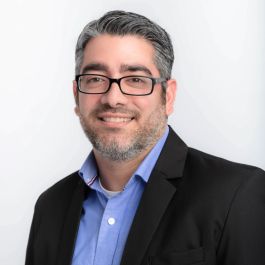
“At Alliant, we don’t adopt technology simply because it’s new,” Chief Information Security Officer Mohamad Tayba said. “We evaluate security tools through the lens of risk reduction, operational efficiency, user experience and business value.”
For national defense companies like Caliola Engineering, Tony, an IT and cybersecurity specialist, explained their “practical, risk-based” approach to security tooling.
“We look at how well a tool addresses a real security need, how it integrates with our existing environment, whether it supports our compliance requirements and how manageable it will be for both administrators and users,” Tony said.
We spoke with the three cybersecurity professionals to learn more about the tools, systems and processes their cybersecurity teams use to detect threats, reduce risk and respond faster.

Caliola Engineering develops secure, resilient communication technologies that support mission-critical operations for national defense.
What’s it like to work on the cybersecurity team at your company?
Working on Caliola’s cybersecurity team is fast-paced and extremely rewarding. We’re responsible for protecting company systems, data and users while also making sure we meet security and compliance requirements. Every day can be different — one day may involve investigating an alert and the next might be improving policies, hardening systems or helping employees understand security risks.
What tools or technologies help your team protect the company and its customers?
We use a combination of security, monitoring, identity and compliance technologies to protect Caliola and its customers. These include endpoint protection, firewalls, multi-factor authentication, security monitoring and alerting, email security, vulnerability management and data protection tools.
What should candidates know about how your team evaluates, adopts or improves security tooling?
Our team takes a practical, risk-based approach to security tooling. We look at how well a tool addresses a real security need, how it integrates with our existing environment, whether it supports our compliance requirements and how manageable it will be for both administrators and users.
TransUnion is a global information and insights company.
What’s it like to work on the cybersecurity team at your company?
Working on our cyber defense team means operating with an anticipatory mindset, not a reactive one. We ask ourselves constantly: Are we positioned to see a threat before it becomes an incident, or are we just getting faster at cleaning up after one? That question shapes how we hire, how we organize and how we hold ourselves accountable.
We’ve unified our defensive functions, security operations center, incident response, threat intelligence, forensics and threat hunting, under one operating model so knowledge flows freely instead of getting stuck in silos. Teams train like they fight — no sanitized tabletop exercises, because readiness has to be tested under real conditions to mean anything.
We also believe security should be a trusted partner to the business, not a gatekeeper. That means transparency when things go wrong, metrics that speak the language of the business and giving people the autonomy to own outcomes rather than just execute tasks. For candidates, that translates into real influence, faster growth and work that visibly protects our customers.
What tools or technologies help your team protect the company and its customers?
We think of detection not as a collection of alerts, but as a system that manufactures signals, continuously ingesting, correlating and refining telemetry across identity, network, device and application layers so we can spot patterns a human alone would miss. That systems mindset lets us move from reactive triage toward a genuinely anticipatory security posture.
AI has become a force multiplier on both sides of this equation and we’re intentional about staying ahead. We use it to automate enrichment and triage, chain telemetry into context-rich insight and free our analysts to focus on judgment rather than manual correlation. But human-in-the-loop is non-negotiable for us. Every AI-driven finding or recommended action goes through governance and human validation before it acts on anything that matters.
Underneath the technology, our real advantage is architecture. We build shared platforms, detection libraries, automation, threat intel, once and let every team draw from them, rather than solving the same problem repeatedly. That horizontal approach is what lets us scale protection without scaling headcount at the same rate.
What should candidates know about how your team evaluates, adopts or improves security tooling?
We evaluate tooling the same way we evaluate risk; by asking what residual exposure it leaves behind, not just what debt or gap it claims to close. A tool earns its place in our stack only if it measurably improves our ability to detect, contain or anticipate threats, not because it’s well-marketed or popular elsewhere in the industry.
Every new capability, especially anything AI-driven, goes through a governance-first process. We define clear success metrics upfront, validate outputs before trusting them and require human review for anything touching high-risk decisions. We track effectiveness the same way we track detection health, false positive and negative rates, coverage improvement and measurable impact on time-to-detect and time-to-contain.
Candidates should know this isn’t a static checklist, it’s a living discipline. We continuously revisit what’s in our stack and retire what no longer earns its keep. If you enjoy shaping how an organization thinks about tooling, not just operating what’s handed to you, you’ll have real room to influence that here.
Alliant Credit Union provides banking, loans and investment services to members nationwide.
What’s it like to work on the cybersecurity team at your company?
The cybersecurity team at Alliant is focused on more than protecting systems. We help enable the business to innovate securely while safeguarding the trust our members place in us every day. Our team works across cybersecurity, fraud management, technology and business functions to solve challenges using modern security tools; we’re also transforming how cybersecurity operates by leveraging automation to eliminate repetitive tasks and applying AI to enhance threat detection, risk management and decision-making. We foster a culture of collaboration, continuous learning and innovation, giving team members opportunities to make a meaningful impact while helping shape the future of cybersecurity in a rapidly changing digital environment.
What tools or technologies help your team protect the company and its customers?
At Alliant, we utilize modern security technologies to provide visibility across our environment and defend against evolving threats. Beyond those tools, we're investing heavily in automation and AI-powered capabilities to augment our teams, reduce manual effort and improve both the speed and quality of our security operations. From threat detection and incident response to risk management, automation and AI are helping us work smarter and focus our talent on the areas where human expertise delivers the greatest value. We believe the future of cybersecurity is the combination of skilled professionals and intelligent technology working together to deliver stronger protection, greater resilience and better outcomes for our members.
What should candidates know about how your team evaluates, adopts or improves security tooling?
At Alliant, we don’t adopt technology simply because it’s new. We evaluate security tools through the lens of risk reduction, operational efficiency, user experience and business value. Our goal is to build a security ecosystem that not only protects the organization but also enables innovation and growth. For candidates, that means joining a team that embraces innovation and isn’t afraid to challenge traditional approaches. We encourage our professionals to help shape the future of our security program by identifying opportunities to improve processes, automate workflows, leverage AI and adopt technologies that enhance both security and the overall employee experience.